 InfoSecBulletin Cybersecurity for mankind
Palo Alto Networks released a security advisory about a new vulnerability in its Cortex XDR Broker Virtual Machine (VM). CVE-2026-0231 is a medium-severity flaw that could let an attacker access and change sensitive system information.
Because the Broker VM acts as a critical bridge between on-premises network assets and the cloud-based Cortex XDR platform, securing this component is vital for maintaining an organization’s overall defensive posture.
Japan banking crisis
Outage causes disruption at 128 japan banks: preventing ATM transaction

Daily Cyber security update for 06.11. 2026

Cyber attack causes French bank Credit Mutuel Arkea €100 million missing

OpenAI AI Pipeline Discovers 948 Linux Kernel Privilege Escalation Flaws in 30 Hours

Bangladeshi Researcher Rasel Earns First Apple CVE Recognition for Model I/O Flaw

WinRAR, WordPress RCE flaw & Zyxel GS1900 Zero-Day exploited in the wild

Daily Cyber security update for 04.11. 2026

Daily Cyber security update for 03.11. 2026

Using ARTEX AI, Hacker to attack 200 Organizations Across 14 Countries

Amadeus cyber incident impacted “Cathay Pacific, Qantas, Japan, Malaysia, Korean & Asiana” Airlines

Understanding the Vulnerability
Palo Alto Network’s said, it is an information disclosure vulnerability in Palo Alto Networks Cortex XDR® Broker VM which allows an authenticated user to obtain and modify sensitive information by triggering live terminal session via Cortex UI and modifying any configuration setting. But the attacker must have network access to the Broker VM to exploit this issue.
Palo Alto Networks discovered this vulnerability through their security research. The vendor confirmed there are no known cases of it being exploited maliciously.
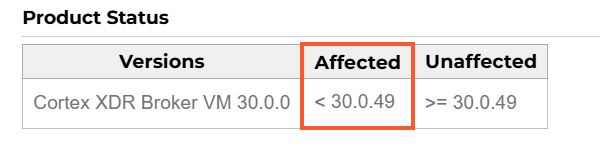
The exploit maturity is unreported, meaning no public exploit code or proof-of-concept is available in the hacker community. The vulnerability is isolated to specific versions of the software. Cortex XDR Broker VM branch versions prior to 30.0.49 are vulnerable.
According to Palo Alto Network, the issue affects all installations within this range, as no specific or unusual system configuration is required to trigger the exposure.
Mitigations and Solutions:
The only reliable defense is to apply the official vendor patch, as there are no known temporary fixes to prevent exploitation. Network administrators should immediately implement the following steps:
Update affected systems to Cortex XDR Broker VM version 30.0.49 or a later release.
Verify if automatic upgrades are enabled on your Broker VM; if so, the patch will be applied automatically without manual intervention.
Enable automatic upgrades if they are currently disabled to ensure that all future security patches are delivered and installed without delay.



