Friday , November 6 2026
SharePoint

Microsoft patches SharePoint RCE flaw CVE-2026-45659 across servers

Microsoft patches to fix a security flaw in SharePoint. This issue could let hackers run harmful code without needing special conditions. The flaw, dubbed CVE-2026-45659, has a CVSS score of 8.8. It is rated as a serious issue.

“Deserialization of untrusted data in Microsoft Office SharePoint allows an authorized attacker to execute code over a network,” Microsoft said in an advisory released last week.

Daily Cyber security update for 06.11. 2026
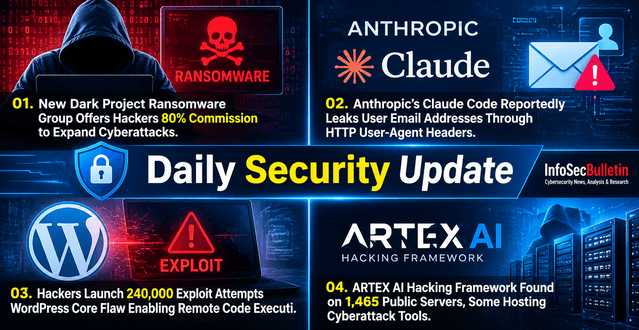
Cyberattacks are rising around the world, including ransomware, malware, data leaks, and hacked websites. These events show how complex and...
Read More
Daily Cyber security update for 06.11. 2026

Cyber attack causes French bank Credit Mutuel Arkea €100 million missing

French lender Credit Mutuel Arkea said on Thursday hackers had stolen around €100 million ($112.61 million) in a cyber heist...
Read More
Cyber attack causes French bank Credit Mutuel Arkea €100 million missing

OpenAI AI Pipeline Discovers 948 Linux Kernel Privilege Escalation Flaws in 30 Hours

OpenAI says that an automated system found and confirmed 948 different Linux kernel security issues in one run. These flaws...
Read More
OpenAI AI Pipeline Discovers 948 Linux Kernel Privilege Escalation Flaws in 30 Hours

Bangladeshi Researcher Rasel Earns First Apple CVE Recognition for Model I/O Flaw

Apple credits Md Rasel Bhuyan and fellow researcher Musaab Khan for discovering an out-of-bounds write vulnerability affecting multiple Apple operating...
Read More
Bangladeshi Researcher Rasel Earns First Apple CVE Recognition for Model I/O Flaw

WinRAR, WordPress RCE flaw & Zyxel GS1900 Zero-Day exploited in the wild

A flaw in Zyxel GS1900 switches was being used by hackers, and the update to fix it did not work....
Read More
WinRAR, WordPress RCE flaw & Zyxel GS1900 Zero-Day exploited in the wild

Daily Cyber security update for 04.11. 2026

Cyberattacks are rising around the world, including ransomware, malware, data leaks, and hacked websites. These events show how complex and...
Read More
Daily Cyber security update for 04.11. 2026

Daily Cyber security update for 03.11. 2026

Cyberattacks are rising around the world, including ransomware, malware, data leaks, and hacked websites. These events show how complex and...
Read More
Daily Cyber security update for 03.11. 2026

Using ARTEX AI, Hacker to attack 200 Organizations Across 14 Countries

Hackers used ARTEX, a free tool for testing security with AI, to attack over 200 organizations in 14 countries. The...
Read More
Using ARTEX AI, Hacker to attack 200 Organizations Across 14 Countries

Amadeus cyber incident impacted “Cathay Pacific, Qantas, Japan, Malaysia, Korean & Asiana” Airlines

A cybersecurity incident with Spanish travel tech company Amadeus IT Group has worried the global airline industry. Hackers got into...
Read More
Amadeus cyber incident impacted “Cathay Pacific, Qantas, Japan, Malaysia, Korean & Asiana” Airlines

Multiple European supermarket fridges got hacked: Temperatures reached high as 55°C

A cyberattack on refrigeration systems has affected stores of many supermarket chains in various European countries. Hackers changed the temperature...
Read More
Multiple European supermarket fridges got hacked: Temperatures reached high as 55°C

Microsoft said that any unauthenticated attacker could cause the vulnerability and it does not need admin or higher permissions.

“In a network-based attack, an authenticated attacker, who has a minimum of Site Member permissions (PR:L), could execute code remotely on the SharePoint Server,” the Windows maker added.

Microsoft thanked a researcher called MEOW for finding and reporting the problem. Updates have been given for these versions –

SharePoint Server Subscription Edition
SharePoint Server 2019
SharePoint Enterprise Server 2016

Last month, Microsoft fixed a security issue with SharePoint Server that allowed fake identities. This flaw, listed as CVE-2026-32201 and rated 6.5 on the CVSS scale, was known to be taken advantage of in real attacks.

The tech giant says CVE-2026-45659 is less likely to be used against users, but it’s still important for users to fix it for better safety. This is especially true because many problems in the platform have often been targeted by attackers in the past.


Check Also

SMS of Death

‘SMS of Death’ Zero-Click Flaw Disrupting Android Phones With a Single Text

A security expert shared information about a zero-click Android bug known as “SMS of Death.” …