InfoSecBulletin Cybersecurity for mankind
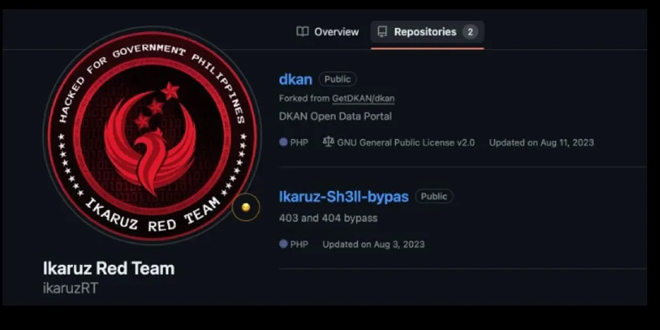
SentinelOne researchers found that the Ikaruz Red Team is targeting the Philippines government using different ransomware builders like LockBit, Vice Society, Clop, and AlphV to carry out “small-scale” attacks. They are also sharing data leaks from various organizations in the Philippines.
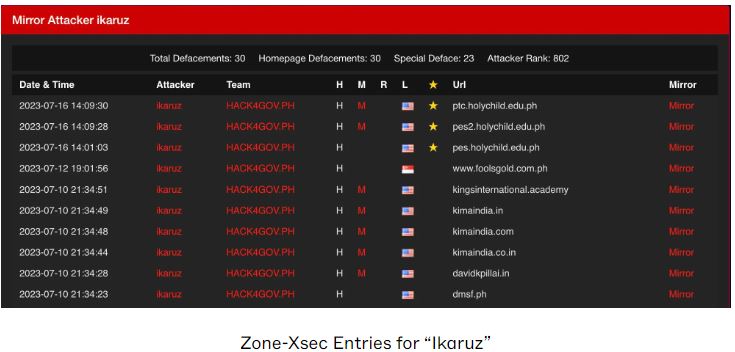
Ikaruz Red Team (IRT) has been targeting entities in the Philippines through defacements, small-scale DDoS attacks, and ransomware attacks. This has been happening between 2023 and present day (2024). Resecurity documented that there is a larger wave of hacktivist groups targeting the region. They mentioned that the tensions with China and the strategic significance of the Philippines in the Indo-Pacific make it an attractive target for those who want to cause civil disruption.
Microsoft’s November 2026 Patch Tuesday addresses 1,093 flaws, with Outlook zero-day

Barracuda ESG flaws exploited, gaining root access

Apple, SAP, and Ivanti Patch Critical flaws Affecting Messaging, Bluetooth, and Enterprise Systems

Jailbroken DeepSeek AI Agent Conducts Two-Week Cyberattack on European Telecom

Daily Cyber security update for 10.11. 2026

IBM fixes 208 API Connect vulnerabilities, 47 critical

89 New ransomware groups emerge in 2026, claiming over 2,200 victims

Daily Cyber security update for 08.11. 2026

Japan banking crisis
Outage causes disruption at 128 japan banks: preventing ATM transaction

Daily Cyber security update for 06.11. 2026

In the past year, there has been a rise in hacktivist attacks in the Philippines. Groups like Robin Cyber Hood, Philippine Exodus (aka PHEDS), Cyber Operations Alliance, and Philippine Hacking University have claimed responsibility for ransomware attacks, misinformation campaigns, and espionage.
On April 8th, the National Privacy Commission (NPC) of the Philippines started investigating a breach of the Department of Science & Technology by a previously unidentified hacktivist group called #opEDSA.
Ikaruz Red Team Ransomware Activity:
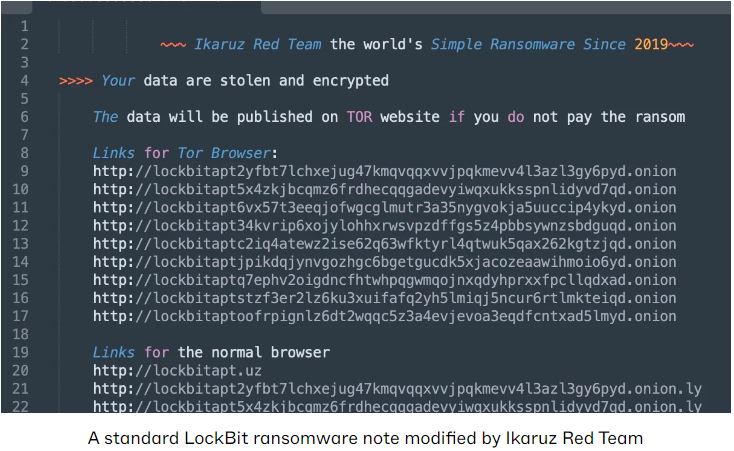
Ikaruz Red Team, previously known for web defacements and nuisance attacks, is now launching small-scale ransomware attacks using leaked LockBit builders. They are distributing modified LockBit 3 ransomware and advertising data leaks from various organizations in the Philippines.
Ikaruz Red Team ransom notes are based on the LockBit template. The only change is the replacement of the LockBit ransomware name with ‘Ikaruz Red Team’ in the top line. By modifying the config.json file before creating the LockBit payloads, this change can be easily made in the ransom notes. Click here to readout the full report.