Sunday , October 11 2026
Fortinet

Fortinet admits data breach after hacker claims to steal 440GB

Fortinet confirmed a data breach after a threat actor claimed to have stolen 440GB of files from its Microsoft SharePoint server.

Fortinet told two international media that, “An individual gained unauthorized access to a limited number of files stored on Fortinet’s instance of a third-party cloud-based shared file drive, which included limited data related to a small number of Fortinet customers, and we have communicated directly with customers as appropriate,”,

Anthropic unveils “OSS Scanner” Free AI Vulnerability Scanner for Open-Source Projects

Anthropic unveiled OSS Scanner on Thursday as an opt-in vulnerability scanner designed to enhance security within the open-source ecosystem through...
Read More
Anthropic unveils “OSS Scanner” Free AI Vulnerability Scanner for Open-Source Projects

Rise on RCE Exploits Targeting Hikvision Camera Flaw

There was a rise in scanning and remote code execution attempts on video surveillance devices in Ukraine from September 21...
Read More
Rise on RCE Exploits Targeting Hikvision Camera Flaw

FortiBleed Attack Compromised 80,000+ Devices, SonicWall Patches 4 SMA1000 Flaws CVSS 10

The FBI and U.S. Secret Service released a joint warning about cybersecurity. The warning said that the FortiBleed campaign is...
Read More
FortiBleed Attack Compromised 80,000+ Devices, SonicWall Patches 4 SMA1000 Flaws  CVSS 10

Critical Atlassian & IBM Flaws Expose Files and Enable Remote Code Execution

Atlassian has fixed CVE-2026-21589, a serious flaw in Atlassian Data Center with a score of 9.3. This bug allows an...
Read More
Critical Atlassian & IBM Flaws Expose Files and Enable Remote Code Execution

Citrix NetScaler SAML 0-Day Flaw Under Attack

Citrix has put out emergency security updates for a NetScaler SAML flaw that hackers are using. Known as CVE-2026-88779, this...
Read More
Citrix NetScaler SAML 0-Day Flaw Under Attack

Major Danish university breached, 200,000 users at risk

Hackers got into the identity and access management system at the Technical University of Denmark (DTU) and downloaded a lot...
Read More
Major Danish university breached, 200,000 users at risk

Microsoft’s X account hijacked to promote Clippy crypto scam

Microsoft's official X account was taken over to promote an unapproved Clippy-themed cryptocurrency. The tech giant’s X account, with 13...
Read More
Microsoft’s X account hijacked to promote Clippy crypto scam

Critical cPanel, GitLab AI Gateway and Dell CSM Flaws Enable RCE And Admin Hijacking

CPanel has put out security updates to fix three problems in cPanel & WHM. These problems could let attackers take...
Read More
Critical cPanel, GitLab AI Gateway and Dell CSM Flaws Enable RCE And Admin Hijacking

Nearly 100,000 email addresses exposed in first AI-related data breach in Singapore

Nearly 100,000 Bee Cheng Hiang customers had their email addresses leaked when an employee used an AI tool to generate...
Read More
Nearly 100,000 email addresses exposed in first AI-related data breach in Singapore

Hackers Exploit Zimbra Mail Servers: TeamViewer patched 5 critical flaws

Hackers to exploit a flaw in Zimbra mail servers that are connected to the Internet. They send special emails that...
Read More
Hackers Exploit Zimbra Mail Servers: TeamViewer patched 5 critical flaws
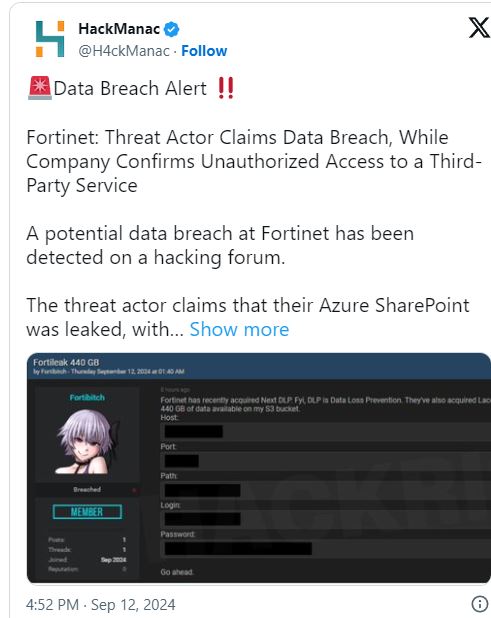
  Source: X

The threat actor, known as “Fortibitch,” claims to have tried to extort Fortinet into paying a ransom, likely to prevent the publishing of data, but the company refused to pay.

In response to questions about incident, Fortinet confirmed that customer data was stolen from a “third-party cloud-based shared file drive.”

Fortinet’s website later stated that less than 0.3% of its customers were affected by the incident, and there was no malicious activity targeting them.

The cybersecurity company confirmed that the incident did not involve data encryption, ransomware, or access to Fortinet’s network.

Cyberdaily.au said, “The incident reportedly affected customers within the Asia-Pacific region. Home Affairs confirmed it was aware of the incident but provided no further details.”

“The National Office of Cyber Security is aware of reports regarding a potential cyber incident impacting Fortinet and stands ready to assist, if required,” it said.


Check Also

JadePuffer

JadePuffer Agentic AI targets and destroys Azure’s cloud resources

The JadePuffer ransomware group is attacking Azure users with agent-based attacks that gather information, steal …