InfoSecBulletin Cybersecurity for mankind
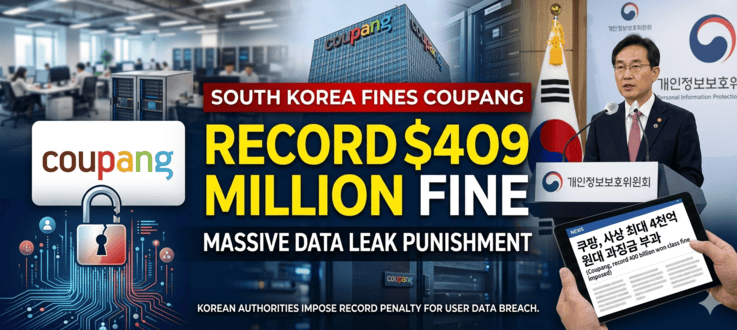
South Korea’s privacy regulator said on Thursday (June 11) that the country will fine e-commerce giant Coupang 625 billion won ($409.30 million) over a massive leak of customer information last year and illegal collection of personal information, in the country’s largest data breach penalty on a company.
The Personal Information Protectin Commission said the New York-listed company had leaked personal data of more than 33 million customers and failed to detect the breach within the 72 hours required by the law.
Bypassing firewalls, AI Agents Accessed Indian ‘ Data Without Permission: CERT-In

MITRE ATT&CK v20 Unveils 9 New Attack Techniques On AI Exploits, MFA Bypass, and CAPTCHA Evasion

Hackers Exploit Fortinet Flaws to Deploy Stealthy PEERSTITCH Malware on FortiGate Firewalls

Hacker stole Meta GitHub repos; Stole Source Code

Urgent patch! Zoom,NVIDIA and IBM Patch 41 Security flaws

Microsoft patches record braking 1411 flaws; 2 zero days

Anthropic unveils “OSS Scanner” Free AI Vulnerability Scanner for Open-Source Projects

Rise on RCE Exploits Targeting Hikvision Camera Flaw

FortiBleed Attack Compromised 80,000+ Devices, SonicWall Patches 4 SMA1000 Flaws CVSS 10

Critical Atlassian & IBM Flaws Expose Files and Enable Remote Code Execution

“This accident occurred due to Coupang’s lack of safety measures and systems, not sophisticated hacking,” Song Kyung-hee, the chairperson of the privacy regulator, told a briefing on Thursday.
“We have decided to impose a total of 624.68 billion won in fines … on Coupang for violating safety obligations and collecting personal data without legal grounds,” a Personal Information Protection Commission statement said.
“Inadequate basic safeguards, including poor management of authentication signing keys and lax access controls” resulted in the personal data of around 37.5 million users being exposed, the commission said.
The fine amounts to 1.4% of Coupang’s revenue of 45 trillion won in 2025, according to Reuters’ calculation. After the fine was announced, Coupang apologised for having caused concern to the public and its customers.
However, the company said that “we regret that our proactive measures to prevent secondary harm from last year’s data leak incident, as well as our explanations based on clear facts, were not sufficiently reflected” in the regulator’s decision.
ShinyHunters claim stolen data from 100+ org via oracle PeopleSoft servers