InfoSecBulletin Cybersecurity for mankind
Fortinet on Monday warned customers that a recently patched vulnerability, tracked as CVE-2023-27997, could be a zero-day flaw that has been exploited in limited attacks.
The vulnerability, which is a critical heap-based buffer overflow in the SSL-VPN module, can allow a remote hacker to execute arbitrary code or commands using specifically crafted requests.
Over 1 million credit cards stolen in attack across 20 countries

Knight Squad Academy now serves as Bangladesh’s first CVE Numbering Authority

Daily Cyber security update for 18.11. 2026

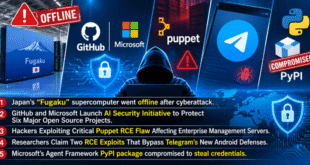
Japan’s “Fugaku” supercomputer went offline after cyberattack

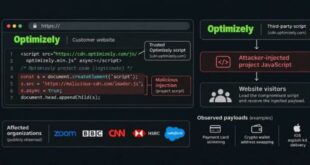
Hijacked Optimizely Scripts infect CNN, HSBC, BBC, Zoom, Salesforce sites with malware

Researcher Uncover 150 M Kik Profile Images Publicly Accessible Database

Months-old flaw led to a global Microsoft outage: said Microsoft

OWASP Top 10 Neocloud & AI Data Center Security Risks

Six 0-Days Discovered by Researchers Allow Unauthorized Access to Supermarket Fridge Systems

Daily Cyber security update for 14.11. 2026

ALSO READ:
Microsoft Warns of AitM Phishing Attacks Against Financial Organizations
Fortinet confirmed that the vulnerability was reported to the company by researchers Charles Fol and Dany Bach from French cybersecurity firm Lexfo. The company also confirmed that the vulnerability has been patched in the latest FortiOS and FortiProxy updates.
However, Fortinet said that it is possible that the vulnerability has already been exploited by attackers in limited cases. The company is working with customers to monitor the situation and is urging customers to upgrade to the latest firmware as soon as possible.
The vulnerability is not believed to be related to the Volt Typhoon campaign, which was detailed by Microsoft in May. The Volt Typhoon campaign is a Chinese state-sponsored operation that has been targeting critical infrastructure organizations in the US territory of Guam. Microsoft said that the hackers exploited internet-exposed Fortinet FortiGuard firewalls for initial access. Fortinet believes that the Volt Typhoon campaign has exploited CVE-2022-40684, a security hole that has been widely exploited for initial access since at least the fall of 2022.
Fortinet customers are advised to upgrade to the latest firmware as soon as possible to protect themselves from this vulnerability. The latest firmware can be found on Fortinet’s website.
In addition to upgrading their firmware, Fortinet customers should also implement other security measures to protect themselves from attack, such as using strong passwords, enabling multi-factor authentication, and keeping their software up to date.