Thursday , October 29 2026
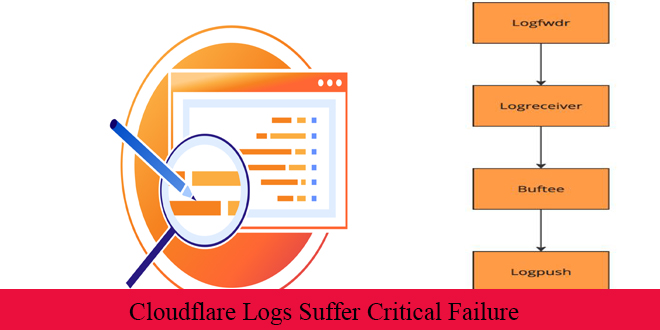
flowchart

Cloudflare logs faces major failure, losing 55% of user data

Cloudflare suffered an incident roughly 3.5 hours On November 14, 2024 impacting the majority of customers using Cloudflare Logs. Cloudflare lost about 55% of the logs normally send to customers were not sent and were lost on that incident.

Log services are crucial for network operations, helping businesses analyze traffic, troubleshoot issues, and detect threats. Cloudflare’s log service uses a tool called Logpush to process and deliver large amounts of data to customers.

Daily Cyber security update for 29.10. 2026

Cyberattacks are rising around the world, including ransomware, malware, data leaks, and hacked websites. These events show how complex and...
Read More

Rapid7 Unveils 17 Zimbra Collaboration Suite Flaws Breaking Identity Boundaries

Rapid7 researchers found 17 security flaws in Zimbra Collaboration Suite (ZCS) that mess up authentication, mailbox isolation, and host privileges....
Read More
Rapid7 Unveils 17 Zimbra Collaboration Suite Flaws Breaking Identity Boundaries

CISA launched two free tools Identify Security Misconfig in Microsoft 365 and Google Workspace

The U.S. Cybersecurity and Infrastructure Security Agency (CISA) provides two free tools to help organizations spot security flaws in Microsoft...
Read More
CISA launched two free tools Identify Security Misconfig in Microsoft 365 and Google Workspace

Apple iOS 27.2 Released Fixes 163 Flaws, Including Critical WebKit RCE

Apple launched iOS 27.2 and iPadOS 27.2 on October 26, 2026, fixing 163 security flaws. The update is for iPhone...
Read More
Apple iOS 27.2 Released Fixes 163 Flaws, Including Critical WebKit RCE

CISA adds PHP2Shell to KEV, PHP Releases New Security Updates to Fix Critical HTTP2Shell flaw

CISA has updated a new alert to reflect the addition of CVE-2026-109618 and CVE-2026-109619 to its Known Exploited Vulnerabilities (KEV)...
Read More
CISA adds PHP2Shell to KEV, PHP Releases New Security Updates to Fix Critical HTTP2Shell flaw

Cloudflare Unveils Emergency WAF Ruleset Update on Brotli flaw

Cloudflare has shared an urgent update to its Web Application Firewall (WAF) rules due to CVE-2026-111497, a Brotli issue. The release...
Read More
Cloudflare Unveils Emergency WAF Ruleset Update on Brotli flaw

Daily Cyber security update for 26.10. 2026

Cyberattacks are rising around the world, including ransomware, malware, data leaks, and hacked websites. These events show how complex and...
Read More
Daily Cyber security update for 26.10. 2026

The Washington Post report
Ex-DOGE AI startup Cathedral Breaches Anthropic Internal Systems within 12 Hours

AI startup Cathedral gained a limited access to internal systems at Anthropic in less than 12 hours, exposing employee information,...
Read More
The Washington Post report  Ex-DOGE AI startup Cathedral Breaches Anthropic Internal Systems within 12 Hours

Daily Cyber security update for 25. 10. 2026

Cyberattacks are rising around the world, including ransomware, malware, data leaks, and hacked websites. These events show how complex and...
Read More
Daily Cyber security update for 25. 10. 2026

Daily Cyber security update for 24. 10. 2026

Cyberattacks are rising around the world, including ransomware, malware, data leaks, and hacked websites. These events show how complex and...
Read More
Daily Cyber security update for 24. 10. 2026

On November 14th, a Logpush update caused a significant error. Cloudflare’s incident report revealed that the update did not direct auxiliary tools to send the collected logs. Consequently, the logs were collected but never delivered and were eventually lost when the cache was cleared.

“A misconfiguration in one part of the system caused a cascading overload in another part of the system, which was itself misconfigured. Had it been properly configured, it could have prevented the loss of logs,” Cloudflare stated in their report.

Engineers team quickly found the flaw and reverted the update, but this caused a cascading failure. The system became overwhelmed with excessive log data, including from users who hadn’t set up Logpush, worsening the problem.

Cloudflare has apologized for the loss of user data and is implementing measures to prevent future incidents, though efforts are still underway.

The loss of important log data highlights the need for thorough testing and backup measures to maintain the integrity and availability of crucial information.

Check Also

Trump

Trump says data centres should pay dividends to local community

US President Donald Trump said on Wednesday that companies ​building data centers should pay a …