Saturday , November 7 2026
Clop ransomware

Clop ransomware claim to breach Oracle via E-Business Suite 0-Day hack

The Clop ransomware gang claims to have breached Oracle’s internal systems and has listed the company on its dark web leak site.

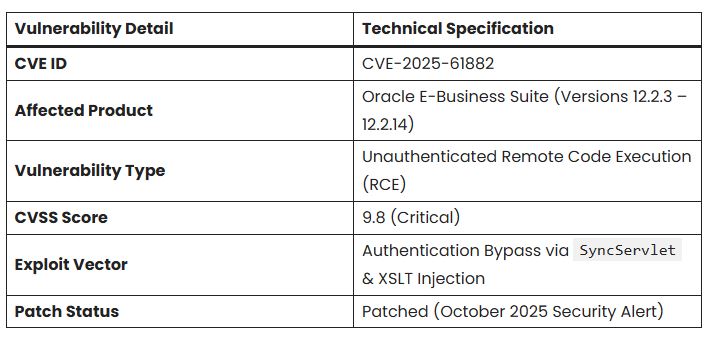
This is part of a large extortion campaign that takes advantage of a serious zero-day vulnerability in Oracle E-Business Suite (EBS), dubbed CVE-2025-61882.

Japan banking crisis
Outage causes disruption at 128 japan banks: preventing ATM transaction

A major system failure has brought customer-facing banking services to a standstill at 128 shinkin banks across western Japan, leaving...
Read More
Japan banking crisis  Outage causes disruption at 128 japan banks: preventing ATM transaction

Daily Cyber security update for 06.11. 2026

Cyberattacks are rising around the world, including ransomware, malware, data leaks, and hacked websites. These events show how complex and...
Read More
Daily Cyber security update for 06.11. 2026

Cyber attack causes French bank Credit Mutuel Arkea €100 million missing

French lender Credit Mutuel Arkea said on Thursday hackers had stolen around €100 million ($112.61 million) in a cyber heist...
Read More
Cyber attack causes French bank Credit Mutuel Arkea €100 million missing

OpenAI AI Pipeline Discovers 948 Linux Kernel Privilege Escalation Flaws in 30 Hours

OpenAI says that an automated system found and confirmed 948 different Linux kernel security issues in one run. These flaws...
Read More
OpenAI AI Pipeline Discovers 948 Linux Kernel Privilege Escalation Flaws in 30 Hours

Bangladeshi Researcher Rasel Earns First Apple CVE Recognition for Model I/O Flaw

Apple credits Md Rasel Bhuyan and fellow researcher Musaab Khan for discovering an out-of-bounds write vulnerability affecting multiple Apple operating...
Read More
Bangladeshi Researcher Rasel Earns First Apple CVE Recognition for Model I/O Flaw

WinRAR, WordPress RCE flaw & Zyxel GS1900 Zero-Day exploited in the wild

A flaw in Zyxel GS1900 switches was being used by hackers, and the update to fix it did not work....
Read More
WinRAR, WordPress RCE flaw & Zyxel GS1900 Zero-Day exploited in the wild

Daily Cyber security update for 04.11. 2026

Cyberattacks are rising around the world, including ransomware, malware, data leaks, and hacked websites. These events show how complex and...
Read More
Daily Cyber security update for 04.11. 2026

Daily Cyber security update for 03.11. 2026

Cyberattacks are rising around the world, including ransomware, malware, data leaks, and hacked websites. These events show how complex and...
Read More
Daily Cyber security update for 03.11. 2026

Using ARTEX AI, Hacker to attack 200 Organizations Across 14 Countries

Hackers used ARTEX, a free tool for testing security with AI, to attack over 200 organizations in 14 countries. The...
Read More
Using ARTEX AI, Hacker to attack 200 Organizations Across 14 Countries

Amadeus cyber incident impacted “Cathay Pacific, Qantas, Japan, Malaysia, Korean & Asiana” Airlines

A cybersecurity incident with Spanish travel tech company Amadeus IT Group has worried the global airline industry. Hackers got into...
Read More
Amadeus cyber incident impacted “Cathay Pacific, Qantas, Japan, Malaysia, Korean & Asiana” Airlines

Security experts report that Clop affiliates started using this vulnerability as early as August 2025, before Oracle issued a fix in October 2025.

The exploit chain specifically targets the OA_HTML/SyncServlet endpoint to bypass authentication, followed by malicious XSLT template injection via OA_HTML/RF.jsp to execute arbitrary commands.

This “pre-auth” nature allowed attackers to compromise servers without valid credentials, granting them full control over sensitive ERP data.​

cybersecuritynews reported, evidence from Clop’s leak site shows a “PAGE CREATED” status for ORACLE.COM, listed with major companies like MAZDA.COM, HUMANA.COM, and the Washington Post.

The Oracle Corporation listing hints that the company may have suffered from its own software issue.
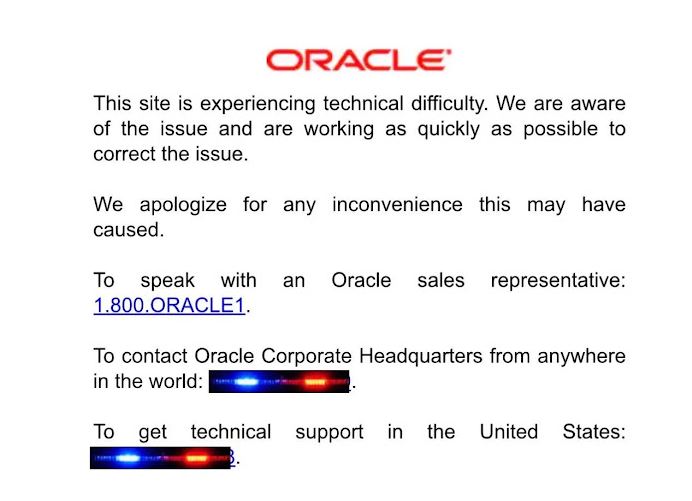
Source: Cybersecuritynews.com

Victims report receiving extortion emails from addresses like support@pubstorm[.]com, threatening the release of financial and personal records if ransom demands are not met.​

Check Also

Zyxel GS1900

WinRAR, WordPress RCE flaw & Zyxel GS1900 Zero-Day exploited in the wild

A flaw in Zyxel GS1900 switches was being used by hackers, and the update to …