 InfoSecBulletin Cybersecurity for mankind
A renowned security analyst and bug hunter, Nagli (@naglinagli), recently uncovered a critical security vulnerability in ChatGPT.
With just a single click, a threat actor could easily exploit the vulnerability and gain complete control of any ChatGPT user’s account.
Nearly 100,000 email addresses exposed in first AI-related data breach in Singapore

Hackers Exploit Zimbra Mail Servers: TeamViewer patched 5 critical flaws

Google Warns of Hackers Actively Exploiting Citrix 0-Day Flaws

CISA Warns Critical MikroTik RouterOS Flaw While Cisco SD-WAN Zero-Day Exploited in Attacks

Apple Zero-Day Exploited: Pentagon Data Breach Reportedly Exposes Sensitive Data of 3 Million People

JadePuffer Agentic AI targets and destroys Azure’s cloud resources

“InfoSecCon-2026: Bangladesh’s Cybersecurity Leaders Unite to Shape a Safer Digital Future”

Microsoft Patches CVSS 10.0 Azure AI Foundry Vulnerability Allowing Privilege Escalation

AWS is unable to restore access to Bahrain, one UAE cloud data zone after war damage

Cisco Warns of Critical ISE 0-Day Flaw and Hackers Allegedly Selling Fortinet FortiGate 1-Day Flaw

As a result, opening the doors to sensitive data let attackers execute unauthorized actions; the whole is termed “Account Take Over.”
ChatGPT Account Takeover
Account takeover is a sneaky cyber attack where an attacker or hacker gains access to your account unauthorizedly by either exploiting in the system or stealing your login details.
It is possible for an attacker to conduct a variety of malicious activities after having gained access to a target system or device:-
- Theft of personal information
- Fraudulent transactions
- Spread malware
To access a victim’s ChatGPT account, the attacker exploits a web cache deception vulnerability. This ChatGPT Account Take Over bug made a single-click attack possible, enabling a remote attacker to compromise any user’s account and completely take over the account.
ChatGPT Account Take Over Bug Attack Flow
A web cache deception vulnerability is a sneaky security flaw that lets attackers trick web servers’ caching systems, giving them access to users’ accounts.
A vulnerability like this can arise when a website’s server cache is set up or used incorrectly. Hackers can use this ChatGPT Account Take Over vulnerability to manipulate cached web pages or create fake ones to deceive users.
Here below, we have mentioned the complete attack flow in five key points, and these key points will give you an accessible overview of the complete attack flow:-
- Attacker crafts a dedicated .css path of the /api/auth/session endpoint.
- Attacker distributes the link (either directly to a victim or publicly)
- Victims visit the legitimate link.
- Response is cached.
- Attacker harvests JWT Credentials.
If left unchecked, this web cache deception vulnerability could’ve given attackers access to sensitive user information, including:-
- Names
- Email addresses
- Access tokens

While all of these above-mentioned data are retrieved from the OpenAI’s API server, which is accessed via the following URL:-
https[:]//chat[.]openai[.]com/api/auth/session
Then this information could be used to generate a request to “https://chat.openai.com/api/auth/session/victim.css.” No matter if the victim “.css” file was on the server, the server would respond with the same data as “/api/auth/session.”
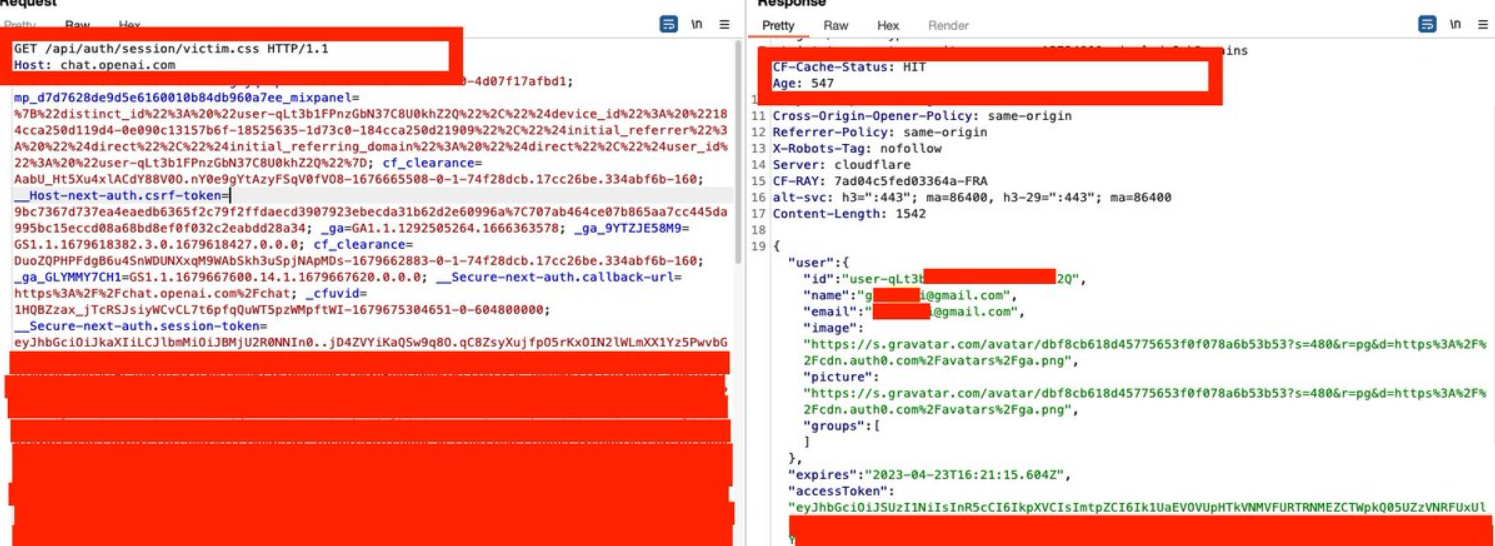
The server would cache a CSS file and save the victim’s session content, data, and access token in the process due to the “.css” extension.
For the exploit to succeed, the CF-Cache-Status response must confirm a cached “HIT.” This means the data was cached and will be served to the following request within the same region.
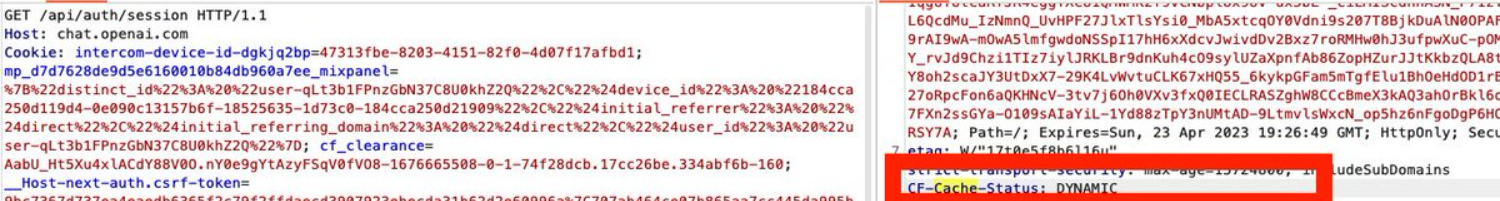
An attacker can read a victim’s sensitive data from the cached response if they manipulate the Load Balancer into caching their request on a customized path.
See the flaw in action:-
When Nagli discovered the issue, he acted quickly and responsibly by reporting it to the ChatGPT team. By doing so, he helped to prevent potential harm and ensure the continued safety of ChatGPT users.
Even though the researcher did not receive any financial compensation for his efforts, he asserted that he is proud to have played a role in enhancing the security of the innovative product.
Mitigation
Web cache deception is a highly severe vulnerability that’s relatively easy to exploit. However, there are several ways to mitigate this issue, and here below we have mentioned them:-
- The cache server should operate based on the application’s cache-control headers.
- Only cache files if HTTP caching headers allow it.
- Cache files based on their Content-Type header, not just the file extension.
- Return HTTP errors like 404 or 302 for non-existent files.



