Monday , May 4 2026
Alert, Vulnerabilities
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) added a new security flaw affecting different Linux versions to its list of Known Exploited Vulnerabilities (KEV). They mentioned that there is proof of this flaw being used in real attacks. The flaw, known as CVE-2026-31431 (CVSS score: 7.8), is a type …
Read More »
Monday , May 4 2026
Alert
Microsoft Defender sent out many false alerts after a wrong security update made it mark two real DigiCert root certificates as malicious. This could have stopped SSL/TLS checks and code-signing work in businesses everywhere. A Defender antimalware signature update released around April 30, 2026, introduced a detection labeled Trojan:Win32/Cerdigent.A!dha, which …
Read More »
Sunday , May 3 2026
Alert, National, Social media
A new app dubbed ‘NB” TV is fast spreading in Bangladeshi but creating panic as well. By using the app some people have automatically lost money in different locations in Bangladesh. While installing, the app takes control over the smartphone and transfers money as its maker instructs. The Cyber Unit of …
Read More »
Sunday , May 3 2026
Alert, National
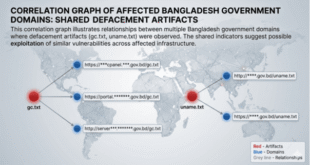
Cyber Threat Intelligence Unit of BGD e-Gov CIRT has found many suspicious files on Bangladesh government infra like gc.txt and uname.txt. Hackers use such files to check unauthorized write access to web servers. The found artifacts match signs of a big global web defacement campaign that hit Magento systems, first …
Read More »
Saturday , May 2 2026
Alert, Vulnerabilities
A weaponized proof-of-concept (PoC) exploit framework dubbed “cPanelSniper” has been publicly released for CVE-2026-41940, a maximum-severity authentication bypass in cPanel & WHM that has already led to the compromise of tens of thousands of servers worldwide with attack activity traced as far back as late February 2026. CVE-2026-41940 is a …
Read More »
Friday , May 1 2026
Alert
Wazuh has fixed a critical issue dubbed CVE-2026-30893 which is rated 9.0 on the CVSS scale allowing an authenticated cluster peer to write arbitrary files outside the intended extraction directory on other cluster nodes. This can be escalated to code execution in the Wazuh service context by overwriting Python modules …
Read More »
Wednesday , April 29 2026
Alert
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) warn federal agencies to protect their Windows systems from a flaw used in zero-day attacks. CVE-2026-32202 is a security issue found by the cybersecurity company Akamai. They say it is a zero-click NTLM hash leak problem that remains after Microsoft did not …
Read More »
Wednesday , April 29 2026
Alert
Google has launched an important security update for the Chrome browser. It fixes 30 security issues. This update makes the browser version 147.0.7727.137/138 for Windows and Mac, and 147.0.7727.137 for Linux. It will be available to users worldwide in the next few days and weeks. This patch cycle is particularly …
Read More »
Saturday , April 18 2026
Alert, International
Hackers are looking for weak TP-Link home routers to spread Mirai-like malware, taking advantage of CVE-2023-33538 in a new round of automated attacks. Current exploit attempts have some technical problems, but researchers say the bug is real and can be dangerous when used with default passwords and outdated firmware. Network …
Read More »
Saturday , April 18 2026
Alert, Hot Topic
A recent April 2026 report from security expert Himaja Motheram at Censys says that nearly 6 million internet-connected hosts still use the File Transfer Protocol (FTP). This shows a big 40% drop from the 10.1 million servers seen in 2024. This old protocol still brings a risk because many users keep …
Read More »
 InfoSecBulletin Cybersecurity for mankind