InfoSecBulletin Cybersecurity for mankind
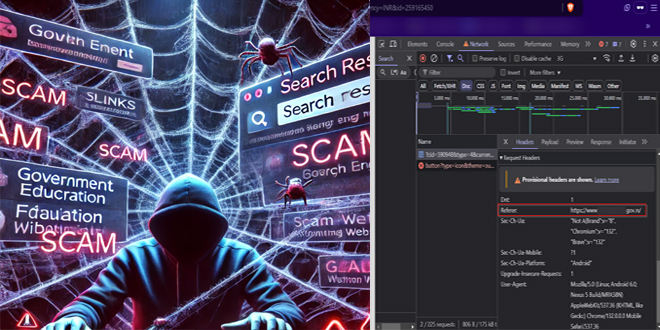
Indian government and educational websites, along with reputable financial brands, have experienced SEO poisoning, causing user traffic to be redirected to dubious sites promoting rummy and other investment games.
Analysts at CloudSEK have found that threat actors are using black hat Search Engine Poisoning to promote Rummy and investment websites to unsuspecting users. They are targeting sites with .gov.in and .ac.in domains, employing keyword stuffing related to well-known Indian financial brands. Over 150 government portals, mainly from state governments, have been impacted.
Daily Cyber security update for 14.11. 2026

Huge European telecom leak exposes clients of Swedbank, SEB, airBaltic, and other companies

PHP2Shell attack exploited a Check Point 0-day to deploy malware

North Korean hackers steal more than $400 million using video images, FBI says

Microsoft’s November 2026 Patch Tuesday addresses 1,093 flaws, with Outlook zero-day

Barracuda ESG flaws exploited, gaining root access

Apple, SAP, and Ivanti Patch Critical flaws Affecting Messaging, Bluetooth, and Enterprise Systems

Jailbroken DeepSeek AI Agent Conducts Two-Week Cyberattack on European Telecom

Daily Cyber security update for 10.11. 2026

IBM fixes 208 API Connect vulnerabilities, 47 critical

What is Search Engine Poisoning?
Search engine poisoning refers to malicious practices aimed at manipulating search engine results to promote harmful or deceptive content. These tactics are typically employed by cybercriminals to redirect users to fraudulent websites, distribute malware, or launch phishing attacks. Techniques in play are Referrer Header Manipulation, Cloaking, Keyword Stuffing, Backlinking, Underlying system Vulnerabilities.
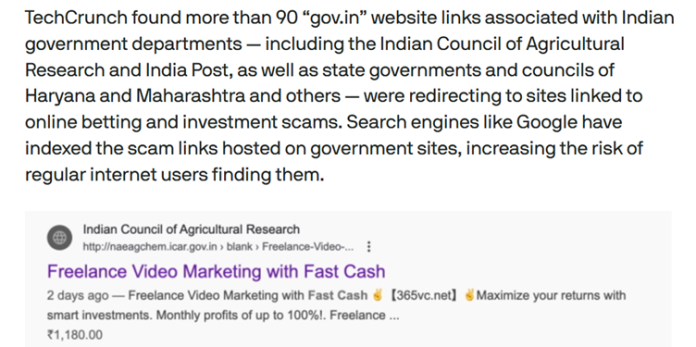
Threat actors injected malicious JavaScript into vulnerable government websites, including state portals, to manipulate search engine rankings. The script redirects mobile users from search engines like Google to gambling sites, while showing error pages to desktop users to avoid detection.
One compromised Kerala government webpage, for instance, was altered to include hidden keywords like “instant personal loans” and “low-interest credit cards” tied to major Indian banks.
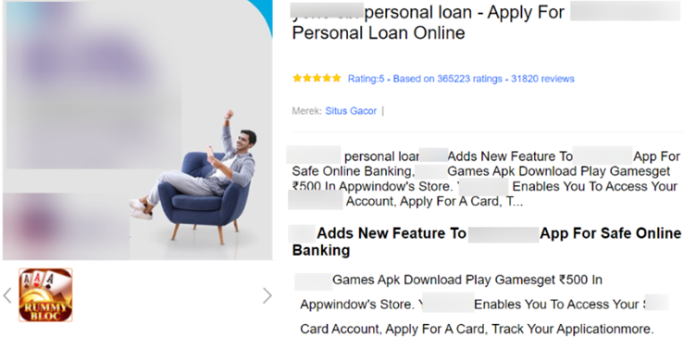
Analysts found over 12,000 spam pages leveraging .shtml and .aspx file uploads on government servers, with content mirroring Indonesian casino templates to bypass regional filters.
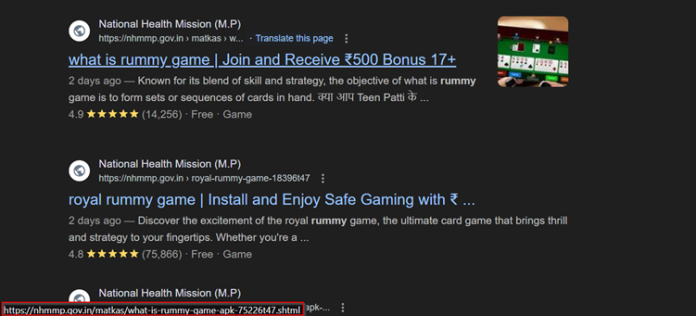
Users searching for legitimate financial services are funneled to pages promoting rummy games disguised as “investment opportunities”.
Since January 2025, Google has removed 2,300 malicious pages, but ephemeral domains and encrypted traffic remain challenges. With annual losses over ₹200 crore, this issue underscores the urgent need for better defenses in India’s digital governance.
Builder claims Rs 150 cr for data loss; AWS faces FIR In Bengaluru