 InfoSecBulletin Cybersecurity for mankind
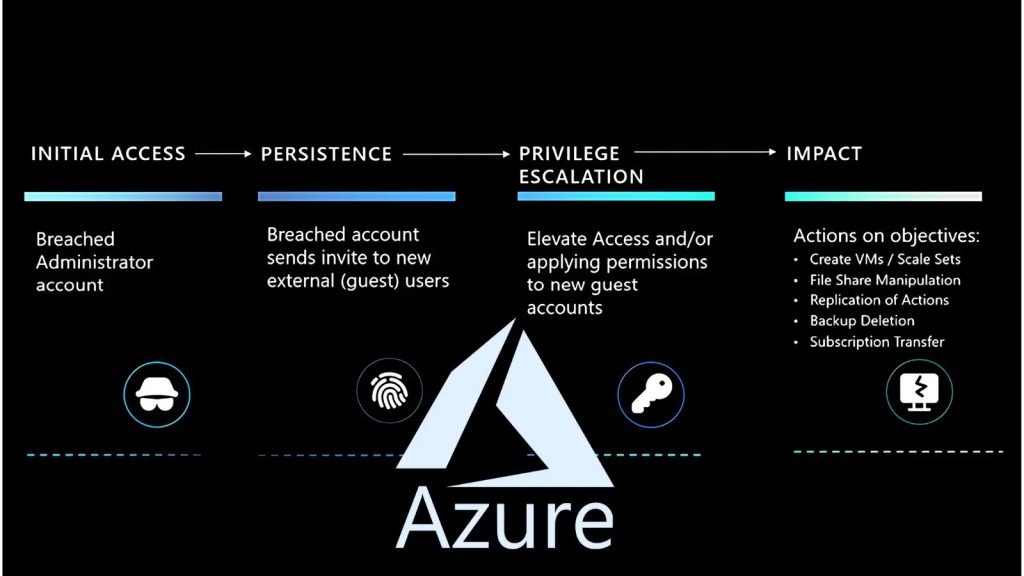
Microsoft security experts recently conducted an exploration on how to effectively use Azure Logs to identify and counteract threat actions. Azure’s defense mechanism relies on effectively understanding and using logs to hunt for threats.
Microsoft focuses on integrating best practices for log management, analysis, and incident response to stay proactive against evolving cyber threats.
Daily Cyber security update for 14.11. 2026

Huge European telecom leak exposes clients of Swedbank, SEB, airBaltic, and other companies

PHP2Shell attack exploited a Check Point 0-day to deploy malware

North Korean hackers steal more than $400 million using video images, FBI says

Microsoft’s November 2026 Patch Tuesday addresses 1,093 flaws, with Outlook zero-day

Barracuda ESG flaws exploited, gaining root access

Apple, SAP, and Ivanti Patch Critical flaws Affecting Messaging, Bluetooth, and Enterprise Systems

Jailbroken DeepSeek AI Agent Conducts Two-Week Cyberattack on European Telecom

Daily Cyber security update for 10.11. 2026

IBM fixes 208 API Connect vulnerabilities, 47 critical

Identifying the initial breach and understanding subsequent actions is crucial in this process. Microsoft emphasizes the importance of integrating best practices for managing logs, analyzing them, and responding to incidents to stay ahead of cyber threats.
Microsoft describes a hypothetical attack scenario called “Pass the Cookie” where an attacker steals a user’s session cookie to gain unauthorized access to their account. It is important to closely monitor and analyze Azure logs to detect sophisticated attacks.
Log Analysis Techniques:
“To simplify cybersecurity challenges, Microsoft recommends utilizing Azure Log Analytics.” This tool is essential for investigating security incidents within Azure subscriptions.”
By sending both Microsoft Entra ID Audit logs and Azure Activity logs to Log Analytics, organizations can consolidate these logs in the CloudAppEvents table.

Simultaneously, Log Analytics organizes this data into the AuditLogs and AzureActivity tables.
Microsoft provides examples of Log Analytics queries, such as hunting for Azure Role assignments to newly added guest user accounts, demonstrating the practical application of log analysis in identifying potential security threats and vulnerabilities.
Understanding the scope and complexity of threat actor actions is crucial in fortifying defenses against cyberattacks. The detailed analysis of logs enables organizations to trace attackers’ steps, from the initial breach to their movements within the Azure environment. This insight is invaluable in developing strategies to prevent future attacks and enhance the security posture of cloud subscriptions.



