 InfoSecBulletin Cybersecurity for mankind
DataDog Security Labs found a worrying campaign targeting Amazon Web Services (AWS), showing a new wave of harmful activity aimed at compromising important cloud resources. The attackers are using various methods, focusing on finding and possibly stealing data from AWS Secrets Manager, S3 buckets, and S3 Glacier vaults.
Between May 23rd and 27th, 2024, a campaign showed how cyber threats to cloud infrastructure continue to evolve. The attackers likely to use leaked access keys, residential proxies, and the Cloudflare WARP VPN to hide their actions, showing their sophistication and determination.
PHP shares new RCE flaw (CVE 2026-115560) with no patch but mitigation

US banks faced unauthorized access by AI agents in customer accounts: Axios reports

Atlassian patched 176 flaw in Jira and Confluence: Fortinet Urges to Patch Flaws Affecting FortiOS, FortiManager

Hacker claim to access Rajasthan Police data: 70,000 records allegedly exposed

Update now! PHP2Shell: Critical PHP vulnerabilities patched

Trump says data centres should pay dividends to local community

Hackers Actively Exploiting Palo Alto VPN Flaw Via CVE-2026-0257

DeepSeek AI banned by U.S. Government; federal agencies must remove all related tools

CISA, NSA and NIST Publish New 10 AI Agent Control Guidelines

Claude AI Cracks 25-Year NSA Cryptography Number Mystery in Just 30 Minutes

DataDog’s research did not find any successful attempts to steal data. However, the fact that many AWS resources were being identified suggests that there might be a deliberate and potentially large-scale operation happening.
While DataDog’s research did not observe successful data exfiltration attempts, the widespread enumeration of AWS resources suggests a calculated and potentially large-scale operation. The attackers may be assessing the value of available data before initiating exfiltration or testing the level of access they possess for potential resale in underground markets.
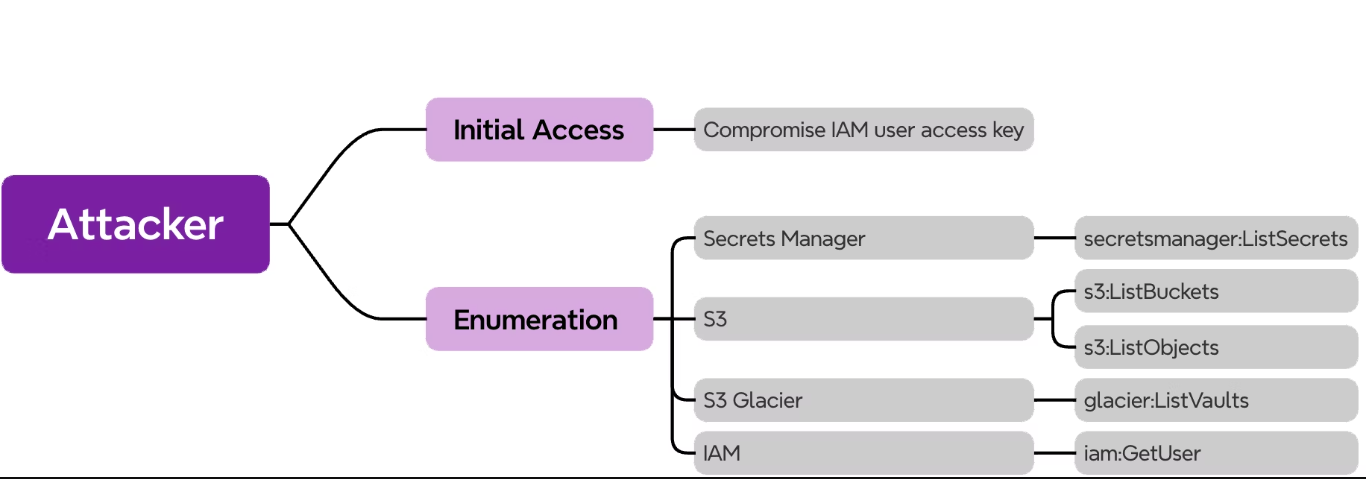
Attackers are now targeting S3 Glacier vaults, a shift from the traditional focus on S3 buckets. This shows that attackers are broadening their tactics to explore new ways to exploit potential vulnerabilities.
DataDog’s report provides important information about the tactics, techniques, and procedures used in this campaign. It gives organizations valuable insights to improve their AWS security. By monitoring the indicators of compromise and implementing proactive security measures, organizations can reduce the risk of being attacked.



