Monday , October 26 2026

Alert: HPE (CVE-2025-37164) warns RCE flaw and ASUS (CVE-2025-59374) Flaw added in KEV

Hewlett Packard Enterprise (HPE) has fixed a critical vulnerability in its OneView software that allowed remote code execution. OneView is HPE’s software for managing infrastructure, helping IT admins streamline server, storage, and network management.

Vietnamese researcher Nguyen Quoc Khanh (brocked200) reported the critical security flaw (CVE-2025-37164) to the company’s security team.

Daily Cyber security update for 25. 10. 2026

Cyberattacks are rising around the world, including ransomware, malware, data leaks, and hacked websites. These events show how complex and...
Read More
Daily Cyber security update for 25. 10. 2026

Daily Cyber security update for 24. 10. 2026

Cyberattacks are rising around the world, including ransomware, malware, data leaks, and hacked websites. These events show how complex and...
Read More
Daily Cyber security update for 24. 10. 2026

PHP shares new RCE flaw (CVE 2026-115560) with no patch but mitigation

The PHP security team shared ways to protect against a new flaw that lets someone run unwanted code on certain...
Read More
PHP shares new RCE flaw (CVE 2026-115560) with no patch but mitigation

US banks faced unauthorized access by AI agents in customer accounts: Axios reports

Major US banks have detected unauthorized access to customer accounts by third-party AI agents, with some systems taking actions beyond...
Read More
US banks faced unauthorized access by AI agents in customer accounts: Axios reports

Atlassian patched 176 flaw in Jira and Confluence: Fortinet Urges to Patch Flaws Affecting FortiOS, FortiManager

Fortinet has urged customers to prioritize security updates for FortiOS, FortiManager, and FortiAnalyzer scheduled for October 22, 2026. The coordinated...
Read More
Atlassian patched 176 flaw in Jira and Confluence: Fortinet Urges to Patch Flaws Affecting FortiOS, FortiManager

Hacker claim to access Rajasthan Police data: 70,000 records allegedly exposed

Hacker offers to sell Rajasthan Government’s Department of Information Technology & Communication (DoIT&C) data in a underground forum. The threat...
Read More
Hacker claim to access Rajasthan Police data: 70,000 records allegedly exposed

Update now! PHP2Shell: Critical PHP vulnerabilities patched

The PHP team released urgent security updates to fix PHP2Shell, two serious flaws (CVE-2026-109618 and CVE-2026-109619) that let attackers run...
Read More
Update now! PHP2Shell: Critical PHP vulnerabilities patched

Trump says data centres should pay dividends to local community

US President Donald Trump said on Wednesday that companies ​building data centers should pay a "dividend" to the communities ‌where...
Read More
Trump says data centres should pay dividends to local community

Hackers Actively Exploiting Palo Alto VPN Flaw Via CVE-2026-0257

Ransomware groups are using a flaw in Palo Alto Networks GlobalProtect VPN to get around multi-factor authentication and access corporate...
Read More
Hackers Actively Exploiting Palo Alto VPN Flaw Via CVE-2026-0257

DeepSeek AI banned by U.S. Government; federal agencies must remove all related tools

The U.S. Department of Homeland Security (DHS) ordered federal agencies to stop using DeepSeek products and remove it from all...
Read More
DeepSeek AI banned by U.S. Government; federal agencies must remove all related tools

All OneView versions prior to v11.00 are vulnerable to exploitation by unauthenticated attackers through simple code injection, allowing remote code execution on unpatched systems.

“A potential security vulnerability has been identified in Hewlett Packard Enterprise OneView Software. This vulnerability could be exploited, allowing a remote unauthenticated user to perform remote code execution,” HPE warned in a Tuesday advisory.

Admins should patch vulnerable systems for CVE-2025-37164 immediately, as no workarounds or mitigations are available. HPE has not confirmed if this vulnerability has been exploited in attacks. Affected organizations can upgrade to OneView version 11.00 or later via HPE’s Software Center to fix it.

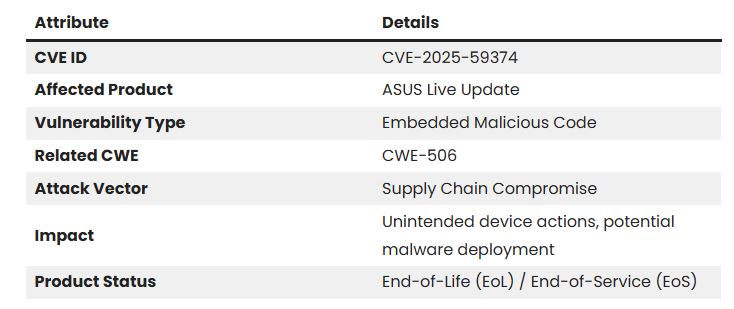
CISA has included a new ASUS vulnerability in its Known Exploited Vulnerabilities catalog, indicating a serious risk for affected users. The flaw, CVE-2025-59374, impacts ASUS Live Update, a tool for firmware and software updates on ASUS devices. The advisory states that some ASUS Live Update clients were compromised with malware due to unauthorized changes in the supply chain.

 

Check Also

VPN

Hackers Actively Exploiting Palo Alto VPN Flaw Via CVE-2026-0257

Ransomware groups are using a flaw in Palo Alto Networks GlobalProtect VPN to get around …