Tuesday , October 27 2026
ColdFusion

CVE-2024-53961
Adobe alerts of critical ColdFusion bug with PoC exploit available

Adobe has issued urgent security updates for ColdFusion versions 2023 and 2021 to fix a critical vulnerability (CVE-2024-53961). This flaw allows attackers to read arbitrary files from the system, risking exposure of sensitive data and configuration files. It results from improper path limitations, enabling unauthorized access outside the intended directory.

Proof-of-Concept Exploit Exists:

Cloudflare Unveils Emergency WAF Ruleset Update on Brotli flaw

Cloudflare has shared an urgent update to its Web Application Firewall (WAF) rules due to CVE-2026-111497, a Brotli issue. The release...
Read More
Cloudflare Unveils Emergency WAF Ruleset Update on Brotli flaw

Daily Cyber security update for 26.10. 2026

Cyberattacks are rising around the world, including ransomware, malware, data leaks, and hacked websites. These events show how complex and...
Read More
Daily Cyber security update for 26.10. 2026

The Washington Post report
Ex-DOGE AI startup Cathedral Breaches Anthropic Internal Systems within 12 Hours

AI startup Cathedral gained a limited access to internal systems at Anthropic in less than 12 hours, exposing employee information,...
Read More
The Washington Post report  Ex-DOGE AI startup Cathedral Breaches Anthropic Internal Systems within 12 Hours

Daily Cyber security update for 25. 10. 2026

Cyberattacks are rising around the world, including ransomware, malware, data leaks, and hacked websites. These events show how complex and...
Read More
Daily Cyber security update for 25. 10. 2026

Daily Cyber security update for 24. 10. 2026

Cyberattacks are rising around the world, including ransomware, malware, data leaks, and hacked websites. These events show how complex and...
Read More
Daily Cyber security update for 24. 10. 2026

PHP shares new RCE flaw (CVE 2026-115560) with no patch but mitigation

The PHP security team shared ways to protect against a new flaw that lets someone run unwanted code on certain...
Read More
PHP shares new RCE flaw (CVE 2026-115560) with no patch but mitigation

US banks faced unauthorized access by AI agents in customer accounts: Axios reports

Major US banks have detected unauthorized access to customer accounts by third-party AI agents, with some systems taking actions beyond...
Read More
US banks faced unauthorized access by AI agents in customer accounts: Axios reports

Atlassian patched 176 flaw in Jira and Confluence: Fortinet Urges to Patch Flaws Affecting FortiOS, FortiManager

Fortinet has urged customers to prioritize security updates for FortiOS, FortiManager, and FortiAnalyzer scheduled for October 22, 2026. The coordinated...
Read More
Atlassian patched 176 flaw in Jira and Confluence: Fortinet Urges to Patch Flaws Affecting FortiOS, FortiManager

Hacker claim to access Rajasthan Police data: 70,000 records allegedly exposed

Hacker offers to sell Rajasthan Government’s Department of Information Technology & Communication (DoIT&C) data in a underground forum. The threat...
Read More
Hacker claim to access Rajasthan Police data: 70,000 records allegedly exposed

Update now! PHP2Shell: Critical PHP vulnerabilities patched

The PHP team released urgent security updates to fix PHP2Shell, two serious flaws (CVE-2026-109618 and CVE-2026-109619) that let attackers run...
Read More
Update now! PHP2Shell: Critical PHP vulnerabilities patched

Adobe has confirmed a proof-of-concept exploit for CVE-2024-53961, indicating that attackers can exploit this vulnerability. Users should update their ColdFusion installations immediately.

“Adobe is aware that CVE-2024-53961 has a known proof-of-concept that could cause an arbitrary file system read,” Adobe said today, while also cautioning customers that it assigned a “Priority 1” severity rating to the flaw because it has a “a higher risk of being targeted, by exploit(s) in the wild for a given product version and platform.”

CISA warned in May that software companies should fix path traversal security bugs before releasing products, as attackers can exploit these vulnerabilities to access sensitive data, including credentials used to breach accounts and systems.
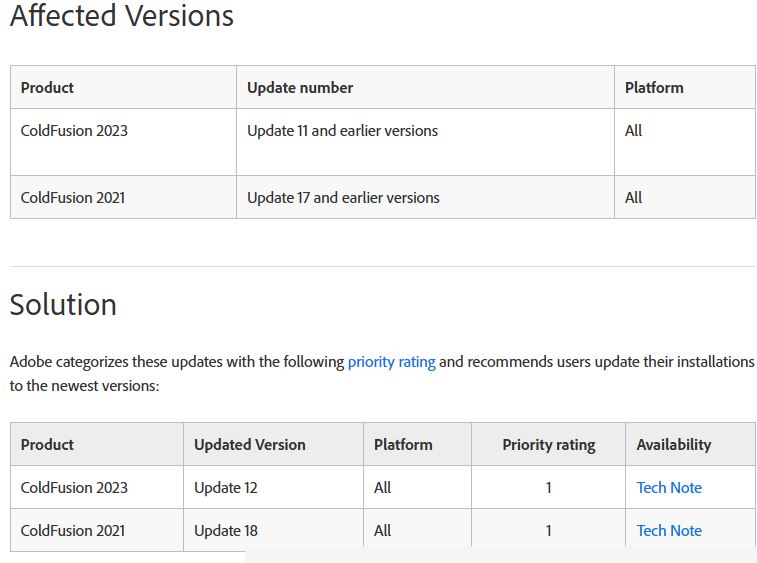
     Source: Adobe

In July 2023, CISA directed federal agencies to secure their Adobe ColdFusion servers by August 10th due to two critical vulnerabilities (CVE-2023-29298 and CVE-2023-38205), one of which was a zero-day exploit.

The U.S. cybersecurity agency reported a year ago that hackers had exploited a ColdFusion vulnerability (CVE-2023-26360) to access outdated government servers since June 2023. This flaw was also used in limited zero-day attacks since March 2023.


Check Also

Update now! PHP2Shell: Critical PHP vulnerabilities patched

The PHP team released urgent security updates to fix PHP2Shell, two serious flaws (CVE-2026-109618 and …