 InfoSecBulletin Cybersecurity for mankind

Refuting the ChatGPT Data Breach
OpenAI, the parent company of ChatGPT, has refuted a report by Group-IB that alleges a data breach of the AI software. Group-IB reported that over 100,000 infected devices were housing ChatGPT hacked credentials. However, OpenAI claims that the credential leak was due to “existing commodity malware” on users’ devices, not a breach of ChatGPT itself.
Hackers Actively Exploiting Palo Alto VPN Flaw Via CVE-2026-0257

DeepSeek AI banned by U.S. Government; federal agencies must remove all related tools

CISA, NSA and NIST Publish New 10 AI Agent Control Guidelines

Claude AI Cracks 25-Year NSA Cryptography Number Mystery in Just 30 Minutes

Bypassing firewalls, AI Agents Accessed Indian ‘ Data Without Permission: CERT-In

MITRE ATT&CK v20 Unveils 9 New Attack Techniques On AI Exploits, MFA Bypass, and CAPTCHA Evasion

Hackers Exploit Fortinet Flaws to Deploy Stealthy PEERSTITCH Malware on FortiGate Firewalls

Hacker stole Meta GitHub repos; Stole Source Code

Urgent patch! Zoom,NVIDIA and IBM Patch 41 Security flaws

Microsoft patches record braking 1411 flaws; 2 zero days

ChatGPT data breach update:
In response to the ChatGPT data breach update query, the OpenAI communications team said the ChatGPT was not hacked and they are currently investigating the alleged hacked ChatGPT accounts.
“The findings from Group-IB’s Threat Intelligence report result from commodity malware on people’s devices and not an OpenAI breach. We are currently investigating the accounts that have been exposed,” an OpenAI spokesperson told Media.
A report from Check Point Research (CPR) highlighted an increase in the trade of stolen ChatGPT Premium accounts, allowing cybercriminals to bypass geofencing restrictions and gain unlimited access.
OpenAI maintains that it has industry best practices in place to protect user data, and that it is currently investigating the accounts that have been exposed. The company also encourages users to use strong passwords and install only verified and trusted software on their personal computers.
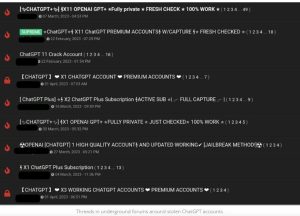
The ChatGPT data breach is the latest in a series of security concerns surrounding the AI software. In April 2023, Italy became the first country to ban ChatGPT, accusing OpenAI of stealing user data. Additionally, a report from Check Point Research highlighted an increase in the trade of stolen ChatGPT Premium accounts.
ALSO READ:
2463 Bangladeshi’s Compromised ChatGPT accounts are for sale on dark web
The market for stolen ChatGPT accounts has seen a rise, with cybercriminals utilizing tools like bruteforcing and checkers to hack into accounts. Additionally, “ChatGPT Accounts as a Service” has emerged, offering stolen premium accounts, often using stolen payment cards.
The demand for stolen ChatGPT accounts, especially premium ones, has increased due to the ability to bypass restrictions and access premium features. Cybercriminals exploit this demand in the dark web underground, where stolen accounts are sold and even shared for free to promote other malicious services.



