Sunday , October 25 2026
military

“Forces Penpals” exposed US and UK Military Social Network’s 1 Million Records

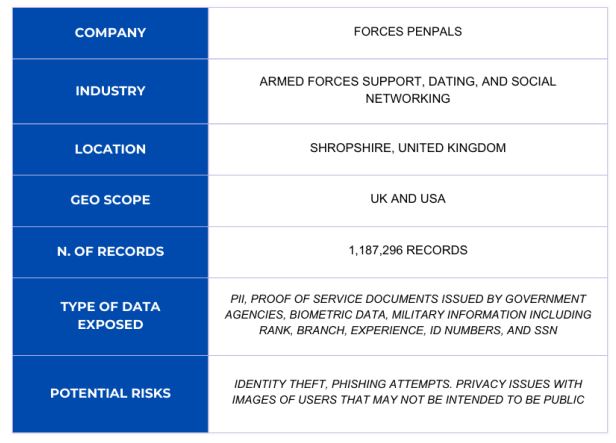
Renowned cybersecurity researcher Jeremiah Fowler uncovered a non-password-protected database having over 1.1 million records linked to Conduitor Limited (Forces Penpals). This platform provides dating services and social networking for US and UK military personnel and their supporters.
Source: VPNmentor

Jeremiah Fowler revealed that the publicly accessible database lacked password protection and encryption. It comprised a staggering total of 1,187,296 documents. In a brief review of the contents, it was noted that the majority of the documents were user images, alongside other potentially sensitive proof of service photos.

Daily Cyber security update for 24. 10. 2026

Cyberattacks are rising around the world, including ransomware, malware, data leaks, and hacked websites. These events show how complex and...
Read More
Daily Cyber security update for 24. 10. 2026

PHP shares new RCE flaw (CVE 2026-115560) with no patch but mitigation

The PHP security team shared ways to protect against a new flaw that lets someone run unwanted code on certain...
Read More
PHP shares new RCE flaw (CVE 2026-115560) with no patch but mitigation

US banks faced unauthorized access by AI agents in customer accounts: Axios reports

Major US banks have detected unauthorized access to customer accounts by third-party AI agents, with some systems taking actions beyond...
Read More
US banks faced unauthorized access by AI agents in customer accounts: Axios reports

Atlassian patched 176 flaw in Jira and Confluence: Fortinet Urges to Patch Flaws Affecting FortiOS, FortiManager

Fortinet has urged customers to prioritize security updates for FortiOS, FortiManager, and FortiAnalyzer scheduled for October 22, 2026. The coordinated...
Read More
Atlassian patched 176 flaw in Jira and Confluence: Fortinet Urges to Patch Flaws Affecting FortiOS, FortiManager

Hacker claim to access Rajasthan Police data: 70,000 records allegedly exposed

Hacker offers to sell Rajasthan Government’s Department of Information Technology & Communication (DoIT&C) data in a underground forum. The threat...
Read More
Hacker claim to access Rajasthan Police data: 70,000 records allegedly exposed

Update now! PHP2Shell: Critical PHP vulnerabilities patched

The PHP team released urgent security updates to fix PHP2Shell, two serious flaws (CVE-2026-109618 and CVE-2026-109619) that let attackers run...
Read More
Update now! PHP2Shell: Critical PHP vulnerabilities patched

Trump says data centres should pay dividends to local community

US President Donald Trump said on Wednesday that companies ​building data centers should pay a "dividend" to the communities ‌where...
Read More
Trump says data centres should pay dividends to local community

Hackers Actively Exploiting Palo Alto VPN Flaw Via CVE-2026-0257

Ransomware groups are using a flaw in Palo Alto Networks GlobalProtect VPN to get around multi-factor authentication and access corporate...
Read More
Hackers Actively Exploiting Palo Alto VPN Flaw Via CVE-2026-0257

DeepSeek AI banned by U.S. Government; federal agencies must remove all related tools

The U.S. Department of Homeland Security (DHS) ordered federal agencies to stop using DeepSeek products and remove it from all...
Read More
DeepSeek AI banned by U.S. Government; federal agencies must remove all related tools

CISA, NSA and NIST Publish New 10 AI Agent Control Guidelines

NSA, CISA, and NIST have released security guidelines to find, control, and stop AI agents that go beyond their allowed...
Read More
CISA, NSA and NIST Publish New 10 AI Agent Control Guidelines

The documents contained full names, mailing addresses, Social Security Numbers, National Insurance Numbers, and Service Numbers. They also included sensitive details like rank, branch of service, dates, and locations that must remain confidential.

Fowler stated that the dataset was from Forces Penpals, a dating service and social network for military members and their supporters. The researcher reported an issue to the authorities, who restricted access of the dataset on the next day.

It is not clear how long the dataset was publicly available. Only an internal forensic audit can reveal any additional access or suspicious activity.

Source: VPNmentor

Maxar Space Data Leak, Company admit, Investigation ongoing!

Check Also

Fortinet

Hackers Exploit Fortinet Flaws to Deploy Stealthy PEERSTITCH Malware on FortiGate Firewalls

Cybersecurity researchers at Palo Alto Networks’ Unit 42 have uncovered a sophisticated cyberattack targeting Fortinet …