Friday , November 13 2026
Paloalto networks

Hacker compromised over 2000 Palo Alto Networks Firewalls

Over 2,000 Palo Alto Networks firewalls have been compromised in a widespread attack using two recently patched vulnerabilities (CVE-2024-0012 and CVE-2024-9474), according to Shadowserver Foundation’s internet scanning.

Palo Alto Networks security researchers reported on Wednesday that they detected a “limited set of exploitation activity” involving two vulnerabilities in PAN-OS, the operating system for their next-generation firewalls. These vulnerabilities are classified as zero-days because patches could not be released before they were exploited.

North Korean hackers steal more than $400 million using video images, FBI says

The United States Justice Department said Thursday it had seized cloud infrastructure used by North Korean hackers in a video-call...
Read More
North Korean hackers steal more than $400 million using video images, FBI says

Microsoft’s November 2026 Patch Tuesday addresses 1,093 flaws, with Outlook zero-day

Microsoft has shared its updates for November 2026. These updates fix 1,093 new flaws in Windows, Office, SQL Server, SharePoint,...
Read More
Microsoft’s November 2026 Patch Tuesday addresses 1,093 flaws, with Outlook zero-day

Barracuda ESG flaws exploited, gaining root access

Barracuda has confirmed active exploitation of security flaws affecting its Email Security Gateway (ESG), warning that attackers could combine two...
Read More
Barracuda ESG flaws exploited, gaining root access

Apple, SAP, and Ivanti Patch Critical flaws Affecting Messaging, Bluetooth, and Enterprise Systems

Apple, SAP, and Ivanti have published security updates that fix several flaws with messaging, Bluetooth, enterprise servers, and endpoint management...
Read More
Apple, SAP, and Ivanti Patch Critical flaws Affecting Messaging, Bluetooth, and Enterprise Systems

Jailbroken DeepSeek AI Agent Conducts Two-Week Cyberattack on European Telecom

A jailbroken AI has been attacking a European telecom company and 13 companies using its data center and cloud for...
Read More
Jailbroken DeepSeek AI Agent Conducts Two-Week Cyberattack on European Telecom

Daily Cyber security update for 10.11. 2026

Cyberattacks are rising around the world, including ransomware, malware, data leaks, and hacked websites. These events show how complex and...
Read More
Daily Cyber security update for 10.11. 2026

IBM fixes 208 API Connect vulnerabilities, 47 critical

IBM patched 208 security flaws in its API Connect platform. The CVE records released out on November 7, 2026. Among...
Read More
IBM fixes 208 API Connect vulnerabilities, 47 critical

89 New ransomware groups emerge in 2026, claiming over 2,200 victims

New ransomware actions in 2026 show more variety in cybercrime, with some groups claimed over 100 victims. The ransomware attack...
Read More
89 New ransomware groups emerge in 2026, claiming over 2,200 victims

Daily Cyber security update for 08.11. 2026

Cyberattacks are rising around the world, including ransomware, malware, data leaks, and hacked websites. These events show how complex and...
Read More
Daily Cyber security update for 08.11. 2026

Japan banking crisis
Outage causes disruption at 128 japan banks: preventing ATM transaction

A major system failure has brought customer-facing banking services to a standstill at 128 shinkin banks across western Japan, leaving...
Read More
Japan banking crisis  Outage causes disruption at 128 japan banks: preventing ATM transaction

CVE-2024-0012 is a vulnerability in Palo Alto Networks PAN-OS that lets unauthenticated attackers with network access to the management interface gain administrator privileges. This could enable them to perform administrative tasks, alter configurations, or exploit other vulnerabilities, such as CVE-2024-9474.

Palo Alto Networks’ Unit 42 research team has named the ongoing attack campaign “Operation Lunar Peek.” Since early November, attackers have been seen installing malware and executing commands on compromised firewalls, suggesting the presence of a public exploit chain.
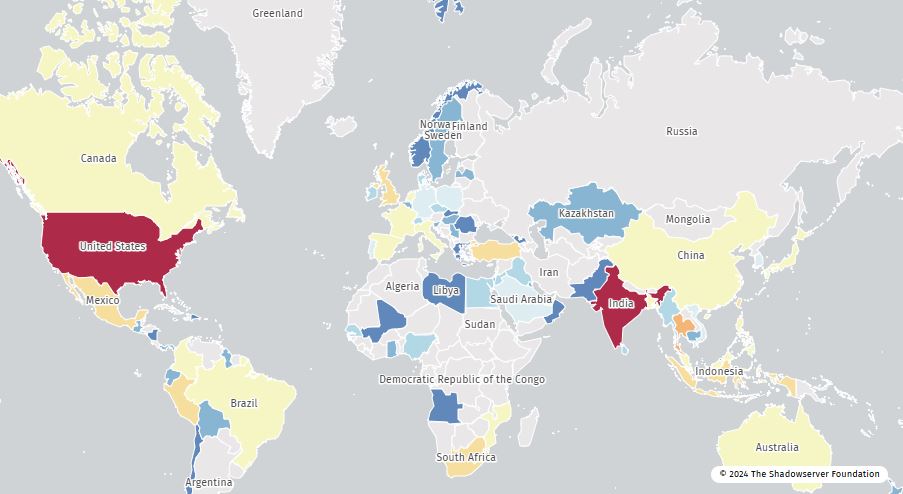
Source: Shadowserver Foundation

The Shadowserver Foundation reports that hackers have compromised over 2,000 Palo Alto Networks firewalls by exploiting two recently patched vulnerabilities. Most affected devices are in the United States, followed by India, with additional breaches in the UK, Australia, and China.

Organizations should review the security advisories for guidance on remediation.

Check Also

SAP

Apple, SAP, and Ivanti Patch Critical flaws Affecting Messaging, Bluetooth, and Enterprise Systems

Apple, SAP, and Ivanti have published security updates that fix several flaws with messaging, Bluetooth, …