InfoSecBulletin Cybersecurity for mankind
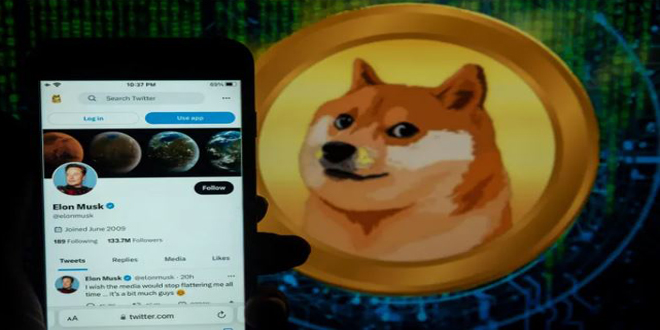
A vulnerability in Twitter’s code was recently discovered that allows users to game the algorithm with mass blocking actions from large numbers of accounts, in an effort to suppress specific users showing up in people’s feeds — essentially, it allows bot-created “shadow bans” in the parlance of social media censorship critics.
Now, the flaw has been assigned a CVE number as an officially recognized security vulnerability: CVE-2023-29218.
NetamLoader malware to attack Win10: Customized for Gov.t in Asia

‘SMS of Death’ Zero-Click Flaw Disrupting Android Phones With a Single Text

NIST Unveiled Guidance for Post-Quantum Cryptography Transition

Daily Cyber security update for 29.10. 2026

Rapid7 Unveils 17 Zimbra Collaboration Suite Flaws Breaking Identity Boundaries

CISA launched two free tools Identify Security Misconfig in Microsoft 365 and Google Workspace

Apple iOS 27.2 Released Fixes 163 Flaws, Including Critical WebKit RCE

CISA adds PHP2Shell to KEV, PHP Releases New Security Updates to Fix Critical HTTP2Shell flaw

Cloudflare Unveils Emergency WAF Ruleset Update on Brotli flaw

Daily Cyber security update for 26.10. 2026

“The Twitter Recommendation Algorithm through ec83d01 allows attackers to cause a denial of service (reduction of reputation score) by arranging for multiple Twitter accounts to coordinate negative signals regarding a target account, such as unfollowing, muting, blocking, and reporting, as exploited in the wild in March and April 2023,” the MITRE CVE entry explained.
The vulnerability was first flagged by infosec researcher Federico Andres Lois after analyzing Twitter’s source code, which was leaked to the public and later posted on GitHub by Twitter as part of its commitment to transparency.
The bug means that botnet armies have the ability to game the algorithm with mass blocks, mutes, abuse reports, spam reports, and unfollows to drive down the number of times specific accounts show up in Twitter’s recommendation engine.
“The current implementation allows for coordinated hurting of account reputation without recourse,” Lois wrote in his disclosure. “Any other time I would just report this information using a vulnerability channel, but given that this is already popular knowledge there is no use to do so.”
The vulnerability has since been discovered by others, prompting a cryptic, yet splashy, response from Twitter CEO Elon Musk.
“Who is behind these botnets?” Musk tweeted. “Million dollar bounty if convicted.”