 InfoSecBulletin Cybersecurity for mankind
Orange’s CERT Coordination Center discovered over 34.5K Cisco IOS XE devices compromised in CVE-2023-20198 attacks. Hackers have used a newly discovered and very serious software vulnerability to hack and infect more than 10,000 Cisco IOS XE devices with harmful software.
VulnCheck, a threat intelligence company, reported that a severe vulnerability (CVE-2023-20198) is being actively exploited in attacks on Cisco IOS XE systems with the Web User Interface (Web UI) enabled and the HTTP or HTTPS Server feature turned on.
Microsoft’s November 2026 Patch Tuesday addresses 1,093 flaws, with Outlook zero-day

Barracuda ESG flaws exploited, gaining root access

Apple, SAP, and Ivanti Patch Critical flaws Affecting Messaging, Bluetooth, and Enterprise Systems

Jailbroken DeepSeek AI Agent Conducts Two-Week Cyberattack on European Telecom

Daily Cyber security update for 10.11. 2026

IBM fixes 208 API Connect vulnerabilities, 47 critical

89 New ransomware groups emerge in 2026, claiming over 2,200 victims

Daily Cyber security update for 08.11. 2026

Japan banking crisis
Outage causes disruption at 128 japan banks: preventing ATM transaction

Daily Cyber security update for 06.11. 2026

VulnCheck found many infected hosts on internet-facing Cisco IOS XE web interfaces. The company also developed a scanner to identify these infections on affected devices.
“Cisco buried the lede by not mentioning thousands of internet-facing IOS XE systems have been implanted. This is a bad situation, as privileged access on the IOS XE likely allows attackers to monitor network traffic, pivot into protected networks, and perform any number of man-in-the-middle attacks,” said VulnCheck CTO Jacob Baines
.
“If your organization uses an IOS XE system, it’s imperative that you determine if your systems have been compromised and take appropriate action once implants have been discovered. While a patch is not yet available, you can protect your organization by disabling the web interface and removing all management interfaces from the internet immediately.”
”
VulnCheck has fingerprinted approximately 10,000 implanted systems, but we’ve only scanned approximately half of the devices listed on Shodan/Censys. We didn’t want to commit to a specific number as it’s evolving (increasing) as we continue our activities,” Baines told BleepingComputer.
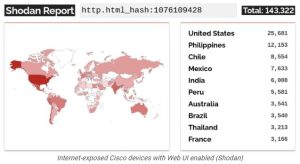
A Shodan search for Cisco devices with their Web UI enabled (shared by Aves Netsec CEO Simo Kohonen) currently shows more than 140,000 Internet-exposed devices.
Cisco: Apply mitigation measures and look for breach indicators
On Monday, Cisco disclosed that unauthenticated attackers can exploit the IOS XE zero-day to gain full administrator privileges and take complete control over affected Cisco routers and switches remotely.
The company cautioned administrators to disable the vulnerable HTTP server feature on all internet-facing systems until a patch becomes available.
Cisco detected the CVE-2023-20198 attacks in late September following reports of unusual behavior on a customer device received by Cisco’s Technical Assistance Center (TAC). Evidence of these attacks dates back to September 18, when the attackers were observed creating local user accounts named “cisco_tac_admin” and “cisco_support.”
Moreover, the attackers deployed malicious implants using CVE-2021-1435 exploits and other unknown methods, enabling them to execute arbitrary commands at the system or IOS levels on compromised devices.
“We assess that these clusters of activity were likely carried out by the same actor. Both clusters appeared close together, with the October activity appearing to build off the September activity,” Cisco said.
“The first cluster was possibly the actor’s initial attempt and testing their code, while the October activity seems to show the actor expanding their operation to include establishing persistent access via deployment of the implant.”
The company also issued a “strong recommendation” for administrators to look for suspicious or recently created user accounts as potential signs of malicious activity linked to this threat.
Source: Bleepingcomputer



