InfoSecBulletin Cybersecurity for mankind
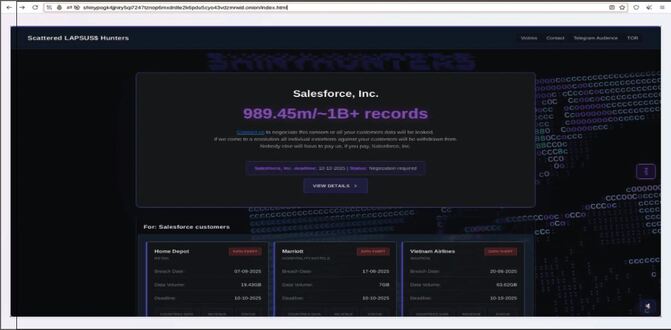
The Trinity of Chaos, a ransomware group linked to Lapsus$, Scattered Spider, and ShinyHunters, has created a Data Leak Site on the TOR network. This site includes data from 39 companies, such as Aeromexico, AirFrance, Google, Cisco, Stellantis, and Qantas Airlines, affected by attacks on weak Salesforce instances and other vulnerabilities.
Trinity of Chaos, a ransomware collective presumably associated with Lapsus$, Scattered Spider, and ShinyHunters. Resecurity’s previous report indicates that the group will continue its activities, now focusing on traditional ransomware.
WinRAR, WordPress RCE flaw & Zyxel GS1900 Zero-Day exploited in the wild

Daily Cyber security update for 04.11. 2026

Daily Cyber security update for 03.11. 2026

Using ARTEX AI, Hacker to attack 200 Organizations Across 14 Countries

Amadeus cyber incident impacted “Cathay Pacific, Qantas, Japan, Malaysia, Korean & Asiana” Airlines

Multiple European supermarket fridges got hacked: Temperatures reached high as 55°C

Apple Warns 99 Countries iPhone Users of Mercenary Spyware Attacks

Daily Cyber security update for 31.10. 2026

NetamLoader malware to attack Win10: Customized for Gov.t in Asia
‘SMS of Death’ Zero-Click Flaw Disrupting Android Phones With a Single Text
The Data Leak Site (DLS) lists recent victims like Stellantis, which revealed a data breach affecting North American customers on September 21, 2025. This followed an attack on Jaguar Land Rover that disrupted its retail and production.
Most leaked data samples don’t include passwords but have a lot of PII, suggesting they probably come from compromised Salesforce instances due to vishing attacks and stolen OAuth tokens linked to Salesloft’s Drift AI chat integration. This has led the FBI to issue a flash warning with technical indicators for organizations to check for potential intrusions in their Salesforce systems.
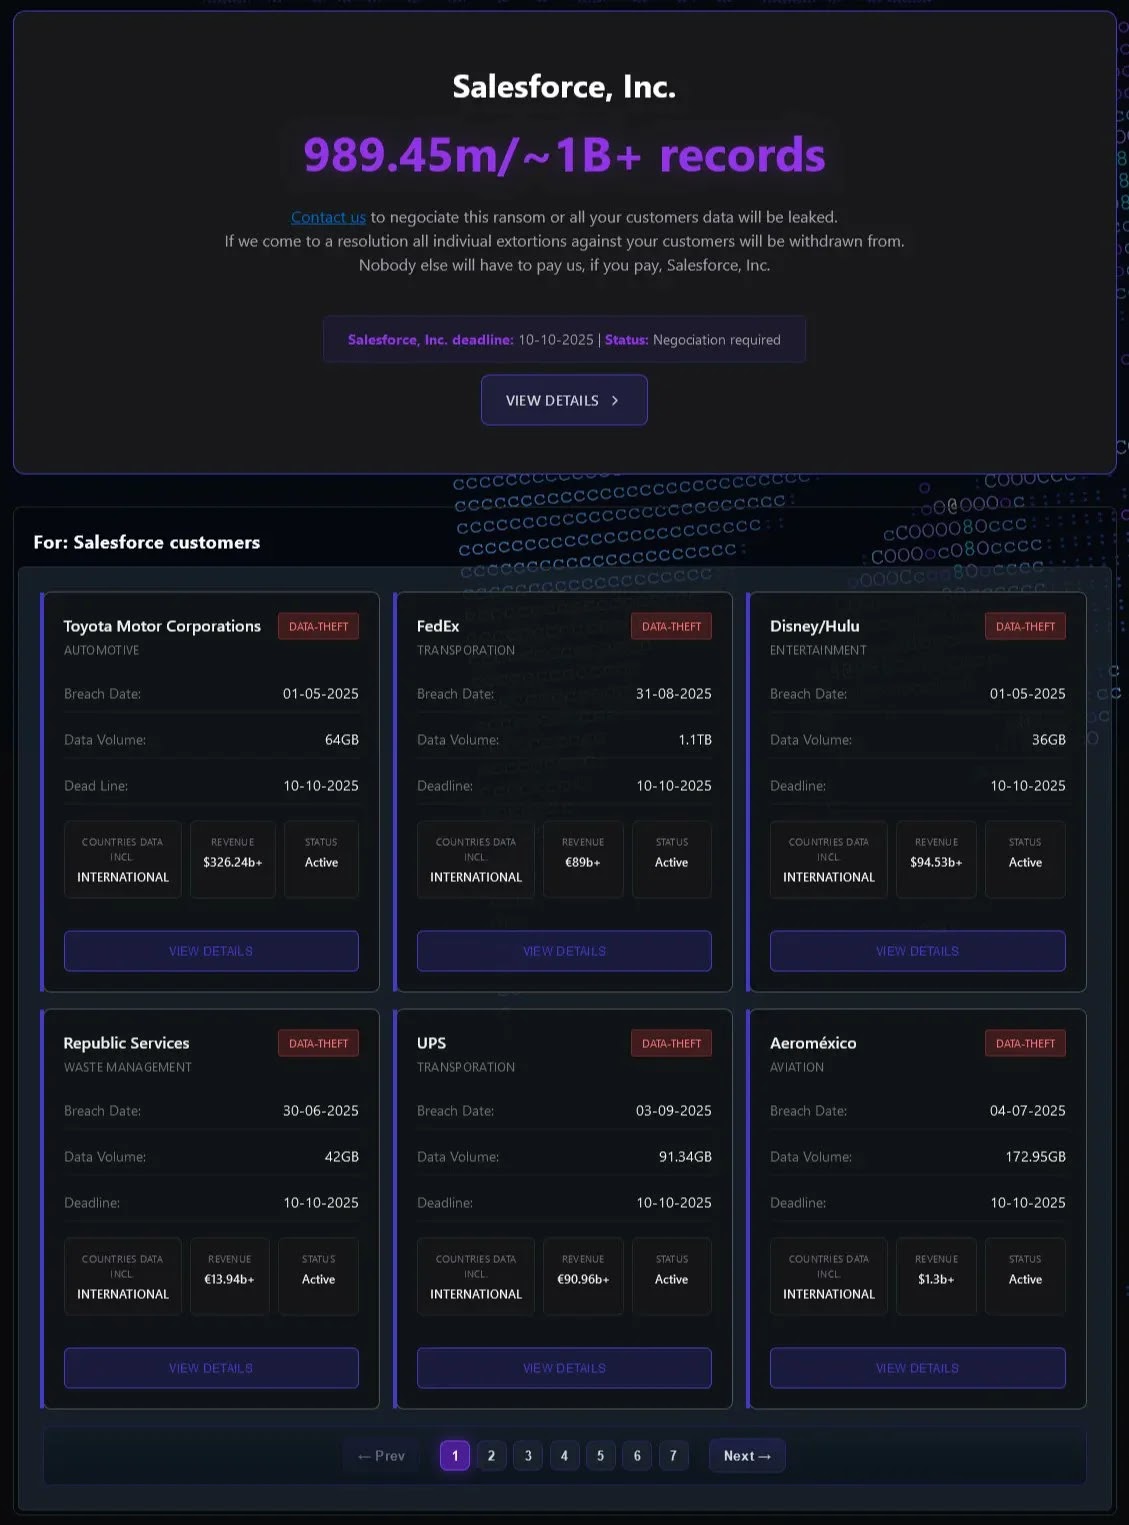
A Resecurity report has revealed a growing global cybercrime campaign led by LAPSUS$, ShinyHunters, and Scattered Spider. Despite claims of their “retirement,” this group continues to hack and extort large companies, with many significant data breaches still undisclosed. The report indicates an increase in private extortion efforts, suggesting the real impact of these hackers may be much larger than known. They also claim to have updated the Data Leak Site (DLS) after October 10, which now features over 1.5 billion records.
Resecurity analysts indicate that new victims and incidents are now surfacing. Ongoing extortion activities and the group’s reputation are pressuring companies to remain silent, revealing the extent of compromised data in the Fortune 100, financial, technology, aviation, retail, and auto sectors.
Cybersecurity experts warn that cybercriminals could use stolen data for harmful purposes, including in AI applications. They can analyze victim information to gain insights and connect data sets, enabling sophisticated social engineering, targeted phishing, and identity theft, particularly against large businesses and government entities.