InfoSecBulletin Cybersecurity for mankind
Bleeping Computer reported, these vulnerabilities were reported to Microsoft on September 7th and 8th, 2023. Microsoft acknowledges the reports but postpones the fixes for later.
ZDI disagreed with this response and decided to publish the flaws under its own tracking IDs to warn Exchange admins about the security risks.
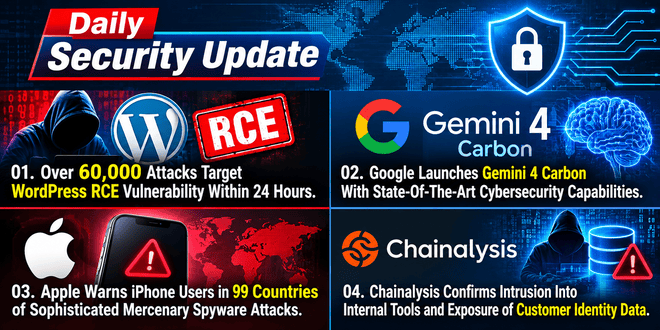
Apple Warns 99 Countries iPhone Users of Mercenary Spyware Attacks
Daily Cyber security update for 31.10. 2026
NetamLoader malware to attack Win10: Customized for Gov.t in Asia

‘SMS of Death’ Zero-Click Flaw Disrupting Android Phones With a Single Text

NIST Unveiled Guidance for Post-Quantum Cryptography Transition

Daily Cyber security update for 29.10. 2026

Rapid7 Unveils 17 Zimbra Collaboration Suite Flaws Breaking Identity Boundaries

CISA launched two free tools Identify Security Misconfig in Microsoft 365 and Google Workspace

Apple iOS 27.2 Released Fixes 163 Flaws, Including Critical WebKit RCE

CISA adds PHP2Shell to KEV, PHP Releases New Security Updates to Fix Critical HTTP2Shell flaw

Summarize of the vulnerabilities published by ZDI:
ZDI-23-1579 – Located in the ‘Download Data From Uri’ method, this flaw is due to insufficient validation of a URI before resource access. Attackers can exploit it to access sensitive information from Exchange servers.
ZDI-23-1580 – This vulnerability, in the ‘Download Data From Office Market Place’ method, also stems from improper URI validation, potentially leading to unauthorized information disclosure.
ZDI-23-1581 – Present in the Create Attachment From Uri method, this flaw resembles the previous bugs with inadequate URI validation, again, risking sensitive data exposure.
Authentication is needed to exploit these vulnerabilities, which makes them less severe with a CVSS rating between 7.1 and 7.5. Requiring authentication is a factor that helps reduce their impact. This could be why Microsoft did not prioritize fixing the bugs.
ALSO READ:
It should be noted, though, that cybercriminals have many ways to obtain Exchange credentials, including brute-forcing weak passwords, performing phishing attacks, purchasing them, or acquiring them from info-stealer logs.
That said, the above zero-days shouldn’t be treated as unimportant, especially ZDI-23-1578 (RCE), which can result in complete system compromise.
ZDI suggests that the only salient mitigation strategy is to restrict interaction with Exchange apps. However, this can be unacceptably disruptive for many businesses and organizations using the product.
We also suggest implementing multifactor authentication to prevent cybercriminals from accessing Exchange instances even when account credentials have been compromised.
Bleeping Computer has contacted Microsoft to ask about ZDI’s disclosure and are still waiting for a response.
Source: ZDI, Bleeping computer