 InfoSecBulletin Cybersecurity for mankind
Recently, McAfee’s Mobile Research Team discovered ‘Goldoson,’ a new type of Android malware, has crept into the Google Play store through 60 genuine apps, downloaded by a whopping 100 million users.
The sneaky malware component found in all 60 apps was not the developers’ fault. It had been slipped into a third-party library, which they unintentionally integrated into their apps.
Hacker claim to access Rajasthan Police data: 70,000 records allegedly exposed

Update now! PHP2Shell: Critical PHP vulnerabilities patched

Trump says data centres should pay dividends to local community

Hackers Actively Exploiting Palo Alto VPN Flaw Via CVE-2026-0257

DeepSeek AI banned by U.S. Government; federal agencies must remove all related tools

CISA, NSA and NIST Publish New 10 AI Agent Control Guidelines

Claude AI Cracks 25-Year NSA Cryptography Number Mystery in Just 30 Minutes

Bypassing firewalls, AI Agents Accessed Indian ‘ Data Without Permission: CERT-In

MITRE ATT&CK v20 Unveils 9 New Attack Techniques On AI Exploits, MFA Bypass, and CAPTCHA Evasion

Hackers Exploit Fortinet Flaws to Deploy Stealthy PEERSTITCH Malware on FortiGate Firewalls

While apart from this, there is good news for McAfee Mobile Security users, as the antivirus software now identifies the Goldoson menace as Android/Goldoson and shields its users against this threat, along with other threats.
Capabilities of Goldoson
Data or information that can be collected from affected devices by the malware include the following:-
- Data on installed apps
- WiFi connected devices
- Bluetooth connected devices
- User’s GPS location
- Location History
- MAC address of Bluetooth nearby
- MAC address of Wi-Fi nearby
Apart from this, Goldson not only infiltrates your device through legitimate apps but can also conduct ad fraud.
The malware can automatically click on ads in the background without your consent, potentially costing you time, money, and device performance.
List of Apps and Current Status
Here in the below table, we have mentioned all the apps and their current Status:-
- L.POINT with L.PAY (10M+, Updated*)
- Swipe Brick Breaker (10M+, Removed**)
- Money Manager Expense & Budget (10M+, Updated*)
- TMAP – 대리,주차,전기차 충전,킥보 … (10M+, Updated*)
- 롯데시네마 (10M+, Updated*)
- 지니뮤직 – genie (10M+, Updated*)
- 컬쳐랜드[컬쳐캐쉬] (5M+, Updated*)
- GOM Player (5M+, Updated*)
- 메가박스(Megabox) (5M+, Removed**)
- LIVE Score, Real-Time Score (5M+, Updated*)
- Pikicast (5M+, Removed**)
- Compass 9: Smart Compass (1M+, Removed**)
- GOM Audio – Music, Sync lyrics (1M+, Updated*)
- 곰TV – All About Video (1M+, Updated*)
- 전역일 계산기 디데이 곰신톡–군인 … (1M+, Updated*)
- 아이템매니아 – 게임 아이템 거래 … (1M+, Removed**)
- LOTTE WORLD Magicpass (1M+, Updated*)
- Bounce Brick Breaker (1M+, Removed**)
- Infinite Slice (1M+, Removed**)
- 나홀로 노래방–쉽게 찾아 이용하는 … (1M+, Updated*)
- SomNote – Beautiful note app (1M+, Removed**)
- Korea Subway Info : Metroid (1M+, Updated*)
- GOODTV다번역성경찬송 (1M+, Removed**)
- 해피스크린 – 해피포인트를 모으 … (1M+, Updated*)
- UBhind: Mobile Tracker Manager (1M+, Removed**)
- 스피드 운전면허 필기시험 … (1M+, Removed**)
- 이상형 월드컵 (500K+, Updated*)
- CU편의점택배 (500K+, Removed**)
- 스마트 녹음기 : 음성 녹음기 (100K+, Removed**)
- 캣메라 [순정 무음카메라] (100K+, Removed**)
- 컬쳐플러스:컬쳐랜드 혜택 더하기 … (100K+, Updated*)
- 창문닫아요(미세/초미세먼지/WHO … (100K+, Removed**)
- 롯데월드타워 서울스카이 (100K+, Updated*)
- Snake Ball Lover (100K+, Removed**)
- 게토(geto) – PC방 게이머 필수 앱 (100K+, Removed**)
- 기억메모 – 심플해서 더 좋은 메모장 (100K+, Removed**)
- 풀빵 : 광고 없는 유튜브 영상 … (100K+, Removed**)
- Money Manager (Remove Ads) (100K+, Updated*)
- Inssaticon – Cute Emoticons, K (100K+, Removed**)
- 클라우드런처 (100K+< Updated*)
- 작은영화관 (50K+, Updated*)
- 매표소–뮤지컬문화공연 예매& … (50K+, Updated*)
- 롯데월드 아쿠아리움 (50K+, Updated*)
- 롯데 워터파크 (50K+, Updated*)
- T map for KT, LGU+ (50K+, Removed**)
- 숫자 뽑기 (50K+, Updated*)
- 로더(Loader) – 효과음 다운로드 앱 (10K+, Removed**)
- GOM Audio Plus – Music, Sync l (10K+, Updated*)
- Swipe Brick Breaker 2 (10K+, Removed**)
- 안심해 – 안심귀가 프로젝트 (10K+, Removed**)
- 불러봄내 – 춘천시민을 위한 공공 … (10K+, Removed**)
- 판타홀릭 – 아이돌 SNS 앱 (5K+, Removed**)
- 씨네큐브 (5K+, Updated*)
- TNT (5K+, Removed**)
- 베스트케어–위험한 전자기장, … (1K+, Removed**)
- InfinitySolitaire (1K+, Removed**)
- 안심해 : 안심지도 (1K+, Removed**)
- 노티아이 for 소상공인 (1K+, Removed**)
- TDI News – 최초 데이터 뉴스 앱 … (1K+, Removed**)
- 눈팅 – 여자들의 커뮤니티 (500+, Removed**)
- 팅서치 TingSearch (50+, Removed**)
- 츄스틱 : 크리샤츄 Fantastic (50+, Removed**)
- 연하구곡 (10+, Removed**)
Technical Analysis
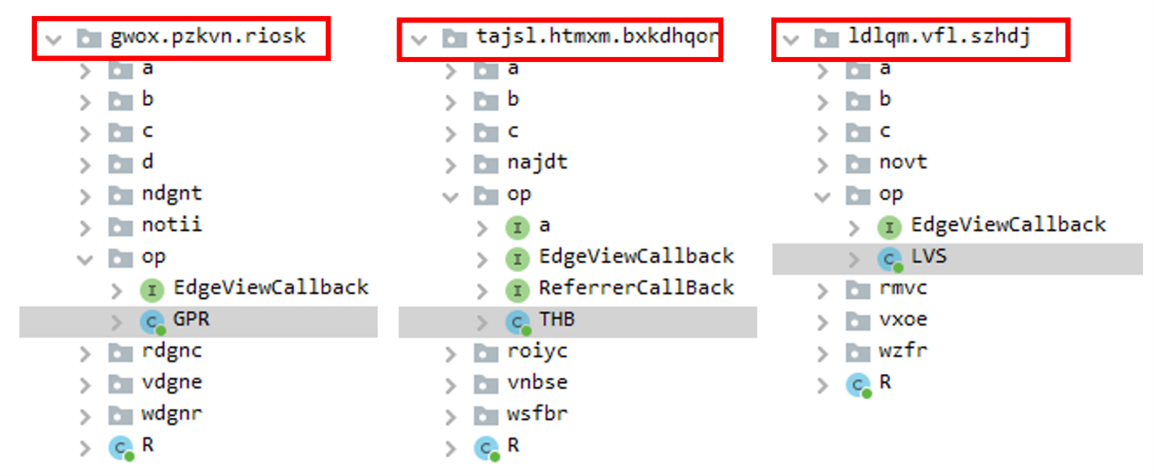
Security analysts have observed that the malicious Goldoson library is stealthy and smarter.
As it registers your device and receives remote configurations from a remote server whose domain is obfuscated while the app is active, putting your privacy at risk.
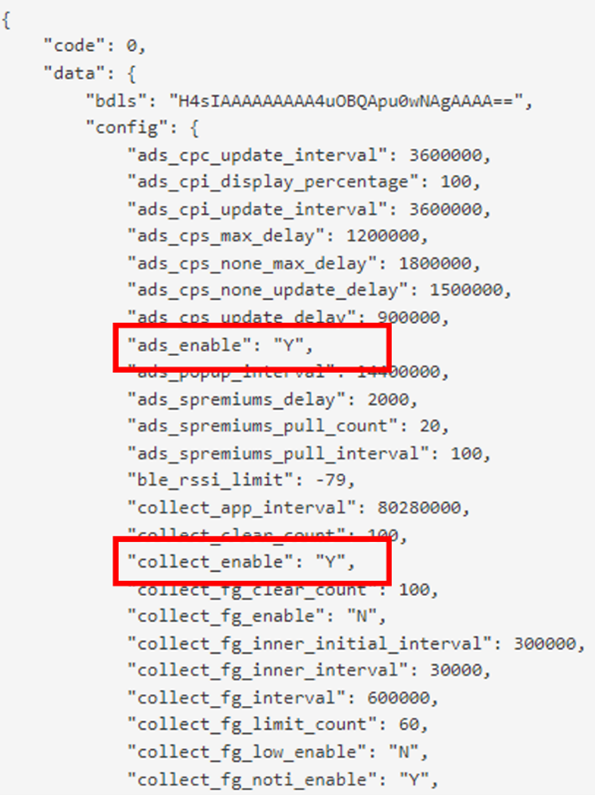
The remote configuration holds the key to the malware’s devastating impact. It determines the frequency of each component’s operation and defines the specific parameters for all the harmful functions.
This library checks periodically, pulls information from the device, and sends it to the remote servers based on its configured parameters.
The tags ‘ads_enable’ and ‘collect_enable’ serve as on/off switches for the malware’s various functions, while the other parameters outline the conditions and requirements for their operation. The malware can choose which functions to activate with these settings and when.
Two factors determine the extent of data collection by the Goldoson malware, and here below we have mentioned them:-
- The level of permissions granted to the infected app during installation.
- The specific Android version it is operating on.
While Android 11 and later versions are more secure against unapproved data collection.
But, besides all the security measures, McAfee detected that Goldson still managed to accumulate sensitive information from about 10% of the apps on these versions.
The malware’s ad-clicking function is quite sneaky – it loads hidden HTML code into a customized WebView and uses it to visit URLs repeatedly, all while remaining out of sight.
By doing so, the malware generates ad revenue without the user’s knowledge. The stolen data is transmitted every two days, but the remote configuration can alter the frequency.

The malware developers can modify the transmission rate to avoid detection and to keep up with their malicious activities.
Goldoson has infiltrated multiple Android app stores, with over 100 million downloads traced back to Google Play alone. Another app store, Korea’s biggest one, has approximately 8 million installations.
Users must remain vigilant and take precautions while downloading apps from unknown sources.



