InfoSecBulletin Cybersecurity for mankind
Cybersecurity researcher Jeremiah Fowler has uncovered a major data breach at ChoiceDNA, an Indiana-based firm offering DNA testing and facial recognition services involving biometric images and personal information.
Fowler reported to Infosecbulletin that around 8,000 sensitive documents, including biometric images and metadata, were publicly accessible without password protection.
Microsoft’s November 2026 Patch Tuesday addresses 1,093 flaws, with Outlook zero-day

Barracuda ESG flaws exploited, gaining root access

Apple, SAP, and Ivanti Patch Critical flaws Affecting Messaging, Bluetooth, and Enterprise Systems

Jailbroken DeepSeek AI Agent Conducts Two-Week Cyberattack on European Telecom

Daily Cyber security update for 10.11. 2026

IBM fixes 208 API Connect vulnerabilities, 47 critical

89 New ransomware groups emerge in 2026, claiming over 2,200 victims

Daily Cyber security update for 08.11. 2026

Japan banking crisis
Outage causes disruption at 128 japan banks: preventing ATM transaction

Daily Cyber security update for 06.11. 2026

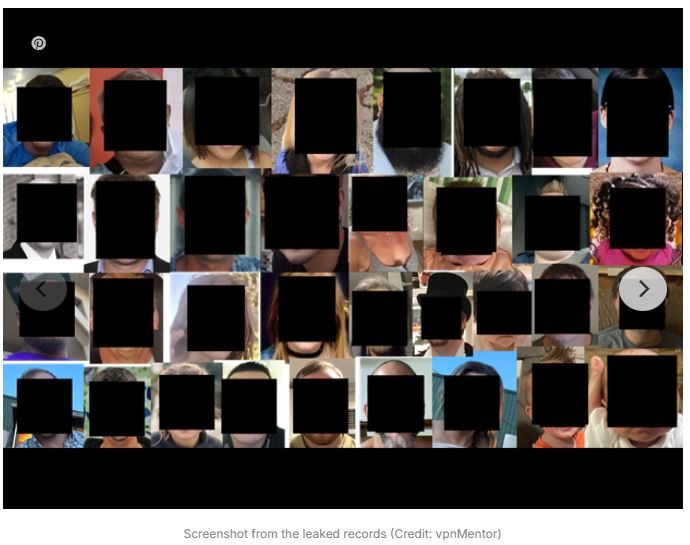
The unsecured WordPress folder exposed data that included facial recognition images and personally identifiable information (PII) like names, phone numbers, email addresses, and sensitive notes on DNA face matching tests.
Fowler’s findings indicate that the data was accessible for an unknown time, with the security flaw fixed only a week after it was reported. The full extent of the compromised data access is still unclear, pending a forensic audit.
Fowler explained hackread that Biometric data, such as facial recognition information, is highly sensitive and can be used to identify individuals, track their movements, and even manipulate their identities through deepfakes. Collecting, storing, and analyzing such data without explicit consent is a serious violation of individual privacy.
ChoiceDNA, an Indiana company that provides DNA testing and facial recognition services, may encounter ethical and legal issues due to these practices. Several U.S. states have strict biometric privacy laws, and the Federal Trade Commission (FTC) has warned about the risks of biometric data misuse, such as fraud and impersonation.
Fowler issued a responsible disclosure notice to the company, leading to the quick securing of the database. This incident emphasizes the importance of secure data storage. While WordPress is widely used, it can be vulnerable if not set up properly. In this case, sensitive data was stored in an unsecured WordPress folder, underscoring the need for strong security measures.
The incident highlights serious security issues with companies storing sensitive biometric data, especially those using WordPress. Experts suggest using more secure options like cloud solutions and implementing additional safeguards such as two-factor authentication (2FA) and Web Application Firewalls (WAF).
NIST unveils new password guidelines 2024: 11 rules to follow