InfoSecBulletin Cybersecurity for mankind
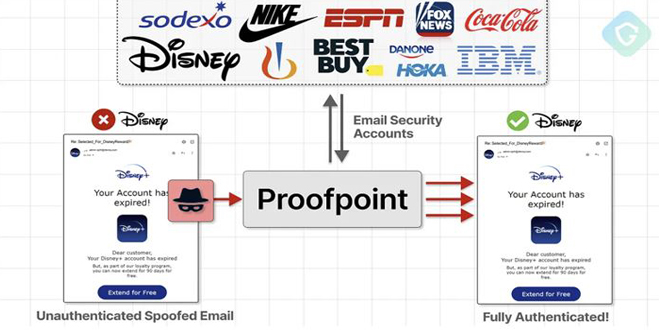
A scam campaign linked to an unknown threat actor is using an email routing misconfiguration in Proofpoint’s defenses to send millions of fake emails pretending to be from companies like Best Buy, IBM, Nike, and Walt Disney. Guardio Labs named the campaign EchoSpoofing.
It started in January 2024. The threat actor took advantage of a loophole and sent around three million emails per day on average. In early June, the number of emails reached a peak of 14 million as the company Proofpoint started to take action against it.
Daily Cyber security update for 14.11. 2026

Huge European telecom leak exposes clients of Swedbank, SEB, airBaltic, and other companies

PHP2Shell attack exploited a Check Point 0-day to deploy malware

North Korean hackers steal more than $400 million using video images, FBI says

Microsoft’s November 2026 Patch Tuesday addresses 1,093 flaws, with Outlook zero-day

Barracuda ESG flaws exploited, gaining root access

Apple, SAP, and Ivanti Patch Critical flaws Affecting Messaging, Bluetooth, and Enterprise Systems

Jailbroken DeepSeek AI Agent Conducts Two-Week Cyberattack on European Telecom

Daily Cyber security update for 10.11. 2026

IBM fixes 208 API Connect vulnerabilities, 47 critical

The Hacker News reported “These emails echoed from official Proofpoint email relays with authenticated SPF and DKIM signatures, thus bypassing major security protections — all to deceive recipients and steal funds and credit card details,”.
“The most unique and powerful part of this domain is the spoofing method – leaving almost no chance to realize this is not a genuine email sent from those companies,” Guardio Labs researcher Nati Tal told.
“This EchoSpoofing concept is really powerful. It’s kind of strange it is being used for large-scale phishing like this instead of a boutique spear-phishing campaign – where an attacker can swiftly take any real company team member’s identity and send emails to other co-workers – eventually, through high-quality social engineering, get access to internal data or credentials and even compromise the entire company.
The technique utilizes an SMTP server on a virtual private server (VPS) to send messages, ensuring compliance with authentication and security measures like SPF and DKIM. Click here to read the full report.