 InfoSecBulletin Cybersecurity for mankind
Fluent Bit, a widely used logging utility, has a critical vulnerability. This vulnerability can lead to denial-of-service attacks, information disclosure, and potentially remote code execution (RCE). Tenable, a cybersecurity firm, discovered this vulnerability.
Fluent Bit is an open source tool that collects and processes large amounts of log data from various sources. It has billions of downloads and is being deployed over 10 million times daily.
Apple Warns 99 Countries iPhone Users of Mercenary Spyware Attacks
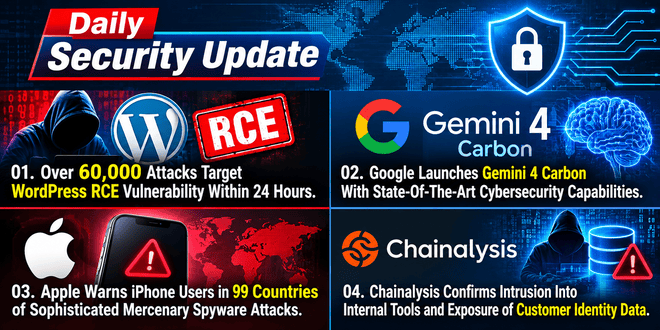
Daily Cyber security update for 31.10. 2026
NetamLoader malware to attack Win10: Customized for Gov.t in Asia

‘SMS of Death’ Zero-Click Flaw Disrupting Android Phones With a Single Text

NIST Unveiled Guidance for Post-Quantum Cryptography Transition

Daily Cyber security update for 29.10. 2026

Rapid7 Unveils 17 Zimbra Collaboration Suite Flaws Breaking Identity Boundaries

CISA launched two free tools Identify Security Misconfig in Microsoft 365 and Google Workspace

Apple iOS 27.2 Released Fixes 163 Flaws, Including Critical WebKit RCE

CISA adds PHP2Shell to KEV, PHP Releases New Security Updates to Fix Critical HTTP2Shell flaw

Developers claim it’s used by big cloud companies like Microsoft, Google Cloud, and AWS, as well as tech giants like Cisco, LinkedIn, VMware, Splunk, Intel, Arm, and Adobe.
Tenable researchers discovered a critical memory corruption vulnerability in Fluent Bit’s built-in HTTP server. The vulnerability is named Linguistic Lumberjack and has been assigned the official identifier CVE-2024-4323.
The cybersecurity firm confirmed that if someone has access to the Fluent Bit monitoring API, they can launch a DoS attack or obtain sensitive information.
Exploiting CVE-2024-4323 for RCE may be possible, but it depends on factors like the operating system and host architecture.
“While heap buffer overflows such as this are known to be exploitable, creating a reliable exploit is not only difficult, but incredibly time intensive,” Tenable explained.
On Monday, the company released technical information and a proof-of-concept (PoC) exploit for DoS attacks.
Tenable shared its findings with Fluent Bit developers in April, but the patch has not been officially released yet. The security firm also informed Microsoft, AWS, and Google Cloud about the findings on May 15th.
Users can implement mitigations for Fluent Bit by restricting access to the tool’s API and disabling any unused endpoints.



