InfoSecBulletin Cybersecurity for mankind
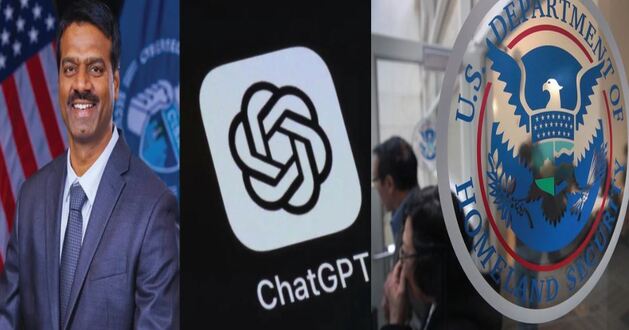
The acting director of the Cybersecurity and Infrastructure Security Agency (CISA) uploaded sensitive contracting documents marked “for official use only” into the public version of ChatGPT last summer, triggering multiple automated security alerts designed to prevent data exfiltration from federal networks, four Department of Homeland Security (DHS) officials told Politico.
Madhu Gottumukkala, CISA’s interim head since May 2025, had secured special permission from the agency’s Chief Information Officer to use the AI tool shortly after joining.
Daily Cyber security update for 25. 10. 2026

Daily Cyber security update for 24. 10. 2026

PHP shares new RCE flaw (CVE 2026-115560) with no patch but mitigation

US banks faced unauthorized access by AI agents in customer accounts: Axios reports

Atlassian patched 176 flaw in Jira and Confluence: Fortinet Urges to Patch Flaws Affecting FortiOS, FortiManager

Hacker claim to access Rajasthan Police data: 70,000 records allegedly exposed

Update now! PHP2Shell: Critical PHP vulnerabilities patched

Trump says data centres should pay dividends to local community

Hackers Actively Exploiting Palo Alto VPN Flaw Via CVE-2026-0257

DeepSeek AI banned by U.S. Government; federal agencies must remove all related tools

At the time, ChatGPT remained blocked for other DHS staff. The uploads occurred in early August 2025, with cybersecurity sensors repeatedly flagging them with multiple warnings in the first week alone. None of the files were classified, but they contained sensitive contracting information not meant for public release.
CISA’s defenses detected the activity, prompting senior DHS officials to launch an internal review to evaluate potential harm to national security.
Gottumukkala discussed the uploads with DHS leaders, including then-acting general counsel Joseph Mazzara and Chief Information Officer Antoine McCord. He also met with CISA’s CIO Robert Costello and chief counsel Spencer Fisher in August to address the handling of “for official use only” (FOUO) material.
DHS policy mandates investigating such exposures, assessing causes, and considering actions from retraining to security clearance revocation. One anonymous official criticized Gottumukkala harshly: “He forced CISA’s hand into making them give him ChatGPT, and then he abused it.” The review’s outcome remains undisclosed.
Public ChatGPT shares user inputs with OpenAI, which boasts over 700 million active users. This risks sensitive data training models accessible to adversaries, including state-backed hackers from Russia and China, precisely the threats CISA counters.
CISA spokesperson Marci McCarthy stated Gottumukkala used ChatGPT “with DHS controls in place” under a “short-term and limited” exception, last accessing it in mid-July 2025. She emphasized the agency’s AI commitment per President Trump’s executive order.
In contrast, approved DHS tools, such as the internal DHSChat, store data on federal networks. All federal employees receive training on handling sensitive documents.
Gottumukkala’s tenure has drawn scrutiny. Six career staff members were placed on leave after his unsanctioned counterintelligence polygraph failure.
In testimony, he denied the “failed test” premise. Last week, he attempted to oust Costello, but was blocked by appointees, as reported by Politico.