Friday , June 13 2025
Alert, Vulnerabilities
Serious security vulnerabilities in Trend Micro Apex One could allow attackers to inject malicious code and elevate their privileges within the system. The company issued emergency patches on June 9, 2025, for five vulnerabilities (CVE-2025-49154 to CVE-2025-49158) rated medium to high on the CVSS 3.0 scale. CVE-2025-49154: Insecure Access Control …
Read More »
Thursday , June 12 2025
Alert, Hot Topic, Vulnerabilities
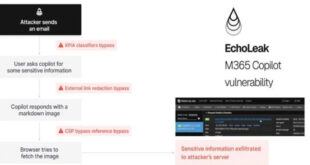
Aim Labs discovered a zero-click AI vulnerability named “EchoLeak” in Microsoft 365 Copilot and reported several ways to exploit it to Microsoft’s MSRC team. The new attack method called “LLM Scope Violation” has been identified, which could also impact other RAG-based chatbots and AI agents. This finding marks a significant …
Read More »
Wednesday , June 11 2025
Alert, Hot Topic, International, Vulnerabilities
Microsoft’s June Patch Tuesday update has arrived, addressing 66 vulnerabilities across its product line. One of these flaws was actively being exploited, making this update crucial for both businesses and individual users. One Zero-Day Actively Exploited: The important fix addresses CVE-2025-33053, a vulnerability in Windows WebDAV that could let attackers …
Read More »
Tuesday , June 10 2025
Alert, Cyber Attack, Vulnerabilities
More than 84,000 Roundcube webmail installations are at risk due to CVE-2025-49113, a severe remote code execution (RCE) vulnerability that comes with an available public exploit. The flaw in Roundcube (versions 1.1.0 to 1.6.10) was discovered by Kirill Firsov and was patched on June 1, 2025. The bug stems from …
Read More »
Monday , June 9 2025
Alert, Cyber Attack, Vulnerabilities
The Security Intelligence and Response Team (SIRT) at Akamai has found that multiple Mirai-based botnets are exploiting CVE-2025-24016, a critical RCE vulnerability in Wazuh servers. This flaw, which has a CVSS score of 9.9, allows remote attackers to execute arbitrary Python code through unsanitized JSON inputs in the Wazuh Distributed …
Read More »
Sunday , June 8 2025
Alert, Vulnerabilities
On June 5, 2025, CISA released seven advisories regarding Industrial Control Systems (ICS) that highlight current security issues, vulnerabilities, and exploits. ICSA-25-155-01 CyberData 011209 SIP Emergency Intercom ICSA-25-155-02 Hitachi Energy Relion 670, 650 series and SAM600-IO Product ICSA-21-049-02 Mitsubishi Electric FA Engineering Software Products (Update H) ICSA-25-133-02 Hitachi Energy Relion …
Read More »
Thursday , June 5 2025
Alert, Cyber Attack, Vulnerabilities
Cisco fixed a critical vulnerability in the Identity Services Engine (ISE) that could let unauthorized attackers carry out harmful actions. The vulnerability, CVE-2025-20286 (CVSS score 9.9), affects Cisco ISE on AWS, Microsoft Azure, and Oracle Cloud. It allows unauthenticated remote attackers to access sensitive data, perform basic admin tasks, modify …
Read More »
Tuesday , June 3 2025
Alert, Vulnerabilities
Qualcomm has issued security patches for three zero-day vulnerabilities in the Adreno GPU driver, affecting many chipsets that are being actively exploited in targeted attacks. The company reported two major flaws (CVE-2025-21479 and CVE-2025-21480) identified by the Google Android Security team in late January, and a third serious vulnerability (CVE-2025-27038) …
Read More »
Monday , June 2 2025
Alert, Vulnerabilities
Roundcube Webmail has fixed a critical security flaw that could enable remote code execution after authentication. Disclosed by security researcher firs0v, the issue has been addressed in the latest updates for the 1.6 and 1.5 LTS versions. The security update addresses a post-authentication RCE vulnerability caused by PHP object deserialization. …
Read More »
Saturday , May 31 2025
Vulnerabilities
The Qualys Threat Research Unit (TRU) found two local information-disclosure vulnerabilities in Apport and systemd-coredump. Both issues are race-condition vulnerabilities. CVE-2025-5054 affects Ubuntu’s core-dump handler, Apport, while CVE-2025-4598 targets systemd-coredump, the default core-dump handler on Red Hat Enterprise Linux 9 and 10, as well as Fedora. These vulnerabilities allow a …
Read More »
 InfoSecBulletin Cybersecurity for mankind