Sunday , November 8 2026

Alert

CVE-2025-30401
Alert! WhatsApp Vuls Let Attackers Execute Malicious Code
WhatsApp

The spoofing vulnerability, CVE-2025-30401, impacts all WhatsApp Desktop versions for Windows before 2.2450.6, posing a risk to users dealing with attachments on the platform. According to the official security advisory, the application “displayed attachments according to their MIME type but selected the file opening handler based on the attachment’s filename …

Read More »

CVE-2025-1268
Patch urgently! Canon Fixes Critical Printer Driver Flaw

Canon

Canon has announced a critical security vulnerability, CVE-2025-1268, in printer drivers for its production printers, multifunction printers, and laser printers. This out-of-bounds issue may disrupt printing or allow malicious code execution when processed by a harmful application. The affected printer drivers include several versions of Canon’s Generic Plus drivers: Generic …

Read More »

Australian fintech database exposed in 27000 records

Australian fintech

Cybersecurity researcher Jeremiah Fowler recently revealed a sensitive data exposure involving the Australian fintech company Vroom by YouX, previously known as Drive IQ. Fowler, in a report to Website Planet, found an unsecured Amazon S3 bucket with 27,000 records. This database contained sensitive personal information, such as driver’s licenses, medical …

Read More »

Over 200 Million Info Leaked Online Allegedly Belonging to X

200 million

Safety Detectives’ Cybersecurity Team found a forum post where a threat actor shared a .CSV file with over 200 million records from X users. The team discovered data in a forum post on the surface web. This popular forum features message boards for database downloads, leaks, cracks, and similar topics. …

Read More »

Splunk Alert User RCE and Data Leak Vulns

Splunk

Splunk has released a security advisory about critical vulnerabilities in Splunk Enterprise and Splunk Cloud Platform. These issues could lead to remote code execution and unauthorized access to sensitive information. CVE-2025-20229: Remote Code Execution via Unauthorized File Upload (CVSS 8.0): CVE-2025-20229 highlights that low-privileged users can pose significant risks by …

Read More »

Micropatches released for Windows zero-day leaking NTLM hashes

NTLM

Unofficial patches are available for a new Windows zero-day vulnerability that allows remote attackers to steal NTLM credentials by deceiving targets into opening malicious files in Windows Explorer. NTLM has been widely exploited in NTLM relay attacks (where threat actors force vulnerable network devices to authenticate to attacker-controlled servers) and …

Read More »

IngressNightmare
Over 40% of cloud environments are vulnerable to RCE

RCE

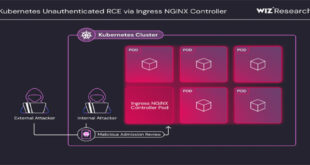
Kubernetes users of the Ingress NGINX Controller are advised to fix four newly found remote code execution ( RCE) vulnerabilities, which have a CVSS score of 9.8. Wiz Security named four vulnerabilities “IngressNightmare” that affect the admission controller of the popular open-source software used for directing external traffic to Kubernetes …

Read More »