 InfoSecBulletin Cybersecurity for mankind
In recent time, Hacker exploited Windows, VMware and Linux flaw. On another side, Australia warn about of BadCandy infections on unpatched Cisco devices.
VMware:
Microsoft’s November 2026 Patch Tuesday addresses 1,093 flaws, with Outlook zero-day

Barracuda ESG flaws exploited, gaining root access

Apple, SAP, and Ivanti Patch Critical flaws Affecting Messaging, Bluetooth, and Enterprise Systems

Jailbroken DeepSeek AI Agent Conducts Two-Week Cyberattack on European Telecom

Daily Cyber security update for 10.11. 2026

IBM fixes 208 API Connect vulnerabilities, 47 critical

89 New ransomware groups emerge in 2026, claiming over 2,200 victims

Daily Cyber security update for 08.11. 2026

Japan banking crisis
Outage causes disruption at 128 japan banks: preventing ATM transaction

Daily Cyber security update for 06.11. 2026

CISA added a serious security flaw affecting Broadcom VMware Tools and VMware Aria Operations to its Known Exploited Vulnerabilities list after reports of ongoing exploitation.
The vulnerability CVE-2025-41244 (CVSS score: 7.8) could allow an attacker to gain root access on vulnerable systems.
“Broadcom VMware Aria Operations and VMware Tools contain a privilege defined with unsafe actions vulnerability,” CISA said in an alert. “A malicious local actor with non-administrative privileges having access to a VM with VMware Tools installed and managed by Aria Operations with SDMP enabled may exploit this vulnerability to escalate privileges to root on the same VM.”
Linux:
CISA has issued an urgent alert about a serious use-after-free vulnerability in the Linux kernel, known as CVE-2024-1086.
This vulnerability, hidden within the netfilter: nf_tables component, allows local attackers to escalate their privileges and potentially deploy ransomware, which could severely disrupt enterprise systems worldwide.
Cisco:
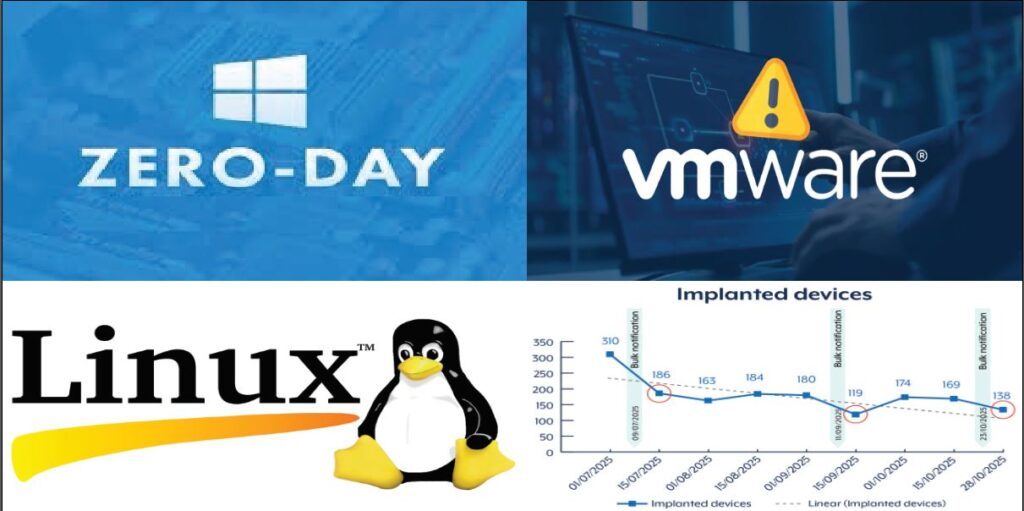
The Australian government warns of ongoing cyberattacks on unpatched Cisco IOS XE devices, targeting routers with the BadCandy webshell. The attacks exploit CVE-2023-20198, a severe vulnerability that enables remote attackers to create a local admin user through the web interface and gain control of devices.
Cisco fixed the flaw in October 2023, which was then marked as an actively exploited issue. A public exploit became available two weeks later, fueling mass exploitation for backdoor planting on internet-exposed devices.
The Australian authorities have warned that variants of the same Lua-based BadCandy web shells are still used in attacks throughout 2024 and 2025, indicating that many Cisco devices remain unpatched.
“Since July 2025, ASD assesses over 400 devices were potentially compromised with BADCANDY in Australia,” reads the bulletin. “As at late October 2025, there are still over 150 devices compromised with BADCANDY in Australia.”
Windows:
A China-linked hacking group is using a Windows zero-day to target European diplomats in Hungary, Belgium, and other countries.
Arctic Wolf Labs states that the attack starts with spearphishing emails that deliver harmful LNK files related to NATO defense workshops, European Commission border meetings, and other diplomatic events.
Malicious files exploit a severe Windows LNK vulnerability (CVE-2025-9491) to install the PlugX RAT, enabling attackers to monitor diplomatic communications and steal sensitive data.
The cyber-espionage campaign has been attributed to a Chinese state-backed threat group tracked as UNC6384 (Mustang Panda), known for conducting espionage operations aligned with Chinese strategic interests and targeting diplomatic entities across Southeast Asia.
Research from Arctic Wolf Labs and StrikeReady shows that malware attacks have expanded recently. Initially aimed at Hungarian and Belgian diplomats, they now also include Serbian government bodies and diplomatic offices from Italy and the Netherlands.
“Arctic Wolf Labs assesses with high confidence that this campaign is attributable to UNC6384, a Chinese-affiliated cyber espionage threat actor,” the researchers said. “This attribution is based on multiple converging lines of evidence including malware tooling, tactical procedures, targeting alignment, and infrastructure overlaps with previously documented UNC6384 operations.”



