InfoSecBulletin Cybersecurity for mankind
Cybersecurity researcher Jeremiah Fowler discovered a non-password-protected database with 520,054 records from an event ticket resale platform and reported it to vpnMentor.
The unprotected public database had 520,054 records totaling 200 GB. It was labeled as containing customer inventory files in PDF, JPG, PNG, and JSON formats. A review of the files revealed many concert and event tickets, ticket transfer proofs, and user-submitted receipts. Some documents included partial credit card numbers, full names, email addresses, and home addresses.
Rapid7 Unveils 17 Zimbra Collaboration Suite Flaws Breaking Identity Boundaries

CISA launched two free tools Identify Security Misconfig in Microsoft 365 and Google Workspace

Apple iOS 27.2 Released Fixes 163 Flaws, Including Critical WebKit RCE

CISA adds PHP2Shell to KEV, PHP Releases New Security Updates to Fix Critical HTTP2Shell flaw

Cloudflare Unveils Emergency WAF Ruleset Update on Brotli flaw

Daily Cyber security update for 26.10. 2026

The Washington Post report
Ex-DOGE AI startup Cathedral Breaches Anthropic Internal Systems within 12 Hours

Daily Cyber security update for 25. 10. 2026

Daily Cyber security update for 24. 10. 2026

PHP shares new RCE flaw (CVE 2026-115560) with no patch but mitigation

Jeremiah Fowler reported that internal files showed the records belonged to Ticket to Cash, an online ticket resale platform. It took several days and a follow-up notice before the database was restricted from public access. During the four days between the initial and second disclosure, over two thousand more records were exposed.
Data exposure involving Personally Identifiable Information (PII) can lead to various malicious activities, with identity theft being the primary concern when sensitive data like SSNs or dates of birth are leaked. Even with just names, email addresses, physical addresses, and partial financial data, scammers can build a fuller profile of victims for ongoing exploitation.
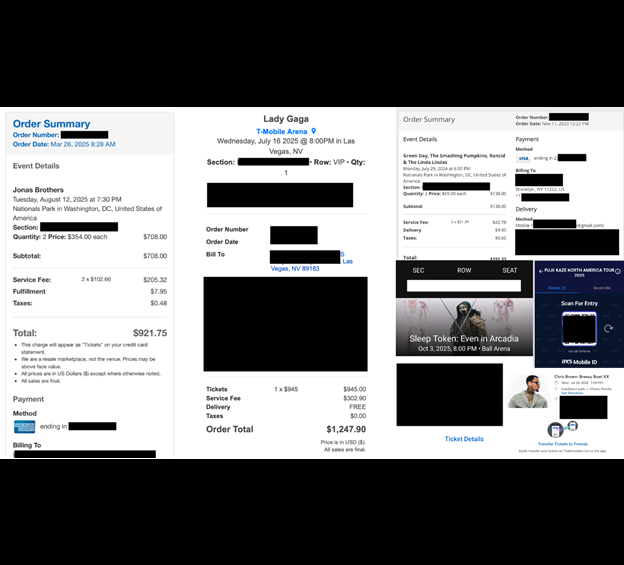
Jeremiah Fowler said tickets for several thousand dollars that were valid for up to 6-7 months in the future. This could hypothetically provide the financial incentive and enough time for a sophisticated attack on the account, counterfeiting, or other fraudulent activity.
A 2023 LendingTree report revealed that 11% of ticket buyers on secondary markets or unreliable sites were scammed. The Guardian reported a 529% increase in ticket scams in the UK last year, with victims averaging a loss of £110 ($145).
Jeremiah Fowler recommend that individuals who believe they may have been affected by a data breach be vigilant:
Monitor your financial accounts for unusual activity and periodically check your credit reports for any new accounts in your name.
Update passwords for any potentially compromised online accounts, and enable multi-factor authentication (MFA) whenever possible for extra security.
Stay alert for phishing attempts, especially emails about ticket purchases or payment issues. Always verify such messages through official channels, and report any suspicious activity to your bank, credit card provider, or relevant service provider.
TicketToCash.com is an online platform where people can sell tickets for concerts, sports, and theater events. It connects users to over 1,000 resale websites. Sellers can list their tickets for free, but Ticket to Cash takes a commission once a sale is made. If tickets don’t sell, the seller loses the full ticket value.