 InfoSecBulletin Cybersecurity for mankind
Palo Alto Networks has revealed a high severity vulnerability in PAN-OS software that may lead to a denial-of-service (DoS) issue on affected devices.
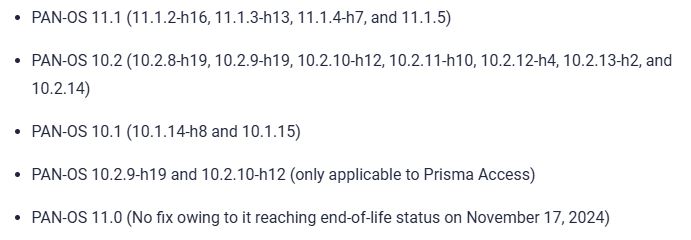
The vulnerability CVE-2024-3393 (CVSS score: 8.7) affects PAN-OS versions 10.X and 11.X, and Prisma Access with PAN-OS versions 10.2.8 or later and before 11.2.3. It has been fixed in PAN-OS versions 10.1.14-h8, 10.2.10-h12, 11.1.5, 11.2.3, and all newer versions.
US banks faced unauthorized access by AI agents in customer accounts: Axios reports

Atlassian patched 176 flaw in Jira and Confluence: Fortinet Urges to Patch Flaws Affecting FortiOS, FortiManager

Hacker claim to access Rajasthan Police data: 70,000 records allegedly exposed

Update now! PHP2Shell: Critical PHP vulnerabilities patched

Trump says data centres should pay dividends to local community

Hackers Actively Exploiting Palo Alto VPN Flaw Via CVE-2026-0257

DeepSeek AI banned by U.S. Government; federal agencies must remove all related tools

CISA, NSA and NIST Publish New 10 AI Agent Control Guidelines

Claude AI Cracks 25-Year NSA Cryptography Number Mystery in Just 30 Minutes

Bypassing firewalls, AI Agents Accessed Indian ‘ Data Without Permission: CERT-In

“A denial-of-service vulnerability in the DNS Security feature of Palo Alto Networks PAN-OS software allows an unauthenticated attacker to send a malicious packet through the data plane of the firewall that reboots the firewall,” the company said in a Friday advisory.
“Repeated attempts to trigger this condition will cause the firewall to enter maintenance mode.”
Palo Alto Networks said it discovered the flaw in production use, and that it’s aware of customers “experiencing this denial-of-service (DoS) when their firewall blocks malicious DNS packets that trigger this issue.”
The activity’s scope is currently unclear. Hacker News has contacted Palo Alto Networks for comment and will update the story if they respond.
Firewalls with DNS Security logging enabled are affected by CVE-2024-3393. The flaw’s severity is reduced to a CVSS score of 7.1 when access is limited to authenticated users through Prisma Access.
The fixes have also been extended to other commonly deployed maintenance releases –
As workarounds and mitigations for unmanaged firewalls or those managed by Panorama, customers have the option of setting Log Severity to “none” for all configured DNS Security categories for each Anti-Spyware profile by navigating to Objects > Security Profiles > Anti-spyware > (select a profile) > DNS Policies > DNS Security.
Users can disable DNS Security logging on firewalls managed by Strata Cloud Manager (SCM) either individually or for all devices by opening a support case. For Prisma Access tenants, it’s recommended to open a support case to disable logging until an upgrade is performed.



