InfoSecBulletin Cybersecurity for mankind
MANILA, Philippines —A staggering 1,279,437 records belonging to law enforcement agencies, including sensitive police employee information, have been compromised in an unprecedented data breach, as revealed by a report from the leading cybersecurity research company VPNMentor on Tuesday.
Exposed records encompass highly sensitive data such as fingerprint scans, birth certificates, tax identification numbers (TIN), tax filing records, academic transcripts, and even passport copies.
Microsoft’s November 2026 Patch Tuesday addresses 1,093 flaws, with Outlook zero-day

Barracuda ESG flaws exploited, gaining root access

Apple, SAP, and Ivanti Patch Critical flaws Affecting Messaging, Bluetooth, and Enterprise Systems

Jailbroken DeepSeek AI Agent Conducts Two-Week Cyberattack on European Telecom

Daily Cyber security update for 10.11. 2026

IBM fixes 208 API Connect vulnerabilities, 47 critical

89 New ransomware groups emerge in 2026, claiming over 2,200 victims

Daily Cyber security update for 08.11. 2026

Japan banking crisis
Outage causes disruption at 128 japan banks: preventing ATM transaction

Daily Cyber security update for 06.11. 2026

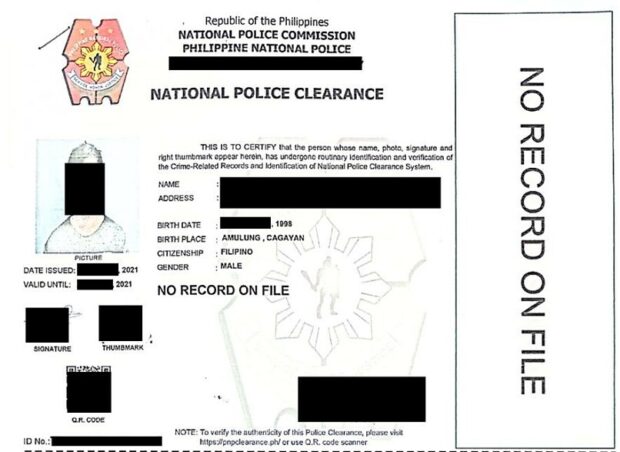
Sample of a criminologist accreditation, police clearance form, and BIR identification card, all available on the exposed database.
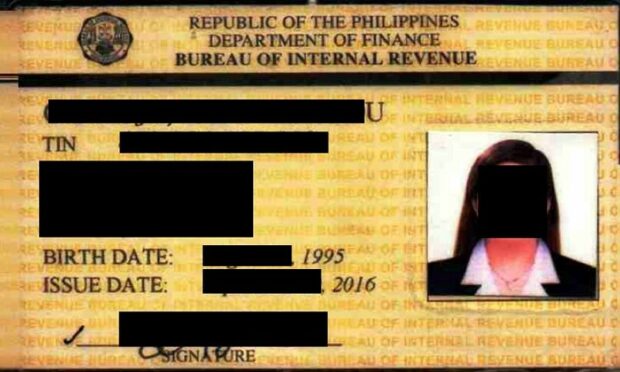
Sample of a criminologist accreditation, police clearance form, and BIR identification card, all available on the exposed database.
Internal directives addressing law enforcement officers were also exposed in the data breach.
“As an example, these would be orders from the top leadership of how to enforce what laws and what gets priority or additional training that is needed etc… I cannot further confirm or verify the accuracy or authenticity of these documents contained within this database. As such, I cannot guarantee that the contents of the documents are accurate or reliable,” writes cybersecurity researcher Jeremiah Fowler, who authored the report.
“Any data breach that exposes personal information belonging to police and members of law enforcement or other officials can be dangerous. Individuals whose data is exposed could be potential victims of identity theft, phishing attacks, and a range of other malicious activities,” stressed Fowler.
“The availability of government records in an unsecured database raises concerns about potential national security issues. The exposed records could also potentially allow criminals to target members of law enforcement for blackmail or other schemes,” he added.
This database was left exposed for a minimum of six weeks, according to the report. However, Fowler recommended that a full forensic audit be conducted to “fully understand the extent and impact of the breach.”
PNP Public Information Office Chief Rederico Maranan relayed to INQUIRER.net a message from Anti-Cybercrime Group Director Police Brig. Gen. Sidney Hernia, stating that the cybercrime unit is still conducting vulnerability assessment and penetration testing.