 InfoSecBulletin Cybersecurity for mankind
Over 1,200 firewall instances are vulnerable to a critical remote code execution issue, known as CVE-2024-52875. The vulnerability is found in several unauthenticated web interface paths, including /nonauth/addCertException.cs, /nonauth/guestConfirm.cs, and /nonauth/expiration.cs.
These pages do not adequately sanitize user input from the dest GET parameter, allowing attackers to inject line feed (LF) characters into HTTP responses. This vulnerability can lead to HTTP response splitting attacks, resulting in open redirects and reflected cross-site scripting (XSS).
Microsoft’s November 2026 Patch Tuesday addresses 1,093 flaws, with Outlook zero-day

Barracuda ESG flaws exploited, gaining root access

Apple, SAP, and Ivanti Patch Critical flaws Affecting Messaging, Bluetooth, and Enterprise Systems

Jailbroken DeepSeek AI Agent Conducts Two-Week Cyberattack on European Telecom

Daily Cyber security update for 10.11. 2026

IBM fixes 208 API Connect vulnerabilities, 47 critical

89 New ransomware groups emerge in 2026, claiming over 2,200 victims

Daily Cyber security update for 08.11. 2026

Japan banking crisis
Outage causes disruption at 128 japan banks: preventing ATM transaction

Daily Cyber security update for 06.11. 2026

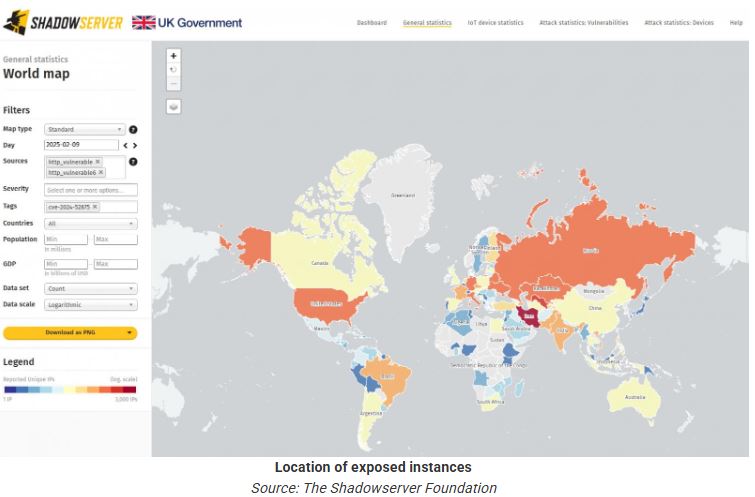
As of February 9, 2025, the Shadowserver Foundation reported 12,229 unpatched KerioControl instances worldwide. A heatmap from Shadowserver shows significant vulnerabilities in North America, Europe, and Asia.
The organization has identified scanning for this vulnerability in its honeypot sensors, showing that threat actors are attempting to exploit it.
The absence of an official warning from the National Vulnerability Database (NVD) makes it harder to address risks. Organizations using these firewalls may not recognize the threat until a breach occurs or they are alerted by third-party security monitors like Shadowserver.
Unpatched KerioControl firewalls are vulnerable to attacks that allow hackers to gain full control. Exploited firewalls can become entry points for larger network intrusions or for launching additional attacks on connected systems.
In mid-December, security researcher Egidio Romano (EgiX) found the flaw that could enable risky 1-click remote code execution (RCE) attacks.
Shadowserver advises organizations to quickly assess their system vulnerabilities, monitor dashboards for alerts, and apply available patches.
KerioControl is a network security suite that small and medium-sized businesses use for VPNs, bandwidth management, reporting and monitoring, traffic filtering, AV protection, and intrusion prevention.
Apple releases update of zero-day vuln exploited in the Wild



