Saturday , October 24 2026
NVIDIA

NVIDIA has released update for NVIDIA Riva

NVIDIA has released a software update for Riva to fix security vulnerabilities that could allow privilege escalation, data tampering, denial of service, or information disclosure.

NVIDIA Riva is a suite of GPU-accelerated microservices for multilingual speech and translation, designed for creating customizable, real-time conversational AI systems. It features automatic speech recognition (ASR), text-to-speech (TTS), and neural machine translation (NMT) and can be used in various settings like cloud, data centers, edge, and embedded devices. Riva allows organizations to add speech and translation functions to large language models (LLMs) and retrieval-augmented generation (RAG), improving chatbots into multilingual assistants and avatars.

PHP shares new RCE flaw (CVE 2026-115560) with no patch but mitigation

The PHP security team shared ways to protect against a new flaw that lets someone run unwanted code on certain...
Read More
PHP shares new RCE flaw (CVE 2026-115560) with no patch but mitigation

US banks faced unauthorized access by AI agents in customer accounts: Axios reports

Major US banks have detected unauthorized access to customer accounts by third-party AI agents, with some systems taking actions beyond...
Read More
US banks faced unauthorized access by AI agents in customer accounts: Axios reports

Atlassian patched 176 flaw in Jira and Confluence: Fortinet Urges to Patch Flaws Affecting FortiOS, FortiManager

Fortinet has urged customers to prioritize security updates for FortiOS, FortiManager, and FortiAnalyzer scheduled for October 22, 2026. The coordinated...
Read More
Atlassian patched 176 flaw in Jira and Confluence: Fortinet Urges to Patch Flaws Affecting FortiOS, FortiManager

Hacker claim to access Rajasthan Police data: 70,000 records allegedly exposed

Hacker offers to sell Rajasthan Government’s Department of Information Technology & Communication (DoIT&C) data in a underground forum. The threat...
Read More
Hacker claim to access Rajasthan Police data: 70,000 records allegedly exposed

Update now! PHP2Shell: Critical PHP vulnerabilities patched

The PHP team released urgent security updates to fix PHP2Shell, two serious flaws (CVE-2026-109618 and CVE-2026-109619) that let attackers run...
Read More
Update now! PHP2Shell: Critical PHP vulnerabilities patched

Trump says data centres should pay dividends to local community

US President Donald Trump said on Wednesday that companies ​building data centers should pay a "dividend" to the communities ‌where...
Read More
Trump says data centres should pay dividends to local community

Hackers Actively Exploiting Palo Alto VPN Flaw Via CVE-2026-0257

Ransomware groups are using a flaw in Palo Alto Networks GlobalProtect VPN to get around multi-factor authentication and access corporate...
Read More
Hackers Actively Exploiting Palo Alto VPN Flaw Via CVE-2026-0257

DeepSeek AI banned by U.S. Government; federal agencies must remove all related tools

The U.S. Department of Homeland Security (DHS) ordered federal agencies to stop using DeepSeek products and remove it from all...
Read More
DeepSeek AI banned by U.S. Government; federal agencies must remove all related tools

CISA, NSA and NIST Publish New 10 AI Agent Control Guidelines

NSA, CISA, and NIST have released security guidelines to find, control, and stop AI agents that go beyond their allowed...
Read More
CISA, NSA and NIST Publish New 10 AI Agent Control Guidelines

Claude AI Cracks 25-Year NSA Cryptography Number Mystery in Just 30 Minutes

Anthropic says a Claude research model showed how the National Security Agency made seeds for five NIST elliptic curves in...
Read More
Claude AI Cracks 25-Year NSA Cryptography Number Mystery in Just 30 Minutes

The security update addresses improper access control issues. Details on the vulnerabilities and their impacts are provided below:

CVE-2025-23242: NVIDIA Riva has a vulnerability that allows improper access control, potentially leading to privilege escalation, data tampering, denial of service, or information disclosure. It has a severity rating of High, with a base score of 7.3.

CVE-2025-23243: NVIDIA Riva has a vulnerability that allows improper access control, potentially leading to data tampering or denial of service. It has a base score of 6.5 and is classified as High severity.

The affected product, its versions, and the updated version are:
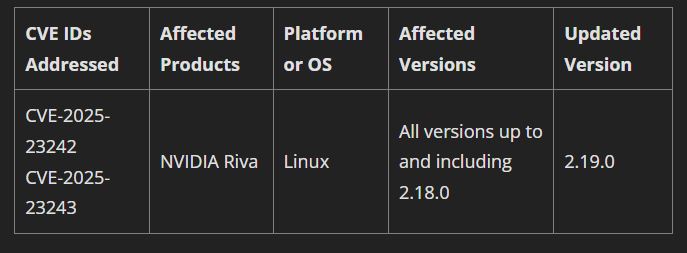
NVIDIA advises users to upgrade from earlier versions of Riva to the latest release.

NVIDIA thanks David Fiser and Alfredo Oliveira from Trend Micro’s Nebula team for reporting these issues.


Check Also

VPN

Hackers Actively Exploiting Palo Alto VPN Flaw Via CVE-2026-0257

Ransomware groups are using a flaw in Palo Alto Networks GlobalProtect VPN to get around …