InfoSecBulletin Cybersecurity for mankind
Hudson Researchers reported that on December 20th, ‘irleaks’ claimed to have 160 million records from 23 top insurance companies in Iran for sale.
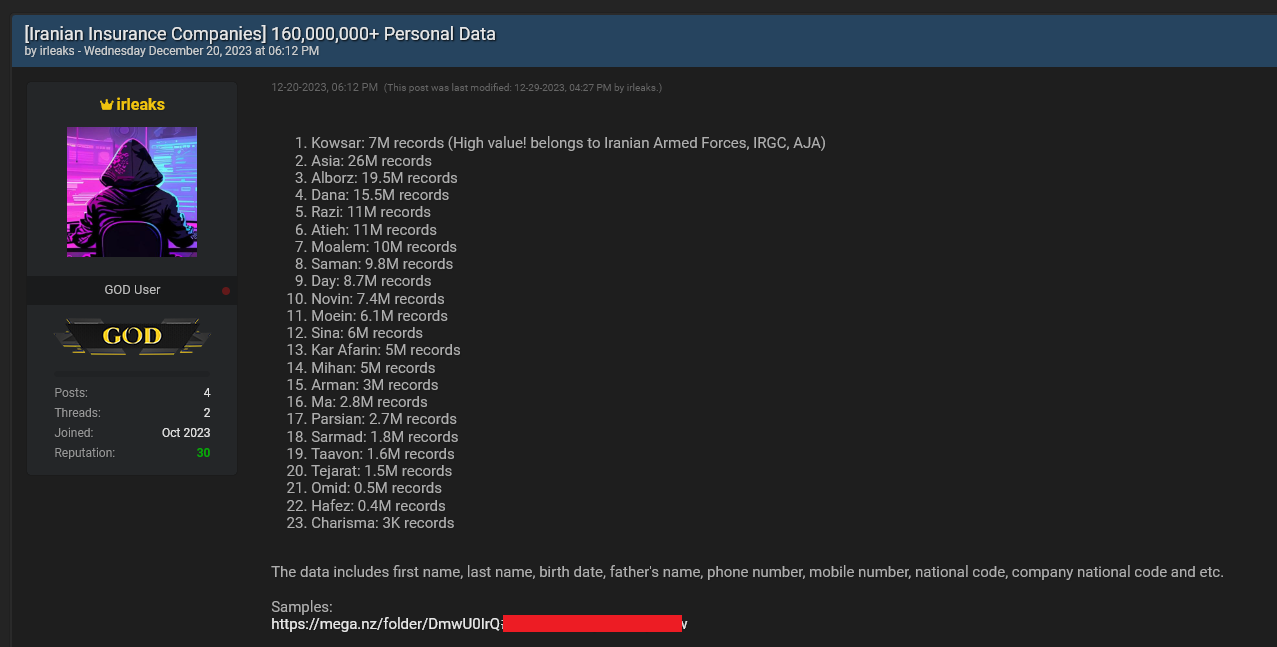
The hacker says they have stolen data like names, birth dates, phone numbers, national codes, and more. They have shared a sample of the data and want $60,000 for it.
Daily Cyber security update for 14.11. 2026

Huge European telecom leak exposes clients of Swedbank, SEB, airBaltic, and other companies

PHP2Shell attack exploited a Check Point 0-day to deploy malware

North Korean hackers steal more than $400 million using video images, FBI says

Microsoft’s November 2026 Patch Tuesday addresses 1,093 flaws, with Outlook zero-day

Barracuda ESG flaws exploited, gaining root access

Apple, SAP, and Ivanti Patch Critical flaws Affecting Messaging, Bluetooth, and Enterprise Systems

Jailbroken DeepSeek AI Agent Conducts Two-Week Cyberattack on European Telecom

Daily Cyber security update for 10.11. 2026

IBM fixes 208 API Connect vulnerabilities, 47 critical

The data contains personal information like names, phone numbers, ID numbers, addresses, passport numbers, and other sensitive details.
Researchers from Hudson Rock confirm that the data seems to be authentic and mention that carrying out an attack on this scale against numerous insurance companies is extremely challenging.
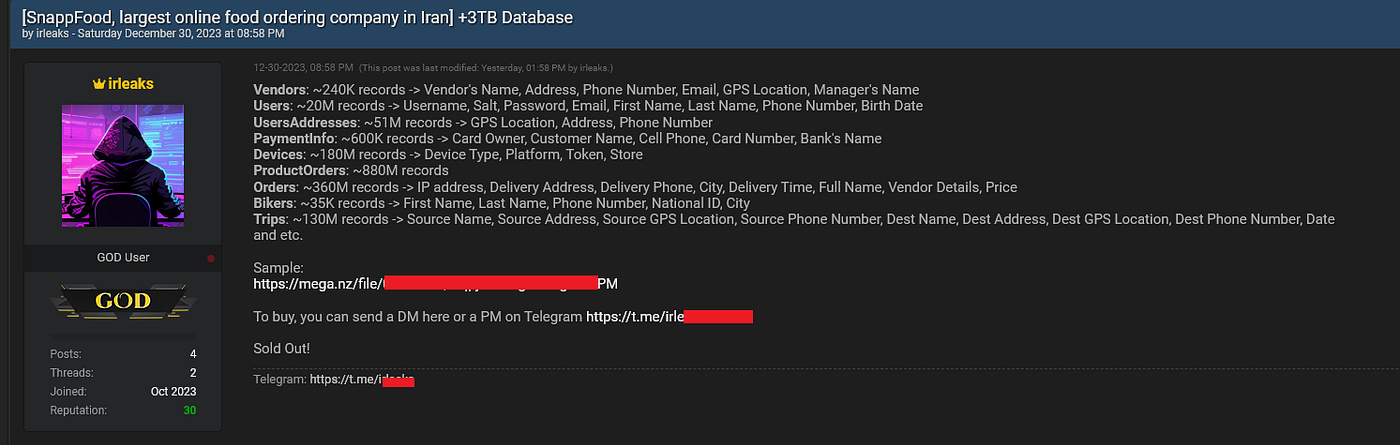
However, the breach wasn’t sufficient for “irleaks”. On December 30th, the threat actor posted another message claiming to have hacked SnappFood, Iran’s biggest online food ordering company.
The data that was apparently exfiltrated from the company amounts to a staggering 3 Terabytes, and includes incredibly sensitive details such as:
*20,000,000 users data (emails, passwords, phone numbers)
* 51,000,000 user addresses
* 600,000 credit cards data
* 180,000,000 device related information
SnappFood noticed the breach and quickly stated that they are investigating the attack.
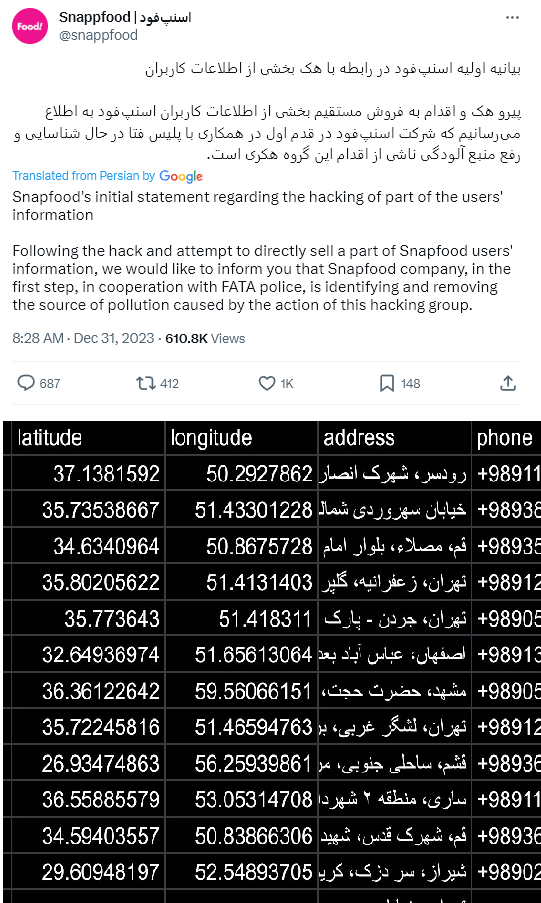
It is worth noting that although the origin of the breach is unknown, Hudson Rock researchers identified a recently compromised employee of SnappFood who had their computer infected with a StealC infostealer.
The infection of this employee’s computer resulted in many sensitive credentials of the organization being accessible to some hackers and may have been used as an initial attack vector against the company.
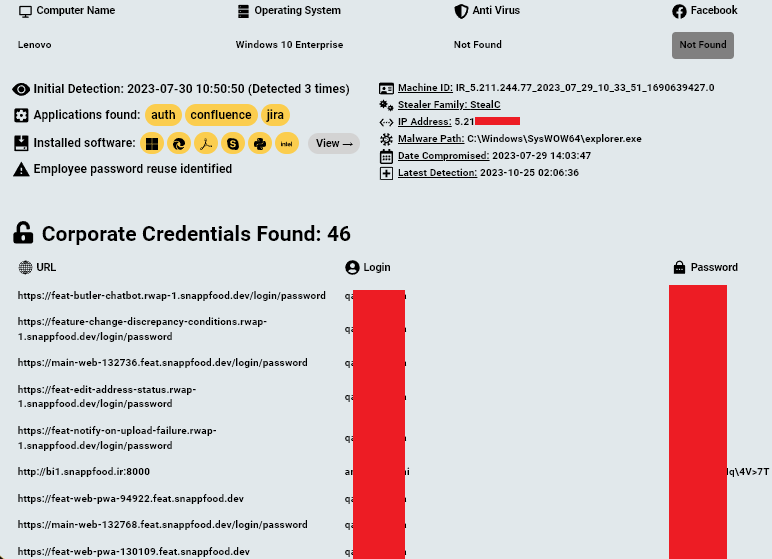
Some of the data includes login details to the company’s Confluence server, Jira server, and other development related URLs.
The combination of sophisticated attacks launched by a single threat actor against industry leading companies in Iran raises the question if this was a state-sponsored attack.