 InfoSecBulletin Cybersecurity for mankind
Citing the international media, various media outlets of the country have reported that various personal information including name, phone numbers, e-mail addresses and national identity numbers of millions of citizens of the country have been leaked from a website of the Bangladesh government.
In this regard, the government’s cyber issue management organization BGD e-GOV CIRT published a situational alert on Saturday (July 8). CIRT says, it is working regularly on data protection. This agency of the government regularly conducts cyber monitoring of various organizations through various means and provides them with necessary support.
Major Danish university breached, 200,000 users at risk

Microsoft’s X account hijacked to promote Clippy crypto scam

Critical cPanel, GitLab AI Gateway and Dell CSM Flaws Enable RCE And Admin Hijacking

Nearly 100,000 email addresses exposed in first AI-related data breach in Singapore

Hackers Exploit Zimbra Mail Servers: TeamViewer patched 5 critical flaws

Google Warns of Hackers Actively Exploiting Citrix 0-Day Flaws

CISA Warns Critical MikroTik RouterOS Flaw While Cisco SD-WAN Zero-Day Exploited in Attacks

Apple Zero-Day Exploited: Pentagon Data Breach Reportedly Exposes Sensitive Data of 3 Million People

JadePuffer Agentic AI targets and destroys Azure’s cloud resources

“InfoSecCon-2026: Bangladesh’s Cybersecurity Leaders Unite to Shape a Safer Digital Future”

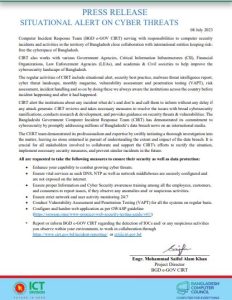
CIRT says that they are working on the issue of data leakage recently.
CIRT statement as follow:
Computer Incident Response Team (BGD e-GOV CIRT) is serving with responsibilities to computer security incidents and activities in the territory of Bangladesh close collaboration with international entities keeping risk-free the cyberspace of Bangladesh.
CIRT also works with various Government Agencies, Critical Information Infrastructures (CII), Financial Organizations, Law Enforcement Agencies (LEAs), and academia & Civil societies to help improve the cyber security landscape of Bangladesh.
The regular activities of CIRT include situational alert, security best practice, malware threat intelligence report, cyber threat landscape, monthly magazine, vulnerability assessment and penetration testing (VAPT), risk assessment, incident handling and so on by doing these we always aware the institutions across the country before incident happening and after it had happened.
CIRT alert the institutions about any incident what do’s and don’ts and call them to inform without any delay if any attack generate. CIRT reviews and takes necessary measures to resolve the issues with broad cyber security ramifications, conducts research & development, and provides guidance on security threats & vulnerabilities. The Bangladeshi Government Computer Incident Response Team (CIRT) has demonstrated its commitment to cyber security by promptly addressing millions of Bangladeshi’s data breach news on an international media.
The CERT team demonstrated its professionalism and expertise by swiftly initiating a thorough investigation into the matter, leaving no stone unturned in pursuit of understanding the extent and impact of the data breach. It is crucial for all stakeholders involved to collaborate and support the CIRT’s efforts to rectify the situation, implement necessary security measures, and prevent similar incidents in the future.
All are requested to take the following measures to ensure their security as well as data protection:
- Enhance your capability to combat growing cyber threats.
- Ensure vital services as such DNS, NTP as well as network middleboxes are securely configured and are not exposed on the internet.
- Ensure proper Information and Cyber Security awareness training among all the employees, customers, and consumers to report issues, if they observe any anomalies and/ or suspicious activities.
- Ensure strict network and user activity monitoring 24/7
- Conduct Vulnerability Assessment and Penetration Testing (VAPT) for all the systems on regular basis.
- Configure and harden web application as per OWASP guideline
(https://onwasp.onrg/www-pronject-web-security-testing-guide/v41/)
- Report or inform BGD e-GOV CIRT regarding the detection of IOCs and/ or any suspicious activities you observe within your environment, to work in collaboration through https://www.cirt.gov.bd/incident-reporting/ or [email protected]



