 InfoSecBulletin Cybersecurity for mankind
LockBit restarted their ransomware operation on a new infrastructure after law enforcement disrupted their servers. Now, they threat to target the government sector more with their attacks.
The gang posted a long message admitting their negligence and sharing their future plans. “Due to my personal negligence and irresponsibility I relaxed and did not update PHP in time.” The threat actor says that the victim’s admin and chat panels server and the blog server were running PHP 8.1.2 and were likely hacked using a critical vulnerability tracked as CVE-2023-3824.
Jailbroken DeepSeek AI Agent Conducts Two-Week Cyberattack on European Telecom

Daily Cyber security update for 10.11. 2026

IBM fixes 208 API Connect vulnerabilities, 47 critical

89 New ransomware groups emerge in 2026, claiming over 2,200 victims

Daily Cyber security update for 08.11. 2026

Japan banking crisis
Outage causes disruption at 128 japan banks: preventing ATM transaction

Daily Cyber security update for 06.11. 2026

Cyber attack causes French bank Credit Mutuel Arkea €100 million missing

OpenAI AI Pipeline Discovers 948 Linux Kernel Privilege Escalation Flaws in 30 Hours

Bangladeshi Researcher Rasel Earns First Apple CVE Recognition for Model I/O Flaw

LockBit ransomware continues attacks:
On Saturday, the gang said it was restarting its ransomware business and acknowledged that their carelessness led to law enforcement stopping its activity in Operation Cronos.
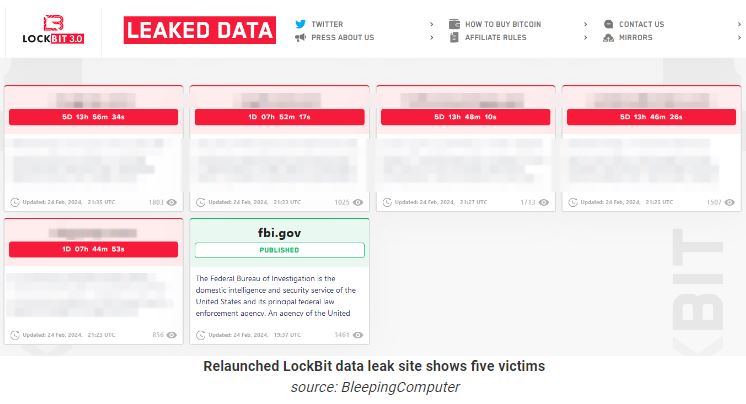
Keeping their name as usual, LockBit moved its data leak site to a new .onion address where five new victims name disclosed.
6 days back, “Operation Cronos” was led by the UK’s National Crime Agency (NCA) with support from Europol, Eurojust, and global law enforcement agencies. The task force was able to take control of 34 servers that made up LockBit’s primary platform, as well as 14,000 accounts used by the group to host tools and store data stolen from victims. The operation also seized 200 crypto-wallets and 1,000 decryption keys which were used to develop a decryptor tool that is now available to the public.



