 InfoSecBulletin Cybersecurity for mankind
The Akira ransomware operation uses a Linux encryptor to encrypt VMware ESXi virtual machines in double-extortion attacks against companies worldwide.
Akira first emerged in March 2023, targeting Windows systems in various industries, including education, finance, real estate, manufacturing, and consulting.
Barracuda ESG flaws exploited, gaining root access

Apple, SAP, and Ivanti Patch Critical flaws Affecting Messaging, Bluetooth, and Enterprise Systems

Jailbroken DeepSeek AI Agent Conducts Two-Week Cyberattack on European Telecom

Daily Cyber security update for 10.11. 2026

IBM fixes 208 API Connect vulnerabilities, 47 critical

89 New ransomware groups emerge in 2026, claiming over 2,200 victims

Daily Cyber security update for 08.11. 2026

Japan banking crisis
Outage causes disruption at 128 japan banks: preventing ATM transaction

Daily Cyber security update for 06.11. 2026

Cyber attack causes French bank Credit Mutuel Arkea €100 million missing

Since launching, the ransomware operation has claimed over 30 victims in the United States alone, with two distinct activity spikes in ID Ransomware submissions at the end of May and the present.
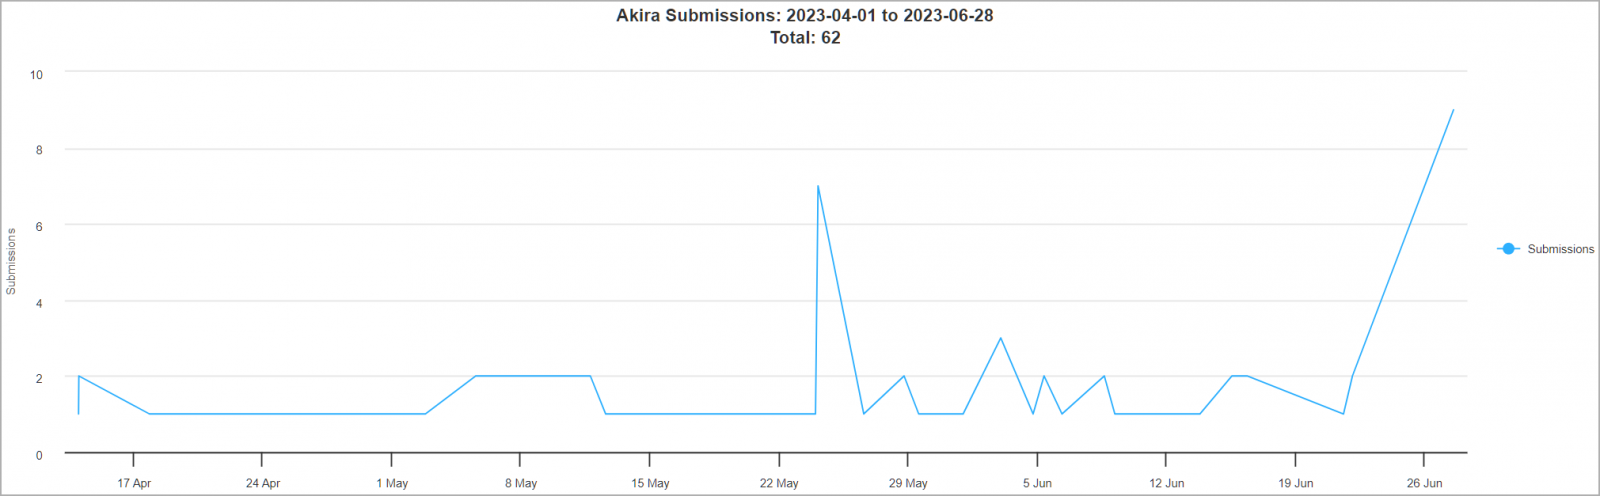
Source: BleepingComputer
Akira targets VMware ESXi
The Linux version of Akira was first discovered by malware analyst rivitna, who shared a sample of the new encryptor on VirusTotal last week.
BleepingComputer’s analysis of the Linux encryptor shows it has a project name of ‘Esxi_Build_Esxi6,’ indicating the threat actors designed it specifically to target VMware ESXi servers.
For example, one of the project’s source code files is /mnt/d/vcprojects/Esxi_Build_Esxi6/argh.h.
Over the past few years, ransomware gangs have increasingly created custom Linux encryptors to encrypt VMware ESXi servers as the enterprise moved to use virtual machines for servers for improved device management and efficient use of resources.
By targeting ESXi servers, a threat actor can encrypt many servers running as virtual machines in a single run of the ransomware encryptor.
However, unlike other VMware ESXi encryptors analyzed by BleepingComputer, Akira’s encryptors do not contain many advanced features, such as the automatic shutting down of virtual machines before encrypting files using the esxcli command.
With that said, the binary does support a few command line arguments that allow an attacker to customize their attacks:
- -p –encryption_path (targeted file/folder paths)
- -s –share_file (targeted network drive path)
- – n –encryption_percent (percentage of encryption)
- –fork (create a child process for encryption)
The -n parameter is particularly notable as it allows attackers to define how much data is encrypted on each file.
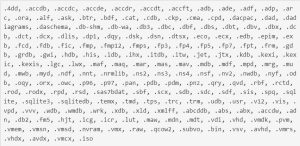
When encrypting files, the Linux Akira encryptor will target the following extensions:
Strangely, the Linux locker appears to skip the following folders and files, all related to Windows folders and executables, indicating that the Linux variant of Akira was ported from the Windows version.

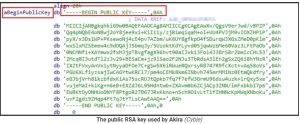
Cyble’s analysts, who also published a report about the Linux version of Akira today, explain that the encryptor includes a public RSA encryption key and leverages multiple symmetric key algorithms for the file encryption, including AES, CAMELLIA, IDEA-CB, and DES.
The symmetric key is used to encrypt the victims’ files and is then encrypted with the RSA public key. This prevents access to the decryption key unless you have the RSA private decryption key only held by the attackers.
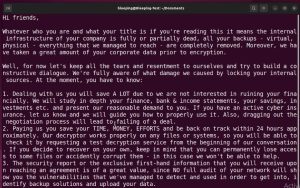
Encrypted files with be renamed to have the .akira extension, and a hardcoded ransom note named akira_readme.txt will be created in each folder on the encrypted device.
The expansion of Akira’s targeting scope is reflected in the number of victims announced by the group recently, which only makes the threat more severe for organizations worldwide.
Unfortunately, adding Linux support is a growing trend among ransomware groups, with many using readily-available tools to do it, as this is an easy and almost foolproof way to increase profits.
Other ransomware operations that utilize Linux ransomware encryptors, with most targeting VMware ESXi, include Royal, Black Basta, LockBit, BlackMatter, AvosLocker, REvil, HelloKitty, RansomEXX, and Hive.
Source: Bleepingcomputer



