 InfoSecBulletin Cybersecurity for mankind

LightSpy mobile espionage campaign, which focuses on targets in Southern Asia and probably India, potentially indicating a renewed focus and grow tensions in the region.
VirusTotal submissions from India suggest potential victims within its borders, aligning with recent warnings by Apple on detections within the same country.
Daily Cyber security update for 14.11. 2026

Huge European telecom leak exposes clients of Swedbank, SEB, airBaltic, and other companies

PHP2Shell attack exploited a Check Point 0-day to deploy malware

North Korean hackers steal more than $400 million using video images, FBI says

Microsoft’s November 2026 Patch Tuesday addresses 1,093 flaws, with Outlook zero-day

Barracuda ESG flaws exploited, gaining root access

Apple, SAP, and Ivanti Patch Critical flaws Affecting Messaging, Bluetooth, and Enterprise Systems

Jailbroken DeepSeek AI Agent Conducts Two-Week Cyberattack on European Telecom

Daily Cyber security update for 10.11. 2026

IBM fixes 208 API Connect vulnerabilities, 47 critical

Technical Details:
Infection vector:
Based on previous campaigns, initial infection likely occurs through compromised news websites carrying stories related to Hong Kong.
Weaponization:
The attack involves a first-stage implant that gathers device information and downloads further stages, including the core LightSpy implant and various plugins for specific spying functions.
Execution Chain:
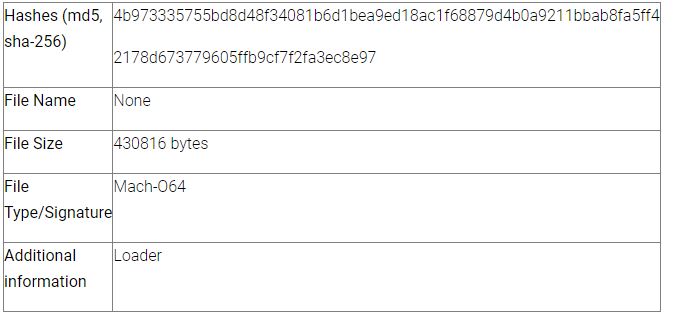
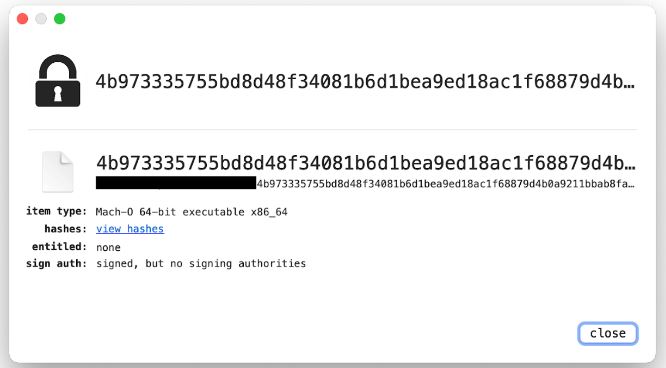
The Loader starts by loading the encrypted and then decrypted LightSpy kernel. LightSpy is an espionage framework with a plugin system. The Loader loads these plugins, which extend the main LightSpy implant. The plugins are securely retrieved from the threat actor’s server in an encrypted format, decrypted, and then executed in the system environment.

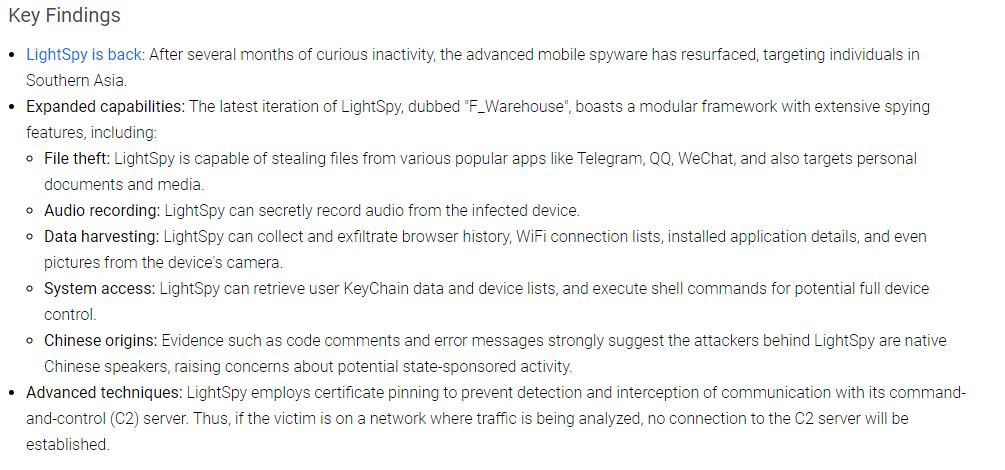
The latest LightSpy campaign utilizes a versatile framework known as “F_Warehouse.” This framework exhibits a wide range of capabilities, enabling it to:
Exfiltrate files: Systematically search and steal files from the compromised mobile device.
Record audio: Covertly capture audio through the device’s microphone.
Perform network reconnaissance: Collect information about WiFi networks the device has connected to.
Track user activity: Harvest browsing history data to monitor online behavior.
Application inventory: Gather details about installed applications on the device.
Capture images: Secretly take pictures using the device’s camera.
Access credentials: Retrieve sensitive data stored within the user’s KeyChain.
Device enumeration: Identify and list devices connected to the compromised system. To read the full report click here.



