 InfoSecBulletin Cybersecurity for mankind
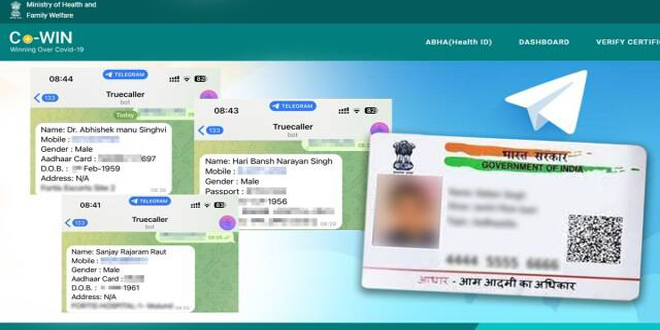
Several Indian media report that a massive data breach of the CoWIN portal (The central platform for COVID-19 vaccination registration in India) had happened.
Microsoft’s November 2026 Patch Tuesday addresses 1,093 flaws, with Outlook zero-day

Barracuda ESG flaws exploited, gaining root access

Apple, SAP, and Ivanti Patch Critical flaws Affecting Messaging, Bluetooth, and Enterprise Systems

Jailbroken DeepSeek AI Agent Conducts Two-Week Cyberattack on European Telecom

Daily Cyber security update for 10.11. 2026

IBM fixes 208 API Connect vulnerabilities, 47 critical

89 New ransomware groups emerge in 2026, claiming over 2,200 victims

Daily Cyber security update for 08.11. 2026

Japan banking crisis
Outage causes disruption at 128 japan banks: preventing ATM transaction

Daily Cyber security update for 06.11. 2026

For this breach media report one billion Indian citizens’ data is at risk. This data leak has also exposed the Aadhaar card, Voter ID, and PAN Card numbers of thousands of Indian citizens, rendering them accessible to anyone on Telegram.
Some famous Indian politician has shared the leaked data screenshot. Saket Gokhale wrote his tweeter handle :
“There has been a major data breach of Modi Govt where personal details of all vaccinated Indians including their mobile nos., Aadhaar numbers, Passport numbers, Voter ID, Details of family members etc. have been leaked & are freely available.”
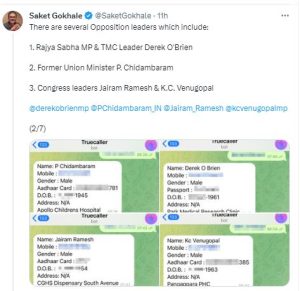
He placed some famous person’s personal detail:
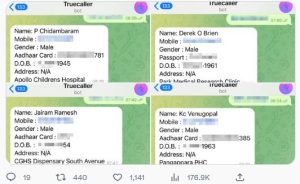
There are several Opposition leaders which include: 1. Rajya Sabha MP & TMC Leader Derek O’Brien 2. Former Union Minister P. Chidambaram 3. Congress leaders Jairam Ramesh & K.C. Venugopal
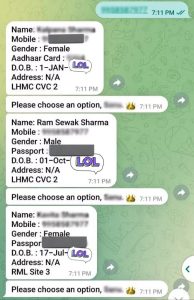
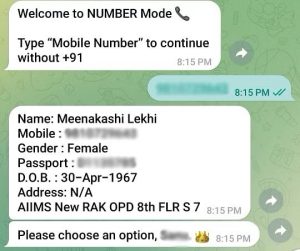
The CoWIN data breach doesn’t stop here. Various news reports have confirmed that if multiple individuals had registered from the same mobile number, the Telegram bot would reveal the details of all individuals in one go.
This means that if a family had booked vaccine slots for multiple members using the same mobile number, their personal information would be exposed collectively.
Media report personal identification information of several top political leaders including India’s Former Union Minister P. Chidambaram, Secretary of the Union Health Ministry, Rajesh Bhushan and his wife, Ritu Khanduri Bhushan who is a Member of the Legislative Assembly from Uttarakhand, Central opposition leaders Jairam Ramesh and K.C. Venugopal, have been exposed.
While the CoWIN portal supposedly had a One Time Password (OTP) security system, it remains unclear how this data leak occurred on Telegram.
However, hours after reports of the alleged CoWIN data breach surfaced, the Indian government refuted the claims stating that the Health Ministry’s CoWIN platform was “completely safe”.
“Certain posts on the social media platform Twitter have claimed using a Telegram (online messenger application) BOT, the personal data of individuals who have been vaccinated is being accessed. It is reported that the BOT has been able to pull individual data by simply passing the mobile number or Aadhaar number of a beneficiary.”
Calling such reports “without any basis” and “mischievous in nature”, the ministry clarified that the CoWIN portal was “completely safe with adequate safeguards for data privacy”.
Elaborating on the security measure, the statement read, “There are security measures in place on Co-WIN portal, with Web Application Firewall, Anti-DDoS, SSL/TLS, regular vulnerability assessment, Identity & Access Management etc. Only OTP authentication-based access of data is provided.
The statement further explained that the development team of COWIN confirmed that there were no public APIs where data can be pulled without an OTP. However, elaborated that one such API had a feature of sharing the data by calling using just a mobile number of Aadhaar.
“However, even this API is very specific and the requests are only accepted from a trusted API which has been white-listed by the CoWIN application,” the statement read.
Following the speculations around the alleged CoWIN data breach, the Union Health Ministry requested the Indian Computer Emergency Response Team (CERT-In) to investigate the issue and submit the report.
However, the initial report by CERT-In noted that the backend database for Telegram bot was not directly accessing the APIs of CoWIN database.
An internal probe to review the existing security measures of CoWIN has also been initiated.
Eng. Md. Saiful Alam Khan told Infosecbulletin.com that “We are aware of it, the “Surokkha” platform is now totally safe, no abnormal something is found. Though our system is safe, from user end there is always to be cautious.”



