 InfoSecBulletin Cybersecurity for mankind
OpenAI has neutralized over 20 malicious cyber operations using its AI chatbot, ChatGPT, for creating malware, spreading misinformation, avoiding detection, and spear-phishing.
The report confirms that since the start of the year, generative AI tools are being used to improve offensive cyber operations. OpenAI’s latest report reveals that Chinese and Iranian threat actors are misusing ChatGPT to improve their operations.
Hacker claim to access Rajasthan Police data: 70,000 records allegedly exposed

Update now! PHP2Shell: Critical PHP vulnerabilities patched

Trump says data centres should pay dividends to local community

Hackers Actively Exploiting Palo Alto VPN Flaw Via CVE-2026-0257

DeepSeek AI banned by U.S. Government; federal agencies must remove all related tools

CISA, NSA and NIST Publish New 10 AI Agent Control Guidelines

Claude AI Cracks 25-Year NSA Cryptography Number Mystery in Just 30 Minutes

Bypassing firewalls, AI Agents Accessed Indian ‘ Data Without Permission: CERT-In

MITRE ATT&CK v20 Unveils 9 New Attack Techniques On AI Exploits, MFA Bypass, and CAPTCHA Evasion

Hackers Exploit Fortinet Flaws to Deploy Stealthy PEERSTITCH Malware on FortiGate Firewalls

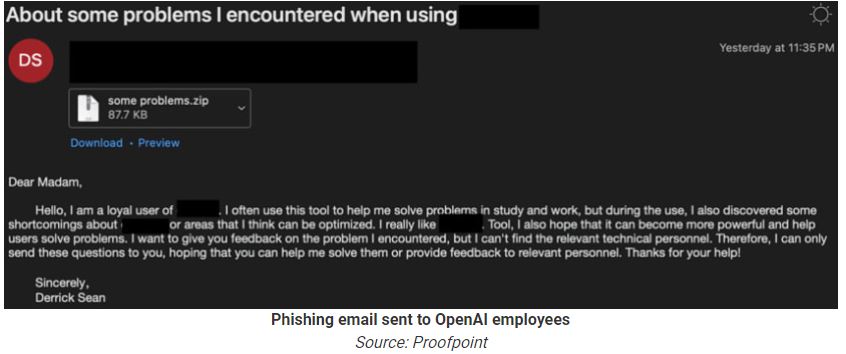
A Chinese threat group named “SweetSpecter” tried to use ChatGPT for research and malware creation. They also attempted spear-phishing attacks on OpenAI employees. Opening the attachments initiated an infection that installed the SugarGh0st RAT on the victim’s system.
The Iranian group “CyberAv3ngers,” linked to the Islamic Revolutionary Guard Corps, posed a serious threat by using ChatGPT to find weaknesses in industrial control systems and create attack scripts for critical infrastructure.
OpenAI reports that a threat group requested ChatGPT to generate default credentials for popular Programmable Logic Controllers (PLCs), create custom bash and Python scripts, and obfuscate code.
Iranian hackers used ChatGPT to plan their actions after compromising systems, learn to exploit vulnerabilities, and decide how to steal user passwords on macOS.
The third case in OpenAI’s report focuses on Storm-0817, a group of Iranian threat actors. The group allegedly used ChatGPT for various tasks, including debugging malware, creating an Instagram scraper, translating LinkedIn profiles into Persian, and developing custom Android malware with the necessary command and control infrastructure.
Malware developed using OpenAI’s chatbot can steal contact lists, call logs, files, take screenshots, access browsing history, and determine the user’s location.
“In parallel, STORM-0817 used ChatGPT to support the development of server side code necessary to handle connections from compromised devices,” reads the Open AI report.



