InfoSecBulletin Cybersecurity for mankind
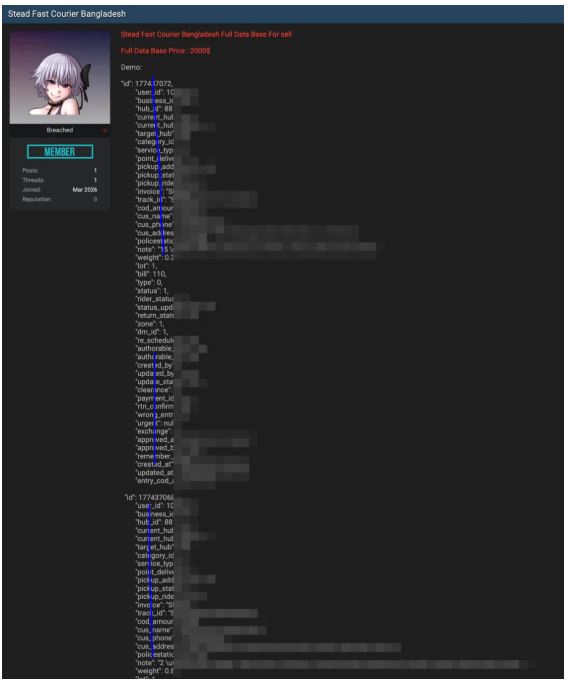
Steadfast Courier, a leading logistics and package delivery service operating in Bangladesh, has reportedly been compromised. The hacker offers to sell the full database of the company on a forum for $2,000.
The allegedly compromised data includes:
Cloudflare Unveils Emergency WAF Ruleset Update on Brotli flaw

Daily Cyber security update for 26.10. 2026

The Washington Post report
Ex-DOGE AI startup Cathedral Breaches Anthropic Internal Systems within 12 Hours

Daily Cyber security update for 25. 10. 2026

Daily Cyber security update for 24. 10. 2026

PHP shares new RCE flaw (CVE 2026-115560) with no patch but mitigation

US banks faced unauthorized access by AI agents in customer accounts: Axios reports

Atlassian patched 176 flaw in Jira and Confluence: Fortinet Urges to Patch Flaws Affecting FortiOS, FortiManager

Hacker claim to access Rajasthan Police data: 70,000 records allegedly exposed

Update now! PHP2Shell: Critical PHP vulnerabilities patched

Customer full names
Phone numbers
Detailed delivery addresses
Package tracking IDs
Cash-on-Delivery (COD) amounts
Invoice details
Hub and zone information
Shipment weights and creation dates
if the hacker claim is true, it may result in an identity theft and security risks for the customer.
Experts said, several systemic weaknesses are often observed across logistics and courier platforms:
Inadequate API authentication mechanisms: Many platforms use weak or poorly set up security controls, which raises the risk of unauthorized access to backend services and sensitive data.
Insufficient database access controls: Inadequate permissions and too many access rights can lead to unauthorized use of important databases.
Absence of robust encryption for sensitive data: Failure to use strong encryption for data in transit and at rest puts customer information at risk.
Security risks introduced by third-party integrations: Unverified tools, APIs, or services may create security holes, increasing the attack surface of logistics platforms.
(Media Disclaimer: This report is based on research conducted internally and externally using OSINT. The information provided here is for reference only, and users are responsible for referring and relying on it. Infosecbulletin is not liable for the accuracy or consequences of using this information by any means)