 InfoSecBulletin Cybersecurity for mankind
A threat actor claims to have breached Huawei Technologies Co., Ltd. (Huawei), a multinational technology company based in Shenzhen, China, that specializes in telecommunications equipment. The incident, which the actor states occurred in October 2025, allegedly resulted in the exfiltration of internal company data.
According to the actor, the compromised data is now being offered for sale. The breach appears to have exposed sensitive property, including source code and internal development tools. A file tree provided by the actor indicates the data includes:
CISA, NSA and NIST Publish New 10 AI Agent Control Guidelines

Claude AI Cracks 25-Year NSA Cryptography Number Mystery in Just 30 Minutes

Bypassing firewalls, AI Agents Accessed Indian ‘ Data Without Permission: CERT-In

MITRE ATT&CK v20 Unveils 9 New Attack Techniques On AI Exploits, MFA Bypass, and CAPTCHA Evasion

Hackers Exploit Fortinet Flaws to Deploy Stealthy PEERSTITCH Malware on FortiGate Firewalls

Hacker stole Meta GitHub repos; Stole Source Code

Urgent patch! Zoom,NVIDIA and IBM Patch 41 Security flaws

Microsoft patches record braking 1411 flaws; 2 zero days

Anthropic unveils “OSS Scanner” Free AI Vulnerability Scanner for Open-Source Projects

Rise on RCE Exploits Targeting Hikvision Camera Flaw

Source code files (e.g., .c, .cpp, .h, .pas)
Internal development tools and scripts
Build files and configurations (e.g., makefiles, .ini files)
Technical documentation and manuals
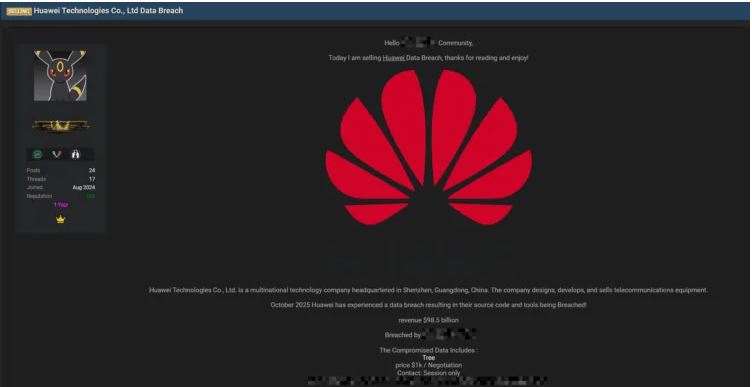
An image of the forum post shows the actor asking for $1,000, with the price open to negotiation, and communication restricted to the Session messaging platform.
According to INFOSEC FOX, Huawei Technologies Co., Ltd. has reportedly suffered a data breach, with a threat actor offering to sell company source code and internal tools.
Industry Response and Recommendations:
Huawei has not publicly commented on the alleged breach. Industry observers recommend:
Continuous Monitoring: Customers should intensify network monitoring for anomalies, especially around Huawei devices and management consoles.
Threat Intelligence Sharing: Organizations are encouraged to collaborate via information-sharing platforms to identify possible indicators of compromise related to Huawei code.
Patch Management: Ensure all Huawei products run the latest firmware and software updates, as these may contain mitigations for vulnerabilities potentially revealed by source code leaks.
Access Controls: Review and strengthen internal access policies to limit lateral movement in the event of similar breaches.
(Source: Darkweb, cybersecuritynews, cyberpress, INFOSEC F0X)
(Media Disclaimer: This report is based on research conducted internally and externally using different ways including open-source intelligence. The information provided here is for reference only, and users are solely responsible for referring and relying on it. Infosecbulletin is not liable for the accuracy or consequences of using this information by any means)



