Sunday , November 15 2026

Fortinet releases updates for Various Products

Fortinet has issued security updates for several products, including FortiOS, to fix vulnerabilities that could allow cyber attackers to take control of affected systems.

CISA encourages users and administrators to review the following advisories and apply necessary updates.

Daily Cyber security update for 14.11. 2026

Cyberattacks are rising around the world, including ransomware, malware, data leaks, and hacked websites. These events show how complex and...
Read More
Daily Cyber security update for 14.11. 2026

Huge European telecom leak exposes clients of Swedbank, SEB, airBaltic, and other companies

The Latvian part of CSCTelecom,  a telecommunications provider, made a database with over 125 million SMS messages public. The leaked...
Read More
Huge European telecom leak exposes clients of Swedbank, SEB, airBaltic, and other companies

PHP2Shell attack exploited a Check Point 0-day to deploy malware

Hackers used Check Point firewall flaws to get root access, insert backdoors, and install harmful malware on a VMware ESXi...
Read More
PHP2Shell attack exploited a Check Point 0-day to deploy malware

North Korean hackers steal more than $400 million using video images, FBI says

The United States Justice Department said Thursday it had seized cloud infrastructure used by North Korean hackers in a video-call...
Read More
North Korean hackers steal more than $400 million using video images, FBI says

Microsoft’s November 2026 Patch Tuesday addresses 1,093 flaws, with Outlook zero-day

Microsoft has shared its updates for November 2026. These updates fix 1,093 new flaws in Windows, Office, SQL Server, SharePoint,...
Read More
Microsoft’s November 2026 Patch Tuesday addresses 1,093 flaws, with Outlook zero-day

Barracuda ESG flaws exploited, gaining root access

Barracuda has confirmed active exploitation of security flaws affecting its Email Security Gateway (ESG), warning that attackers could combine two...
Read More
Barracuda ESG flaws exploited, gaining root access

Apple, SAP, and Ivanti Patch Critical flaws Affecting Messaging, Bluetooth, and Enterprise Systems

Apple, SAP, and Ivanti have published security updates that fix several flaws with messaging, Bluetooth, enterprise servers, and endpoint management...
Read More
Apple, SAP, and Ivanti Patch Critical flaws Affecting Messaging, Bluetooth, and Enterprise Systems

Jailbroken DeepSeek AI Agent Conducts Two-Week Cyberattack on European Telecom

A jailbroken AI has been attacking a European telecom company and 13 companies using its data center and cloud for...
Read More
Jailbroken DeepSeek AI Agent Conducts Two-Week Cyberattack on European Telecom

Daily Cyber security update for 10.11. 2026

Cyberattacks are rising around the world, including ransomware, malware, data leaks, and hacked websites. These events show how complex and...
Read More
Daily Cyber security update for 10.11. 2026

IBM fixes 208 API Connect vulnerabilities, 47 critical

IBM patched 208 security flaws in its API Connect platform. The CVE records released out on November 7, 2026. Among...
Read More
IBM fixes 208 API Connect vulnerabilities, 47 critical

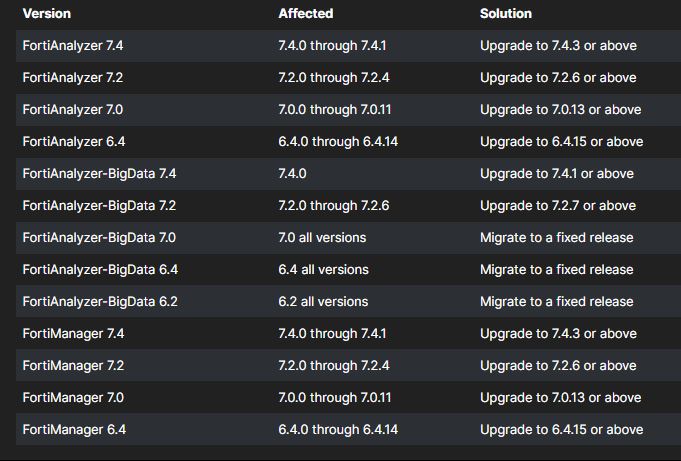
FG-IR-23-396 ReadOnly Users Could Run Some Sensitive Operations:

A client-side enforcement of server-side security vulnerability [CWE-602] in FortiAnalyzer may allow an authenticated attacker with at least read-only permission to execute sensitive operations via crafted requests.
  Source: fortiguard.com

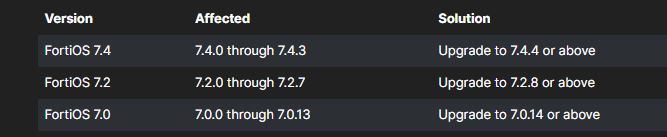
FG-IR-23-475 FortiOS – SSLVPN Session Hijacking Using SAML Authentication:

A session fixation vulnerability [CWE-384] in FortiOS may allow an unauthenticated attacker to hijack user session via a phishing SAML authentication link.
Source: Fortiguard.com

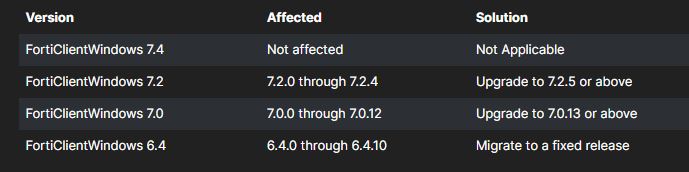
FG-IR-24-144 Privilege Escalation via Lua Auto Patch Function:

A privilege context switching error vulnerability [CWE-270] in FortiClient Windows may allow an authenticated user to escalate their privileges via lua auto patch scripts.
Source: fortiguard.com

FG-IR-24-199 Named Pipes Improper Access Control:

An authentication bypass using an alternate path or channel vulnerability (CWE-288) in FortiClient (Windows) may allow a low privilege attacker to execute arbitrary code with high privilege via spoofed named pipe messages.
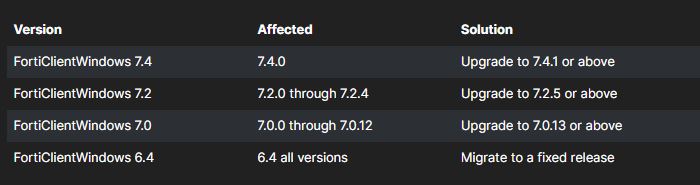

Source: fortiguard.com

Check Also

Anthropic

Anthropic’s Claude Code Source Code Reportedly Leaked

Anthropic’s special Claude Code CLI tool had its complete TypeScript source code inadvertently exposed due …