 InfoSecBulletin Cybersecurity for mankind
AMD has released a security bulletin about three possible vulnerabilities in its Secure Encrypted Virtualization – Secure Nested Paging (SEV-SNP) technology.
A researcher found vulnerabilities that could let a malicious hypervisor controlled by the host system access or modify the memory of a guest VM. This poses big risks to data security. The vulnerabilities are known as CVE-2024-21978, CVE-2024-21980, and CVE-2023-31355, with two rated as medium severity and one as high.
Japan banking crisis
Outage causes disruption at 128 japan banks: preventing ATM transaction

Daily Cyber security update for 06.11. 2026

Cyber attack causes French bank Credit Mutuel Arkea €100 million missing

OpenAI AI Pipeline Discovers 948 Linux Kernel Privilege Escalation Flaws in 30 Hours

Bangladeshi Researcher Rasel Earns First Apple CVE Recognition for Model I/O Flaw

WinRAR, WordPress RCE flaw & Zyxel GS1900 Zero-Day exploited in the wild

Daily Cyber security update for 04.11. 2026

Daily Cyber security update for 03.11. 2026

Using ARTEX AI, Hacker to attack 200 Organizations Across 14 Countries

Amadeus cyber incident impacted “Cathay Pacific, Qantas, Japan, Malaysia, Korean & Asiana” Airlines

SEV-SNP is a security feature for virtual machines that encrypts their memory to protect them from malicious attacks. However, vulnerabilities have been found in this feature due to issues with input validation and write operation restrictions in the firmware. These vulnerabilities could potentially allow a malicious hypervisor to access or corrupt a guest VM’s memory.
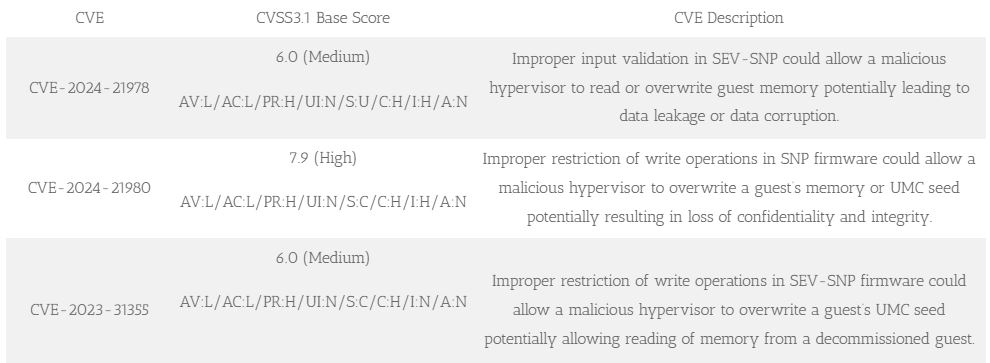
SEV-SNP firmware has a flaw that could let a malicious hypervisor overwrite a guest’s UMC seed, potentially allowing access to memory from a decommissioned guest.
These vulnerabilities are very important because they allow attackers to steal sensitive data, control VM operations, or even cause a denial of service. The affected products are AMD’s 3rd Gen EPYC Processors (Milan) and 4th Gen EPYC Processors (Genoa), which are commonly used in data centers and embedded systems.
To reduce the risks, AMD suggests that users update their systems with the latest Platform Initialization (PI) firmware versions mentioned in the advisory. In certain cases, there may be other options available for reducing the risks, like microcode or other patches.
For more information about firmware updates and how to protect your computer, please check the official AMD security bulletin and follow the guidelines.



