 InfoSecBulletin Cybersecurity for mankind
The 2024 Olympic Games in Paris are coming soon. A recent cybersecurity assessment by Outpost24, a provider of cyber threat exposure management solutions, has raised concerns about the online infrastructure of the games.
Outpost24 has identified critical vulnerabilities in the security posture, despite it being considered “mostly secure”. These vulnerabilities could be used by malicious actors. Here are the concerning findings:
CISA adds PHP2Shell to KEV, PHP Releases New Security Updates to Fix Critical HTTP2Shell flaw

Cloudflare Unveils Emergency WAF Ruleset Update on Brotli flaw

Daily Cyber security update for 26.10. 2026

The Washington Post report
Ex-DOGE AI startup Cathedral Breaches Anthropic Internal Systems within 12 Hours

Daily Cyber security update for 25. 10. 2026

Daily Cyber security update for 24. 10. 2026

PHP shares new RCE flaw (CVE 2026-115560) with no patch but mitigation

US banks faced unauthorized access by AI agents in customer accounts: Axios reports

Atlassian patched 176 flaw in Jira and Confluence: Fortinet Urges to Patch Flaws Affecting FortiOS, FortiManager

Hacker claim to access Rajasthan Police data: 70,000 records allegedly exposed


Open Ports:
Unsecured open ports can be exploited by hackers, leading to unauthorized access to important data and internal systems.
SSL Misconfigurations:
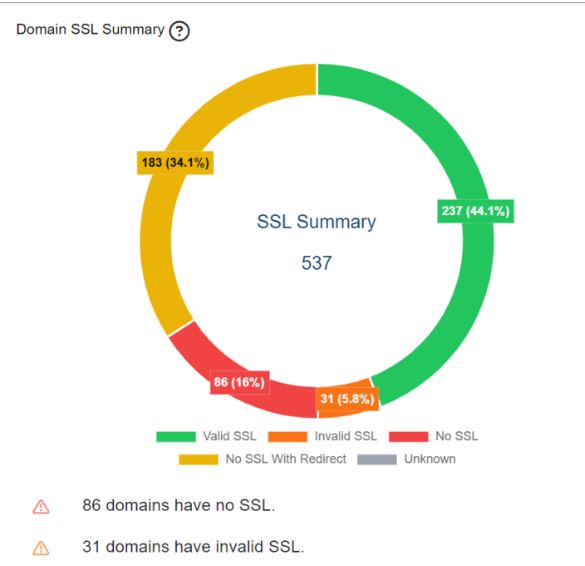
The report shows that 31 domains have bad SSL certificates, and 86 domains have no SSL certificates at all. These problems make the network vulnerable to attacks that can intercept communications and steal information. The report emphasizes the importance of better SSL certificate settings to prevent these attacks.
Cookie Consent Violations:
Websites associated with the Paris 2024 Olympics may not be obtaining proper user consent for cookie usage.
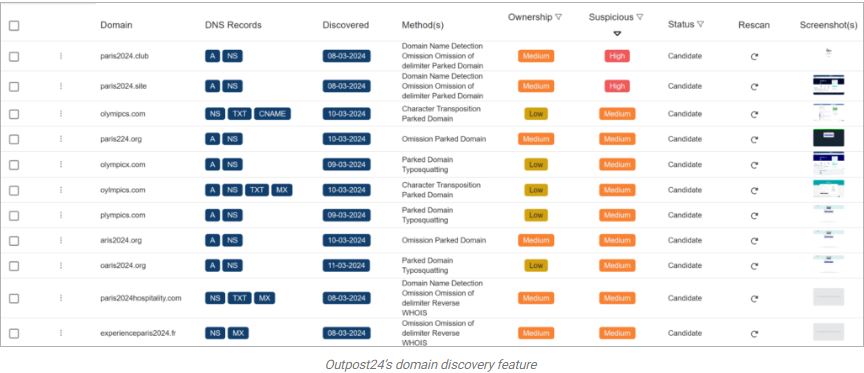
Domain Squatting:
The presence of deceptive domains can trick users into scams or malware attacks.
Potential Dangers:
The Paris 2024 Olympics are at risk of cyberattacks that can cause data breaches, disrupt operations, and damage reputation. These attacks can compromise athlete information, ticketing details, and financial data, posing privacy and security risks. Important systems like scorekeeping, broadcasting, and access control could be targeted, causing chaos and disruption during the Games.
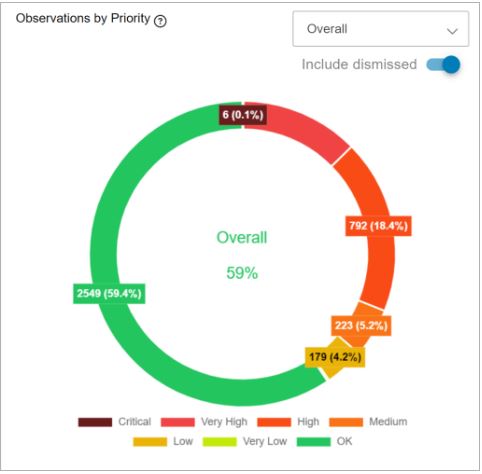
The report emphasizes the positive cybersecurity measures taken by the organizers of Paris 2024 but also emphasizes the need for careful monitoring of potential vulnerabilities.
“Even though we’d consider the Paris 2024 games as a ‘good’ example of how to manage an attack surface, it isn’t perfect (as perfection rarely exists with cybersecurity),” stated Outpost24’s EASM CSO, Stijn Vande Casteele.
The Paris 2024 Olympics are at risk of cybercrime due to increased online activity. Cybercriminals may try to exploit vulnerabilities to steal valuable information, similar to the 450 million cyberattacks during the 2020 Tokyo Olympics.
It is important to fix vulnerabilities and loopholes, patch open ports, correct SSL configurations, comply with cookie consent, and monitor suspicious domain activity to prevent cyberattacks.
(Media Disclaimer: This report is based on research conducted internally and externally using different ways. The information provided is for reference only, and users are responsible for relying on it. Infosecbulletin is not liable for the accuracy or consequences of using this information by any means)



