 InfoSecBulletin Cybersecurity for mankind
CISA has issued a critical alert about a critical vulnerability in Fortinet’s FortiOS and FortiProxy systems. CVE-2025-24472, an authentication bypass vulnerability, has been added to CISA’s Known Exploited Vulnerabilities catalog.
Fortinet FortiOS Authentication Bypass Vulnerability:
Daily Cyber security update for 14.11. 2026

Huge European telecom leak exposes clients of Swedbank, SEB, airBaltic, and other companies

PHP2Shell attack exploited a Check Point 0-day to deploy malware

North Korean hackers steal more than $400 million using video images, FBI says

Microsoft’s November 2026 Patch Tuesday addresses 1,093 flaws, with Outlook zero-day

Barracuda ESG flaws exploited, gaining root access

Apple, SAP, and Ivanti Patch Critical flaws Affecting Messaging, Bluetooth, and Enterprise Systems

Jailbroken DeepSeek AI Agent Conducts Two-Week Cyberattack on European Telecom

Daily Cyber security update for 10.11. 2026

IBM fixes 208 API Connect vulnerabilities, 47 critical

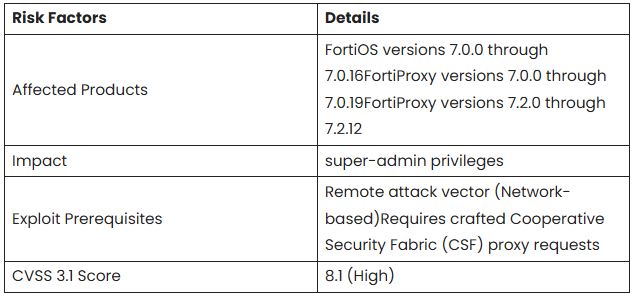
Fortinet FortiOS and FortiProxy contain an authentication bypass vulnerability that allows a remote attacker to gain super-admin privileges via crafted CSF proxy requests, which carries a CVSS score of 8.1.
The vulnerability affects FortiOS versions 7.0.0 to 7.0.16, FortiProxy 7.0.0 to 7.0.19, and FortiProxy 7.2.0 to 7.2.12.
Security experts caution that exploitation could give attackers full administrative access to systems, allowing them to create fake admin accounts, alter firewall policies, and reach SSL VPNs to access internal networks.
Mitigations:
CISA is directing organizations to “apply mitigations per vendor instructions, follow applicable BOD 22-01 guidance for cloud services, or discontinue use of the product if mitigations are unavailable”.
Fortinet has issued patches for vulnerabilities in FortiOS 7.0.17 and higher, as well as FortiProxy 7.0.20/7.2.13 and above.
The KEV catalog, managed by CISA, is a reliable source of known vulnerabilities actively exploited. CISA urges all organizations to prioritize fixing these Organizations should use the KEV catalog to prioritize their vulnerability management, as it is vital for effective external attack surface management and reducing compromise risks.



