 InfoSecBulletin Cybersecurity for mankind
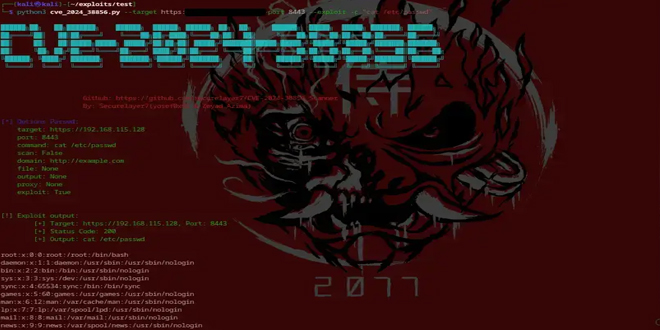
CISA issued a warning about a security flaw in Apache OFBiz, an ERP system. The vulnerability is being actively exploited and has been added to CISA’s Known Exploited Vulnerabilities catalog as CVE-2024-38856.
CVE-2024-38856 is a serious security flaw in Apache OFBiz. It allows attackers to run code on a remote server without authentication. To stay safe, organizations should update to Apache OFBiz version 18.12.15 or newer.
Daily Cyber security update for 14.11. 2026

Huge European telecom leak exposes clients of Swedbank, SEB, airBaltic, and other companies

PHP2Shell attack exploited a Check Point 0-day to deploy malware

North Korean hackers steal more than $400 million using video images, FBI says

Microsoft’s November 2026 Patch Tuesday addresses 1,093 flaws, with Outlook zero-day

Barracuda ESG flaws exploited, gaining root access

Apple, SAP, and Ivanti Patch Critical flaws Affecting Messaging, Bluetooth, and Enterprise Systems

Jailbroken DeepSeek AI Agent Conducts Two-Week Cyberattack on European Telecom

Daily Cyber security update for 10.11. 2026

IBM fixes 208 API Connect vulnerabilities, 47 critical

CVE-2024-38856 is a vulnerability in Apache OFBiz’s authentication mechanism. It allows unauthorized users to access functions only meant for logged-in users. By exploiting this vulnerability, attackers can run any code on compromised systems, possibly gaining full control.
SonicWall found and reported a critical vulnerability, CVE-2024-38856, in Apache OFBiz’s override view feature. This flaw allows unauthenticated attackers to access important parts of the system by sending specific requests.
Cybersecurity researchers Zeyad Azima from SecureLayer7 and Youssef Muhammad have posted a proof-of-concept (PoC) exploit code for CVE-2024-38856 on GitHub. This makes it easier for attackers to use the vulnerability in their attacks.
CISA strongly recommends that all federal agencies and organizations using Apache OFBiz update their installations to version 18.12.15 or later by September 17, 2024. Failing to apply these updates could lead to attacks and severe consequences.



