Wednesday , November 11 2026
Oracle

CIRT-in flags Critical Flaw in Oracle Agile PLM Framework

CERT-In has flagged a security vulnerability in Oracle’s Agile Product Lifecycle Management (PLM) software, identified as CVE-2024-21287 and cataloged as CIVN-2024-0350. This high-risk threat was detected on November 26, 2024.

CVE-2024-21287 affects Oracle Agile PLM Framework version 9.3.6, which is commonly used by organizations for managing product lifecycles and enhancing collaboration and development processes.

Barracuda ESG flaws exploited, gaining root access

Barracuda has confirmed active exploitation of security flaws affecting its Email Security Gateway (ESG), warning that attackers could combine two...
Read More
Barracuda ESG flaws exploited, gaining root access

Apple, SAP, and Ivanti Patch Critical flaws Affecting Messaging, Bluetooth, and Enterprise Systems

Apple, SAP, and Ivanti have published security updates that fix several flaws with messaging, Bluetooth, enterprise servers, and endpoint management...
Read More
Apple, SAP, and Ivanti Patch Critical flaws Affecting Messaging, Bluetooth, and Enterprise Systems

Jailbroken DeepSeek AI Agent Conducts Two-Week Cyberattack on European Telecom

A jailbroken AI has been attacking a European telecom company and 13 companies using its data center and cloud for...
Read More
Jailbroken DeepSeek AI Agent Conducts Two-Week Cyberattack on European Telecom

Daily Cyber security update for 10.11. 2026

Cyberattacks are rising around the world, including ransomware, malware, data leaks, and hacked websites. These events show how complex and...
Read More
Daily Cyber security update for 10.11. 2026

IBM fixes 208 API Connect vulnerabilities, 47 critical

IBM patched 208 security flaws in its API Connect platform. The CVE records released out on November 7, 2026. Among...
Read More
IBM fixes 208 API Connect vulnerabilities, 47 critical

89 New ransomware groups emerge in 2026, claiming over 2,200 victims

New ransomware actions in 2026 show more variety in cybercrime, with some groups claimed over 100 victims. The ransomware attack...
Read More
89 New ransomware groups emerge in 2026, claiming over 2,200 victims

Daily Cyber security update for 08.11. 2026

Cyberattacks are rising around the world, including ransomware, malware, data leaks, and hacked websites. These events show how complex and...
Read More
Daily Cyber security update for 08.11. 2026

Japan banking crisis
Outage causes disruption at 128 japan banks: preventing ATM transaction

A major system failure has brought customer-facing banking services to a standstill at 128 shinkin banks across western Japan, leaving...
Read More
Japan banking crisis  Outage causes disruption at 128 japan banks: preventing ATM transaction

Daily Cyber security update for 06.11. 2026

Cyberattacks are rising around the world, including ransomware, malware, data leaks, and hacked websites. These events show how complex and...
Read More
Daily Cyber security update for 06.11. 2026

Cyber attack causes French bank Credit Mutuel Arkea €100 million missing

French lender Credit Mutuel Arkea said on Thursday hackers had stolen around €100 million ($112.61 million) in a cyber heist...
Read More
Cyber attack causes French bank Credit Mutuel Arkea €100 million missing
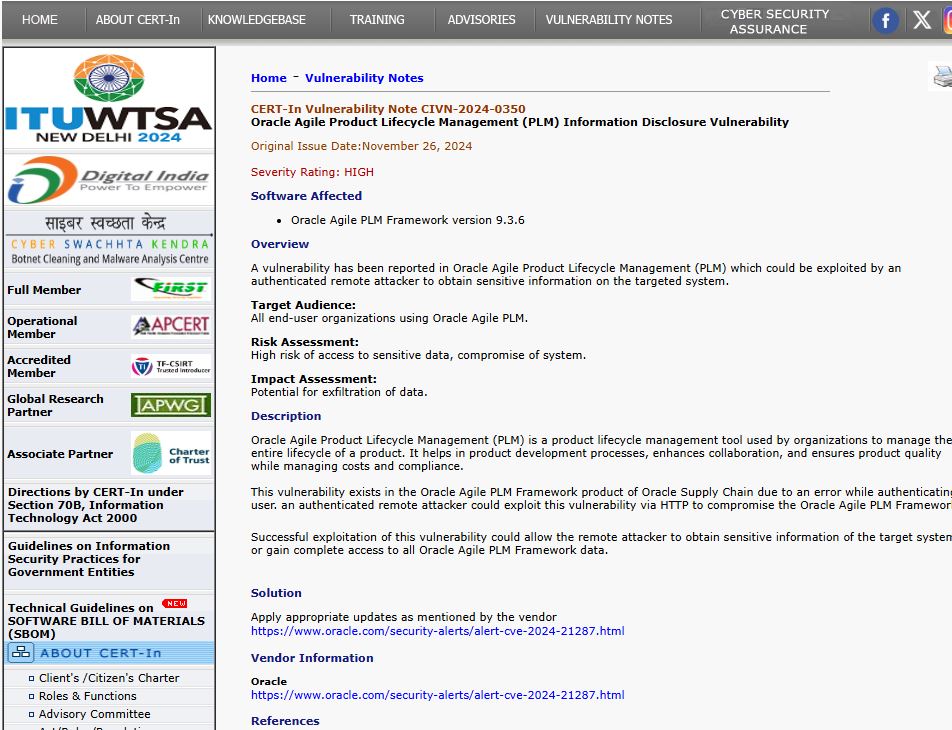
Screenshot from CIRT in website

This Security Alert highlights vulnerability CVE-2024-21287 in Oracle Agile Product Lifecycle Management (PLM). The vulnerability can be exploited remotely without authentication, meaning it can be targeted over a network without a username or password. Successful exploitation may lead to file disclosure.

Oracle Agile PLM is essential for managing product design, quality, and compliance within Oracle Supply Chain. A vulnerability exists due to improper authentication, allowing attackers to exploit the system through HTTP connections, potentially exposing sensitive information or compromising the system remotely.

CERT-In warns that the CVE-2024-21287 vulnerability could lead to data theft. Exploiting this flaw may allow attackers to access sensitive information for financial gain, industrial espionage, or operational sabotage.

Oracle’s Response:

Oracle advises customers to update to Agile PLM Framework version 9.3.6 with the latest security patches to fix a critical Information Disclosure Vulnerability and protect against unauthorized access and data leaks.


Check Also

API Connect

IBM fixes 208 API Connect vulnerabilities, 47 critical

IBM patched 208 security flaws in its API Connect platform. The CVE records released out …